Entitlement management is the identity governance (IGA) practice of defining, granting, reviewing, and removing the specific access rights that people, service accounts, and AI agents hold inside applications and data systems. It ensures every entitlement has an owner, a business reason, and an expiration path, so access stays aligned with least privilege and audit requirements.
See how C1.ai automates entitlement management →
What is entitlement management?#
Entitlement management sits at the center of identity governance and administration (IGA). Access management decides whether a user can log in. Entitlement management decides what that user can do once they are inside: which Salesforce profile they hold, which GitHub repositories they can push to, which AWS accounts they can assume roles in.
What are entitlements?#
Entitlements are access rights, permissions, or privileges to resources in an application. Common examples include:
- Membership to a group, such as an Okta or Entra group
- Read access to a data table, such as a Snowflake schema
- Assignment of a role, such as "Admin" in Zendesk
Having an account in an app is an entitlement too. In C1.ai, every managed application includes a built-in Access entitlement that references all accounts in the app, so account membership can be requested and reviewed like any other entitlement. Entitlements are the smallest unit of access an IGA program governs, and the unit auditors ask about.
Why entitlement management matters#
- Security. Most breaches that involve identity exploit access that was valid but excessive. Fewer standing entitlements means a smaller blast radius when a credential is stolen.
- Compliance. SOX, HIPAA, PCI DSS, and ISO 27001 all require you to show who has access to sensitive systems and that the access was approved and reviewed.
- Cost. Unused entitlements often map to paid SaaS licenses. Removing them recovers spend.
How entitlement management works#
A mature program follows the same lifecycle for every entitlement:
- Discover. Ingest application data via connector, file, or other data feed to identify every resource (roles, groups, and similar objects) and the entitlements on it.
- Describe. Give each entitlement an owner, a clear description (ideally synced from the source system, such as an Entra group description), and attributes like risk level and compliance framework.
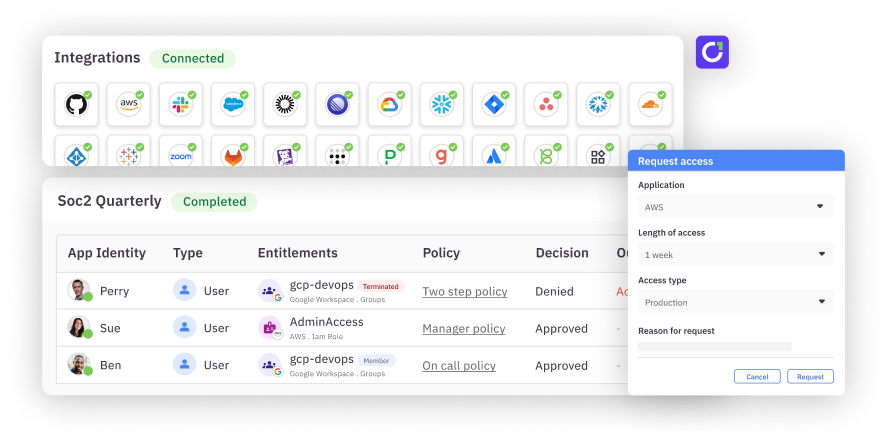
- Grant. Provision access through requests and approvals, birthright rules tied to HR attributes, or time-bound grants with an expiration date.
- Review. Run periodic and event-driven entitlement reviews, scoped by risk level or compliance framework, so owners confirm access is still needed.
- Revoke. Remove access when a review denies it, a grant expires, or a person changes roles or leaves.
Entitlements vs roles vs permissions#
These three terms get used interchangeably, but they sit at different layers:
| Term | What it is | Who usually defines it |
|---|---|---|
| Permission | A single action the app enforces on a resource, such as "edit opportunity" or "delete repository." | The application vendor |
| Entitlement | A grantable access right on a resource in one app, such as membership in a GitHub team or assignment of a Salesforce permission set. | The app admin, synced into the IGA platform |
| Role | An app role (such as "Admin" in Zendesk) is a resource you hold an entitlement to. A business role (such as "Sales Manager, EMEA") bundles entitlements across apps. | App admins for app roles; the IGA team and business owners for business roles |
In C1.ai, cross-app bundles of entitlements are managed as access profiles, which can grant access automatically or make entitlements requestable.
Example: entitlements in a SaaS app#
Take Salesforce. The permission "View All Data" lets a user read every record in the org. That permission lives inside a permission set called "Sales Ops Reporting," which is the entitlement an admin grants to a user. The IGA team then defines a business role, "Sales Operations Analyst," that bundles the Salesforce "Sales Ops Reporting" entitlement with a Tableau "Viewer" license and membership in the #sales-ops Slack channel.
When Priya joins as a Sales Operations Analyst, she receives the role and all three entitlements automatically. When she moves to Marketing six months later, entitlement management removes "Sales Ops Reporting" instead of letting it pile up on top of her new access. Otherwise, she keeps "View All Data" indefinitely.
Entitlement reviews#
An entitlement review is a structured check in which an application owner, manager, or entitlement owner confirms whether each identity should keep a specific entitlement. It is a focused form of the user access review: instead of asking "should this person have access to Salesforce?", it asks "should this person have the 'Sales Ops Reporting' permission set with View All Data?"
Good entitlement reviews share a few traits:
- Right reviewer. The entitlement owner or app owner reviews technical access; managers review whether the person still needs it for their job. In C1.ai, owners can be specific users or everyone who holds a given entitlement.
- Context on every line. Last login, last use of the entitlement, peer comparison, and risk level, so reviewers are not guessing.
- Risk-based cadence. Admin and production entitlements quarterly or more often; low-risk entitlements annually.
- Closed-loop remediation. A "revoke" decision triggers deprovisioning and leaves an evidence trail, not a ticket that sits for weeks.
For a step-by-step approach, see our guide to user access review best practices.
Regulations that require entitlement reviews#
| Regulation or framework | What it expects |
|---|---|
| SOX (ITGCs) | Access to financially significant systems is approved, appropriate, and periodically reviewed. |
| HIPAA Security Rule | Access to ePHI is authorized and limited under the information access management and access control standards (45 CFR 164.308(a)(4) and 164.312(a)). |
| PCI DSS v4.0 | Requirement 7.2.4 calls for reviewing user accounts and related access privileges at least every six months. |
| ISO/IEC 27001:2022 | Annex A controls 5.15 and 5.18 cover access control and the provisioning, review, and removal of access rights. |
| SOC 2 | Common Criteria CC6.1 through CC6.3 cover logical access, authorization, and removal. |
Common problems: sprawl, privilege creep#
Entitlement sprawl happens when the number of entitlements grows faster than anyone can track. A mid-sized company running 200 SaaS apps can easily hold tens of thousands of entitlements, many with cryptic names like "grp_fin_rw_02" and no listed owner. Reviewers cannot approve what they cannot understand, so they rubber-stamp. A quick first step is to filter for entitlements without grants: in C1.ai, the Without grants filter on an app's Entitlements tab surfaces unused entitlements to clean up.
Privilege creep is what sprawl does to an individual. Each promotion, project, or temporary fix adds entitlements, and nothing takes them away. Over time, long-tenured employees hold far more access than their current role needs, which violates least privilege and can create separation of duties conflicts, such as one person who can both create and approve a vendor payment.
Other common problems:
- Orphaned accounts that stay active after an employee or contractor leaves.
- Shadow entitlements granted directly in an app, outside the request process, so the IGA system never sees them.
- Manual, spreadsheet-based reviews that take weeks and produce weak audit evidence.
Entitlements for AI agents#
AI agents and other non-human identities (NHIs), such as service accounts, API keys, OAuth apps, and workload identities, hold entitlements too. They often outnumber human identities and are the least governed.
An AI agent that summarizes support tickets might hold a Zendesk API token with read access to every ticket, a Slack bot scope to post in channels, and a Google Drive scope to read shared files. Each of those is an entitlement. If nobody owns them, the agent's access can creep just like a person's, and with less visibility.
Entitlement management for agents and NHIs should follow the same model as for people:
- Inventory every non-human identity and the entitlements, tokens, and scopes it holds.
- Assign a human owner who is accountable for each agent and reviews its access.
- Scope to the task. Grant only the entitlements the agent needs, ideally just-in-time and time-bound.
- Include agents in entitlement reviews, with usage data that shows whether each scope is still exercised.
- Revoke automatically when the owner leaves, the project ends, or the token goes unused.
Governing humans and agents in one IGA model means one inventory, one review process, and one audit trail, instead of a separate blind spot for every new agent. In C1.ai, AI agents are governed by the same access profiles, policy, approval, and audit used for people, and the Identities and NHI dashboard brings service accounts, secrets, agents, and other machine identities into one view with ownership status.
Want to see it in action? Watch the platform demo.
FAQ#
What is entitlement management in IGA?#
Entitlement management is the part of identity governance and administration that controls the specific access rights identities hold inside applications. It covers discovering, describing, granting, reviewing, and revoking entitlements so access stays least-privileged and auditable.
What are entitlements in cybersecurity?#
Entitlements are individual access rights granted to an identity in a system, such as a group membership, an app role, a permission set, or an API scope. They define what an identity can do after it authenticates.
What is the difference between an entitlement and a permission?#
A permission is a single action the application enforces, like "delete record." An entitlement is the access right an identity is granted on a resource, like membership in an Okta group or assignment of a Salesforce permission set, and it often carries several permissions. IGA programs govern at the entitlement level.
What is an entitlement review?#
An entitlement review is a periodic or event-driven check in which owners confirm whether each identity should keep a specific entitlement. Revoked entitlements should be removed automatically, with evidence recorded for auditors.
How often should entitlement reviews happen?#
Base the cadence on risk. Privileged and financially significant entitlements are commonly reviewed quarterly, PCI DSS requires at least every six months for in-scope systems, and low-risk entitlements are often reviewed annually.
Do AI agents need entitlement management?#
Yes. AI agents and other non-human identities hold tokens, scopes, and roles that grant real access to data. They need an owner, least-privilege scoping, inclusion in entitlement reviews, and automatic revocation.
How does C1.ai handle entitlement management?#
C1.ai (formerly ConductorOne) is an IGA platform that creates resources and entitlements automatically when application data is ingested via connector, file, or other data feed. Teams assign entitlement owners, tag entitlements by risk level and compliance framework, set expirations on grants, require owner approval on access requests, and scope access reviews by those attributes. AI agents are governed through the same access profiles, policy, and approvals.