What is IGA?#
Identity governance and administration (IGA) is the set of policies, processes, and tools an organization uses to decide who can access which systems and data, keep that access correct over time, and prove it to auditors. IGA covers: joiner, mover, and leaver changes, access requests, access reviews, and policy checks such as separation of duties.
What does IGA stand for? IGA stands for identity governance and administration. This is also often called identity governance or identity and access governance.
Each part of the name solves for different problems. Governance sets the rules and checks that they hold: who should have access, who approves it, and whether it is still right. Administration carries the rules out: creating accounts, assigning entitlements, and removing them.
Every employee, contractor, service account, and AI agent holds access that someone has to approve and later take away. Without IGA, that work lives in tickets and spreadsheets, and access drifts away from what people actually need. IGA keeps a record of who has access, why they have it, who approved it, and when someone last checked.
Why IGA matters. A leaver whose account stays active, a contractor with admin rights nobody remembers granting, and an approver who can also release payments are all access problems. Every sign-in looks valid, so it is never flagged as a problem. IGA finds them by comparing what people hold against what their role, approvals, and HR status say they should hold. It also gives security leaders one answer to the question auditors ask every year: who has access to the systems that matter, and who said they should?
In practice, IT handles fewer access tickets, and GRC has review evidence ready before the auditor asks for it.
To plan a program, see how to build an identity governance framework.
IGA vs IAM vs PAM#
IAM, PAM, and IGA are three layers of the same identity program. IAM gets a user in the door, PAM protects the highest-risk accounts, and IGA decides whether the access should exist at all.
| IAM | PAM | IGA | |
|---|---|---|---|
| Core question | Is this user who they claim to be? | Can this privileged account take this action now? | Should this identity have this access, and can we prove it? |
| Main focus | Authentication, SSO, MFA | Admin, root, and service credentials | Access lifecycle, reviews, policy, audit evidence |
| When it acts | At sign-in | During a privileged session | Across the life of the access |
| Typical owner | IT or identity team | Security or infrastructure | Security, GRC, IT, and audit together |
| Failure it prevents | Account takeover | Misuse of powerful accounts | Excess, stale, and unapproved access |
Some frameworks treat IAM as the umbrella category, with access management, PAM, and IGA inside it. The three overlap, and none of them replaces the others. For a deeper comparison, read IGA vs IAM, or see IGA vs PAM.
Core capabilities of IGA#
Six capabilities make up an IGA program. Each one links to its own glossary entry.
| Capability | What it does | Question it answers |
|---|---|---|
| User access reviews | Managers and app owners certify that each person's access is still needed | Does everyone still need what they have? |
| Lifecycle and provisioning | Creates, changes, and removes access as people join, move, and leave, driven by HR data | Does access follow the person's role from day one to last day? |
| Access requests | Gives people one place to ask for access, with approval routing and policy checks | Who asked, who approved, and why? |
| Separation of duties | Blocks or flags combinations of access that let one person complete a risky process alone | Can any one person both start and approve a sensitive action? |
| Entitlement management | Catalogs the permissions inside every application and ties them to roles and owners | What can each account do in each system? |
| Reporting and audit evidence | Produces timestamped records of requests, approvals, reviews, and removals | Can we show an auditor what happened? |
User access reviews. Periodic reviews catch access that outlived its purpose. Reviewers see who has access to what, certify what is still needed, and revoke the rest. C1.ai flags unusual access so reviewers spend their time there instead of approving thousands of lines they cannot judge. See user access reviews.
Lifecycle and provisioning. HR events drive access. A new hire gets the baseline for their role on day one, a transfer swaps old access for new, and a departure closes accounts the same day. Zscaler's move from weeks to 10 minutes for new hires came from this step, described below. See user provisioning.
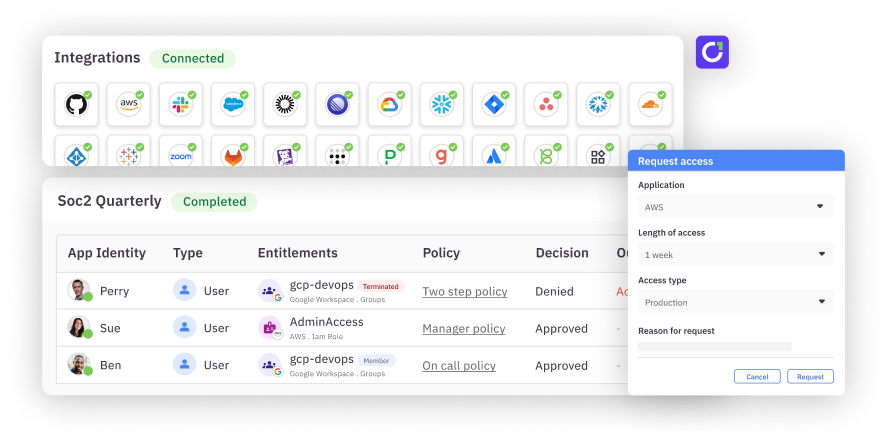
Access requests. Self-service replaces email and tickets. Requests route to the right approver, check policy, and provision automatically once approved, so the person gets access quickly and the approval is on record. See access requests.
Separation of duties. One person should not be able to create a vendor and approve its payment. Separation of duties rules encode pairs like that, and the platform checks them when someone requests access and again during reviews, so conflicts are stopped before they exist.
Entitlement management. Applications describe permissions in their own vocabulary. Entitlement management translates them into terms reviewers understand, links each one to an owner and a role, and shows who holds it.
Reporting and audit evidence. Dashboards show review completion, open exceptions, and aging requests. Exportable records show auditors what happened without a scramble to assemble screenshots.
Least privilege runs through all six. Read what is least privilege for the principle behind the controls, and what is joiner-mover-leaver for the lifecycle events that trigger them.
C1.ai is an example of modern IGA. It connects to applications through API-based connectors built on the open-source Baton framework, lets employees request access in Slack, supports just-in-time and time-bound access, and uses AI to help reviewers focus on the access that looks unusual. See the C1.ai IGA product page, or compare vendors in the IGA solutions guide.
How IGA works, step by step#
Most IGA programs follow the same loop, whatever platform runs it.
- Connect your sources. The platform reads from the HR system, the identity provider, and each application. HR data tells it who works there and in what role. Applications tell it what access exists.
- Build an inventory. It maps every identity to its accounts and entitlements across systems, and assigns an owner to each. Orphaned accounts with no owner show up at this step.
- Set policy. Security and GRC teams define what access each role gets by default, which access needs approval, and which combinations are not allowed. Role design and separation of duties rules live here.
- Automate the lifecycle and requests. When HR records a new hire, transfer, or departure, the platform grants, changes, or removes access to match. Requests outside the default role go through approval, with policy checks at each step.
- Review access on a schedule and on demand. Reviewers certify or revoke access in user access reviews. Revocations are carried out automatically so a "revoke" decision does not sit in a ticket queue.
- Report and improve. Every action is logged. Teams use the record to answer auditors, spot patterns such as accounts that never get used, and tighten policy.
Four groups share the work of IGA. HR owns the source data, IT runs provisioning and integrations, security and GRC own policy and review design, and managers and app owners make the review decisions. Managers see plain-language review items, so they know exactly what they’re approving and reviewing.
IGA for AI agents and non-human identities#
Non-human identities (NHIs) include service accounts, API keys, bots, and AI agents. They hold access the same way a person does, but they rarely have a manager, an HR record, or a last day, so they escape the controls built for employees.
An AI agent can act on its own, call other systems, and hold broad permissions that nobody reviews after the first setup. A single compromised agent credential can expose every system the agent can reach, which is why its access should be as narrow and scoped specifically to the task at hand. Governing agents is the same job IGA already does for people, applied to a new kind of identity:
- Assign an owner. Every agent and service account needs a named human or team accountable for it. When that owner leaves, the platform flags the orphaned identity.
- Scope access to the task. Grant only the permissions the agent needs, and prefer time-bound access over standing access.
- Review it like any other access. Include NHIs in access reviews, with an owner who can certify or revoke.
- Retire it on schedule. When a project ends or an agent is replaced, remove its credentials and entitlements.
Take a support-automation agent that reads customer records and writes to a ticketing system. It should have an owner on the support team, read access to the records it needs and nothing else, and a review date. If the agent is retired, its credentials should go with it.
Ask any platform whether it governs humans and agents from one inventory with one set of reviews, or whether agents need a separate tool. Read more in what is AI agent identity.
Legacy vs modern IGA#
Older IGA platforms were built for on-premises systems and long implementation projects. Modern platforms are built for cloud and SaaS estates that change every week. The differences show up in how each is deployed, connected, and run.
| Legacy IGA | Modern IGA | |
|---|---|---|
| Deployment | Multi-phase projects, often with services partners | Cloud-delivered, configured by the identity team |
| Integrations | Custom connectors and scripts per application | API-based connectors, often prebuilt |
| Access requests | Ticket queues and forms | Requests in chat tools with policy-based routing |
| Reviews | Large periodic campaigns, often spreadsheets | Focused campaigns with data that is current at review time |
| Agents and NHIs | Added later, if at all | Governed in the same model as people |
The shift is also about who does the work. In a legacy deployment, a small group of specialists can end up maintaining connectors and workflows, so every new application becomes a project. Modern platforms move routine configuration to the identity team, which shortens the path from signing a new SaaS contract to governing it.
Judge any platform on outcomes you can check: time to onboard a new application, time to complete a review campaign, and hours spent preparing for an audit. If you are moving from SailPoint or Saviynt, the modern IGA vs legacy IGA page covers the differences, and there are side-by-side comparisons for SailPoint and Saviynt.
Common signs it is time to modernize: access reviews take weeks and reviewers approve in bulk, new hires wait days for access, no one can list every AI agent and service account, and each audit starts with a hunt for evidence.
Large enterprise example: Zscaler. Zscaler is a cloud security company with 5,001 to 10,000 employees. Provisioning for new hires took weeks, and access reviews ran on spreadsheets and screenshots. Zscaler connected about 250 applications to C1.ai, moved to role-based provisioning, and let employees request access in Slack. New-hire provisioning dropped from weeks to 10 minutes, help desk access tickets fell 60%, and user access review volume fell 35% (Zscaler customer story).
Regulations IGA supports#
Auditors rarely ask for "IGA" by name. They ask for evidence that access is limited, approved, and reviewed. IGA produces that evidence as a byproduct of running the program.
| Regulation | Who it applies to | Access expectation | What IGA provides |
|---|---|---|---|
| SOX (Section 404) | US public companies | IT general controls over systems that feed financial reporting, including access and periodic access review | Review records, SoD checks, and approval trails for in-scope applications |
| HIPAA Security Rule | Healthcare providers, plans, and their business associates | Workforce access limited to what the role needs, with access control and audit controls | Role-based access, timely removal for leavers, and logs of who accessed what |
| GLBA Safeguards Rule | Financial institutions in scope of the FTC rule | Access controls that limit customer information to authorized users | Access limited by role, reviews, and records that support the required security program |
| ISO 27001 | Any organization certified to the standard | Annex A controls for access control, identity management, access rights, and privileged access | Documented joiner, mover, and leaver processes and periodic access rights reviews |
Two practical points apply to all four regulations. First, evidence must be current: a review from last year does not show today's access. Second, reviews must lead to action. Auditors look for proof that revocations were carried out, not only that someone clicked approve, so removal should be automated and logged.
Regulated industry example: Qualtrics. Qualtrics is a software company with 5,001 to 10,000 employees that operates under FedRAMP High, which demands granular access controls and strict auditing. Its access reviews were manual and onboarding was disconnected across systems. After adopting C1.ai, onboarding on integrated systems dropped from one to two weeks to under an hour, and access request fulfillment went from four full-time employees to one. Timestamped data on users and entitlements also simplified audits (Qualtrics customer story).
For the evidence auditors expect, see user access reviews, what is HIPAA, and what is GLBA.
IGA FAQ#
What does IGA stand for? IGA stands for identity governance and administration.
What is IGA in simple terms? IGA is how an organization decides who gets access to what, keeps that access correct as people change roles, and proves it to auditors. It covers requests, approvals, reviews, and removal.
What is the difference between identity governance and identity administration? Governance sets and checks the rules for access: who should have it, who approves it, and whether it is still right. Administration carries the rules out by creating accounts, assigning entitlements, and removing them. IGA combines both.
Is IGA the same as IAM? No. IAM covers sign-in and authentication. IGA governs the access itself: whether it should exist, who approved it, and whether it is still needed. You need both.
How is IGA different from PAM? PAM secures privileged accounts and sessions. IGA governs every kind of access, privileged or not, across its full life. They work together.
Who needs IGA? Any organization where access has outgrown manual tracking, and especially those under SOX, HIPAA, GLBA, or ISO 27001 requirements.
Can IGA govern AI agents and service accounts? Yes, if the platform treats them as identities with owners, scoped access, and regular reviews. Platforms that only model employees leave agents ungoverned.
How long does an IGA rollout take? It depends on the number of applications and the quality of HR data. Zscaler's rollout across about 250 applications ran 12 months. Start with the applications in audit scope and expand.
What should I look for in an IGA platform? Check how many of your applications it connects to without custom code, whether it governs AI agents and service accounts alongside people, how quickly reviewers can finish a campaign, and what audit evidence it produces. Ask vendors for these as measured outcomes, and compare them in the IGA solutions guide.
How do I move from SailPoint or Saviynt? Start by listing the applications and review campaigns that matter most for audit, then migrate in waves. The modern IGA page covers how modern platforms differ, and there are comparisons for SailPoint and Saviynt.
What is C1.ai? C1.ai, formerly ConductorOne, is a modern IGA platform that governs access for employees, contractors, and AI agents. See the IGA product page.