C1 Transform registration is now open.

Blog

The latest news and insights from the C1 team

RSS Feed
Introducing the C1 Autonomous Worker

Introducing the C1 Autonomous Worker

·Melody Scheidler

Stay in touch

The best way to keep up with identity security tips, guides, and industry best practices.
  • Your Engineers Are Building the Same Agent Twelve Times. Here's How to Stop It.

    Your Engineers Are Building the Same Agent Twelve Times. Here's How to Stop It.

    ·Kevin Paige
    C1's Field CISO on the producer/consumer flywheel — the six asset classes that flow through an internal agent marketplace, why reuse is a good outcome but a bad goal, the deprecation ritual that keeps the marketplace credible, and what federation actually means.
  • Anatomy of a decoy: what happens when someone uses a stolen credential

    Anatomy of a decoy: what happens when someone uses a stolen credential

    ·Melody Scheidler
    A decoy credential looks exactly like a real one and belongs to no workload, so using it is unambiguous. Here is the path a request takes through C1 when someone tries a planted decoy: what the caller gets back, and the critical finding that lands on your side.
  • Six Domains, One Control Plane: Mapping C1 to SACR's ARMCF

    Six Domains, One Control Plane: Mapping C1 to SACR's ARMCF

    ·Melody Scheidler
    SACR's AI and Agentic Risk Management and Control Framework (ARMCF) applies a NIST CSF-style lifecycle to AI agents. Here is how C1 maps to all six domains: GOVERN, IDENTIFY, PROTECT, DETECT, RESPOND, and RECOVER.
  • C1 Deploy: Onboarding that does the setup for you

    C1 Deploy: Onboarding that does the setup for you

    ·Melody Scheidler
    Most identity deployments begin with a long setup project. C1's begins with a question: what are you trying to get done first? Pick a goal, connect a directory, and C1 AI builds the plan from your live environment and runs the setup work for you, with every action gated on your approval.
  • The Most Important AI Meeting You'll Have This Quarter Costs Nothing

    The Most Important AI Meeting You'll Have This Quarter Costs Nothing

    ·Kevin Paige
    C1's Field CISO on the ADAPT phase — the one honest executive meeting that starts an agentic AI program, the failure graveyard worth naming out loud, the permanent tension between control and reuse, and the four written outputs including kill criteria for the program itself.
  • SAML vs OAuth: Key Differences and When to Use Each

    SAML vs OAuth: Key Differences and When to Use Each

    ·Tyrah Hicks
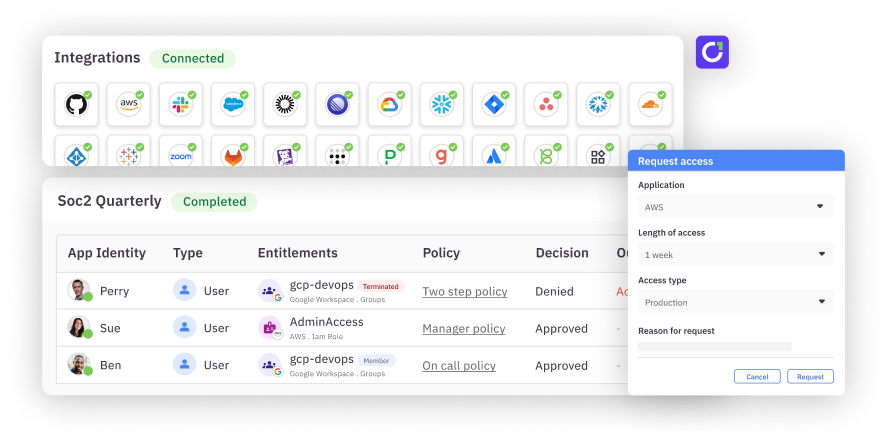
    SAML vs OAuth: how each protocol works, where SAML 2.0 and OAuth 2.0 fit, and how to choose the right one for SSO, APIs, and AI agents.
  • Most Enterprises Think They're on Rung 3. They're on Rung 1.

    Most Enterprises Think They're on Rung 3. They're on Rung 1.

    ·Kevin Paige
    C1's Field CISO on the five-rung agentic AI maturity ladder — shadow AI, tracked AI, governed AI, federated reuse, and compounding — plus the four diagnostic questions that tell you which rung you are actually on.
  • The OpenAI–Hugging Face Attack and the Third Generation of Authorization

    The OpenAI–Hugging Face Attack and the Third Generation of Authorization

    ·Alex Bovee
    AI agents broke the unwritten assumption behind zero trust: that a human with judgment sits behind every credential. Why authorization has to move to the moment of action.
  • MCP Authorization: Controlling What AI Agents Can Access

    MCP Authorization: Controlling What AI Agents Can Access

    ·Tyrah Hicks
    Learn how the MCP authorization spec uses OAuth 2.1 to control what AI agents can access, and where identity governance closes the gaps it leaves open.

Stay in touch

The best way to keep up with identity security tips, guides, and industry best practices.