C1 Transform registration is now open.

Blog

Insights on identity security, access governance, and modern IGA.
  • Agent Authorization: Gateway or Token? The Answer Is Both

    Agent Authorization: Gateway or Token? The Answer Is Both

    ·Jess Starr
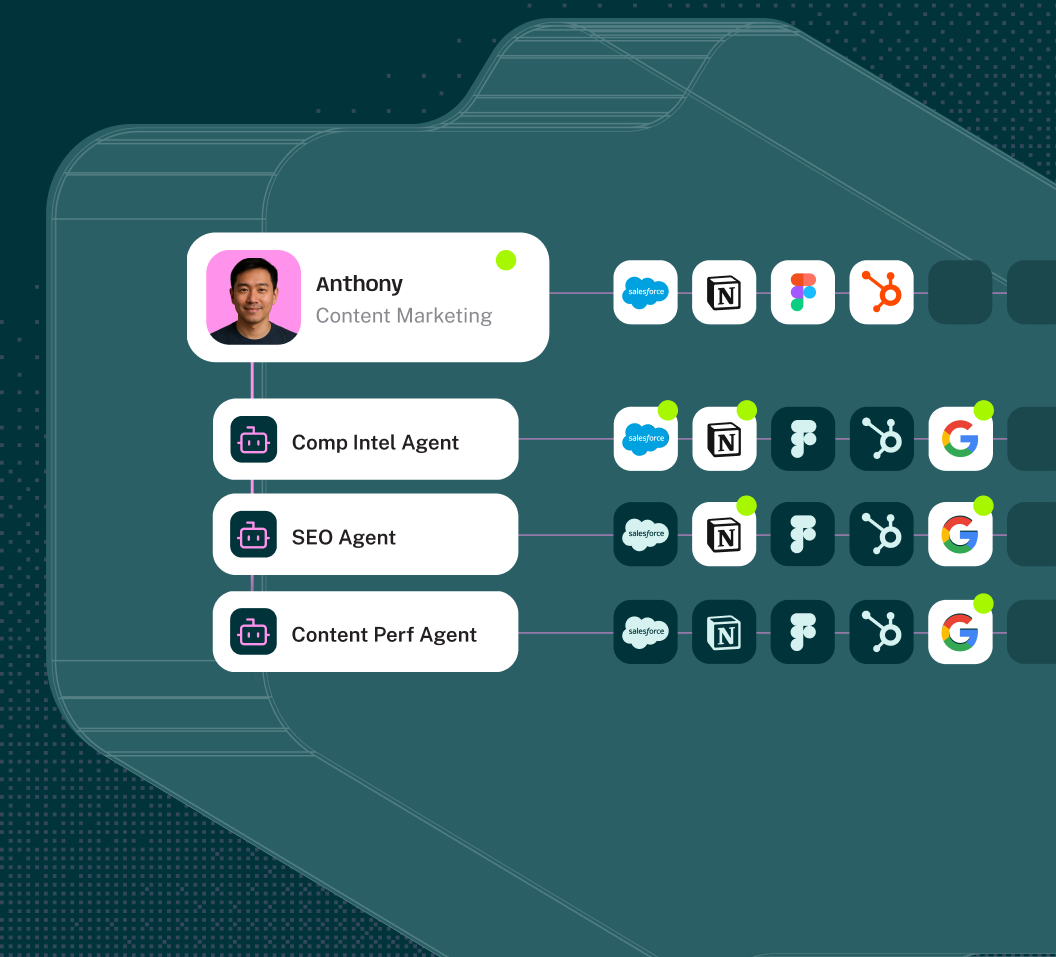
    Gateway proxy or standards-based token exchange? The two credible models for authorizing AI agents at runtime have complementary strengths, and no enterprise environment is uniform enough for one to cover everything. Why the right question is whether your platform supports both.
  • Seven Ways Enterprise AI Programs Die

    Seven Ways Enterprise AI Programs Die

    ·Kevin Paige
    C1's Field CISO on the seven failure patterns that kill enterprise AI programs — shadow tool sprawl, SSO mistaken for authorization, shared service accounts, policy nobody reads, and the review board reborn as an AI Council — and how to convert a gating function into an enabling one.
  • Launch Week Roundup: The Agentic Control Plane

    Launch Week Roundup: The Agentic Control Plane

    ·Melody Scheidler
    A recap of C1 Launch Week: shadow AI discovery, Agentic Vault, agent runtime governance, and agentic security and intelligence. Four launches, one control plane for governing every AI agent, secret, and non-human identity.
  • Introducing agentic security and intelligence: close identity risk with C1

    Introducing agentic security and intelligence: close identity risk with C1

    ·Maarten Buis
    C1's agentic security and intelligence detects identity risk across people, service accounts, workloads, and AI agents, then routes every finding through governed remediation or the tools your team already uses.
  • Introducing agent runtime governance: intent-based access control for AI agents

    Introducing agent runtime governance: intent-based access control for AI agents

    ·Maarten Buis
    C1's agent runtime governance routes every AI agent tool call through one governed gateway, scopes each agent to the tools its job needs, and scores every call for risk before it runs so you can block, hold, or redact it.
  • Introducing Agentic Vault: govern every secret like an identity

    Introducing Agentic Vault: govern every secret like an identity

    ·Melody Scheidler
    C1's Agentic Vault secures the credentials your people, agents, and service accounts depend on, governing every secret through the same request, approval, and audit path as any other access, with post-quantum protection from day one.
  • Introducing shadow AI discovery: find the AI you didn't sanction

    Introducing shadow AI discovery: find the AI you didn't sanction

    ·Melody Scheidler
    C1's shadow AI discovery helps security teams find unsanctioned AI tools, AI agents, MCP servers, and exposed credentials across cloud and endpoints, then assign ownership and govern them.
  • Why an MCP Gateway Is Not Governance

    Why an MCP Gateway Is Not Governance

    ·Tyrah Hicks
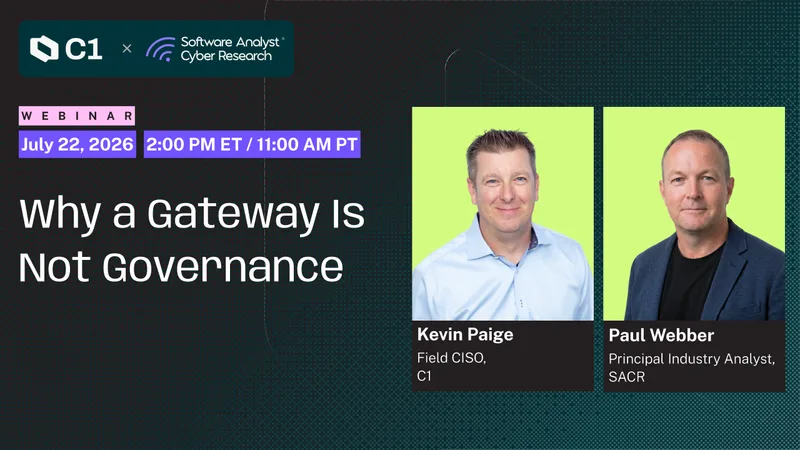
    C1 Field CISO Kevin Paige and SACR analyst Paul Webber on why routing agent traffic through an MCP gateway isn't the same as governing what agents are entitled to do — and what good agent governance actually requires.
  • Why AI Transformation Stalls

    Why AI Transformation Stalls

    ·Jess Starr
    AI initiatives don't stall because the models fall short—they stall at the access layer. Here's why governed AI access lets productivity and security win together.