C1 Egress
Make secure access automatic with a proxy that holds the secrets so your builders don't have to.
Give agents network access without giving them secrets.
Safe by default.
Someone who has never heard of a hardcoded credential gets the safe outcome automatically. Less risk without asking every builder to become a security engineer.
Revocation is immediate.
Turning off a credential kills it on the next call, not on the next deploy, so an offboarding or incident response lands when you run it.
Nothing to steal.
Inspect an agent's environment and there is no credential in it for an attacker to find, because the workload never had one.
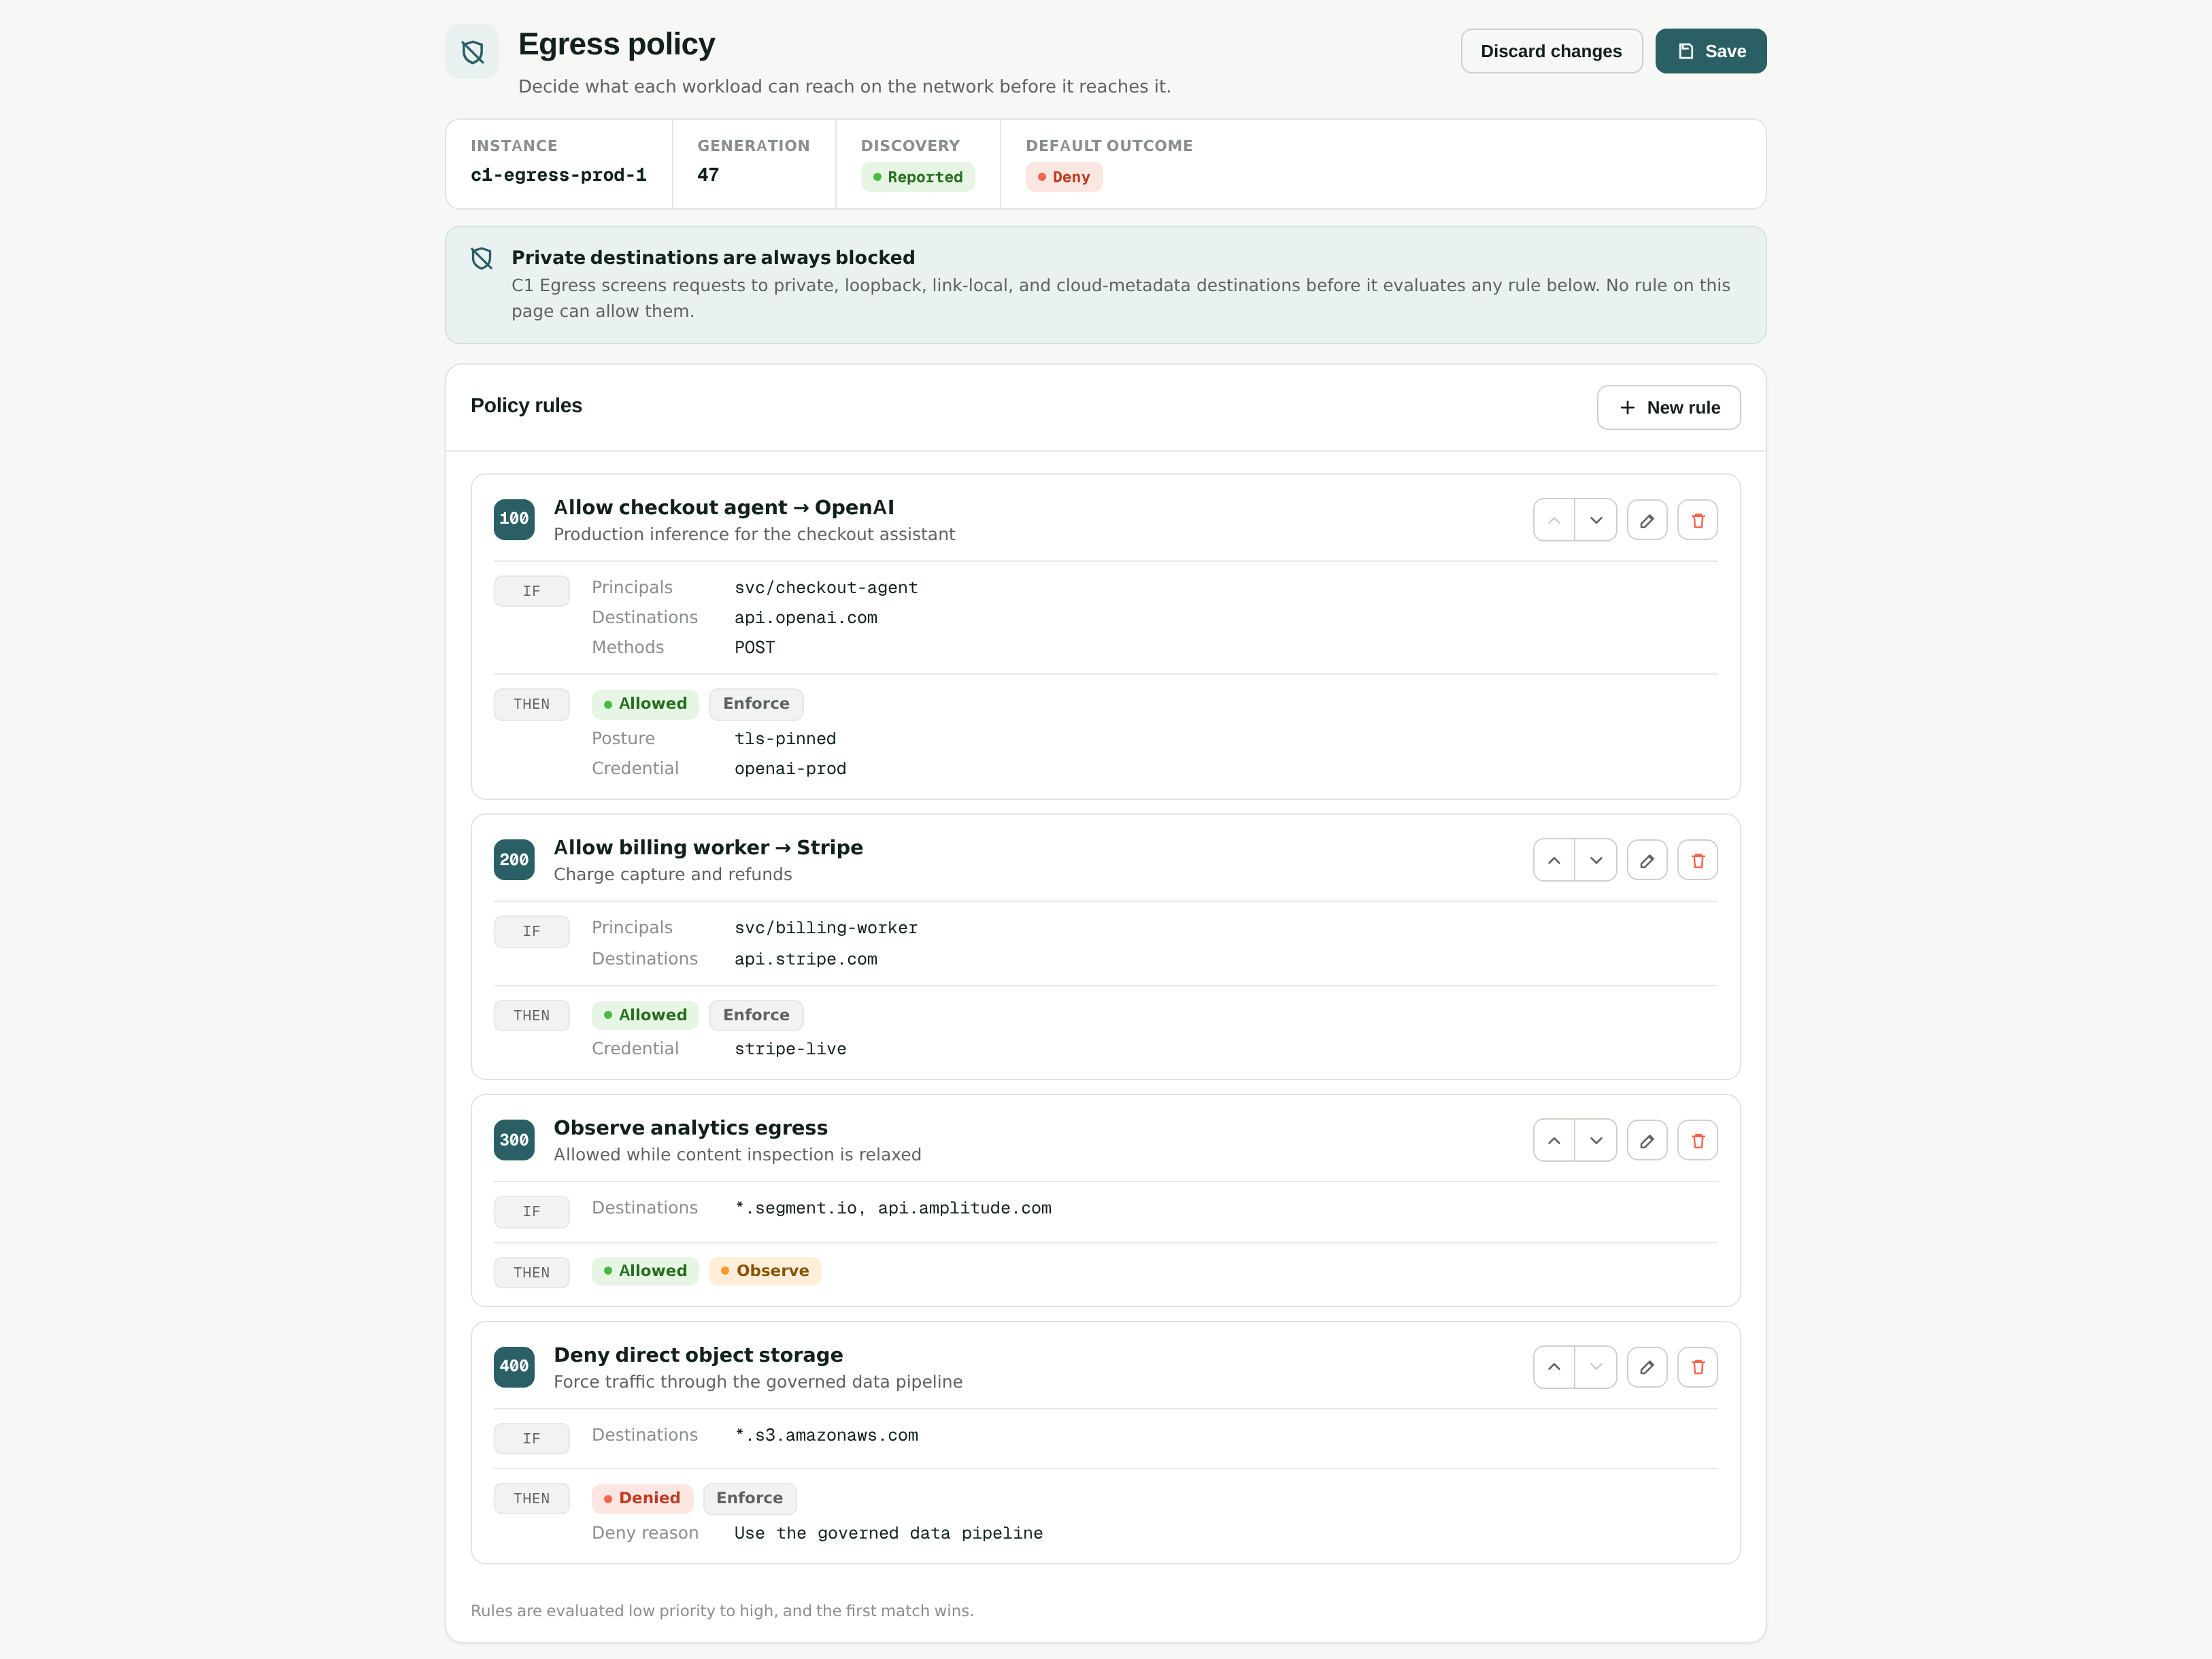
DEFAULT DENY EGRESS
Decide what an agent can reach before it runs.
How it works
An agent starts with every outbound destination blocked until allowed by policy.
CREDENTIAL INJECTION
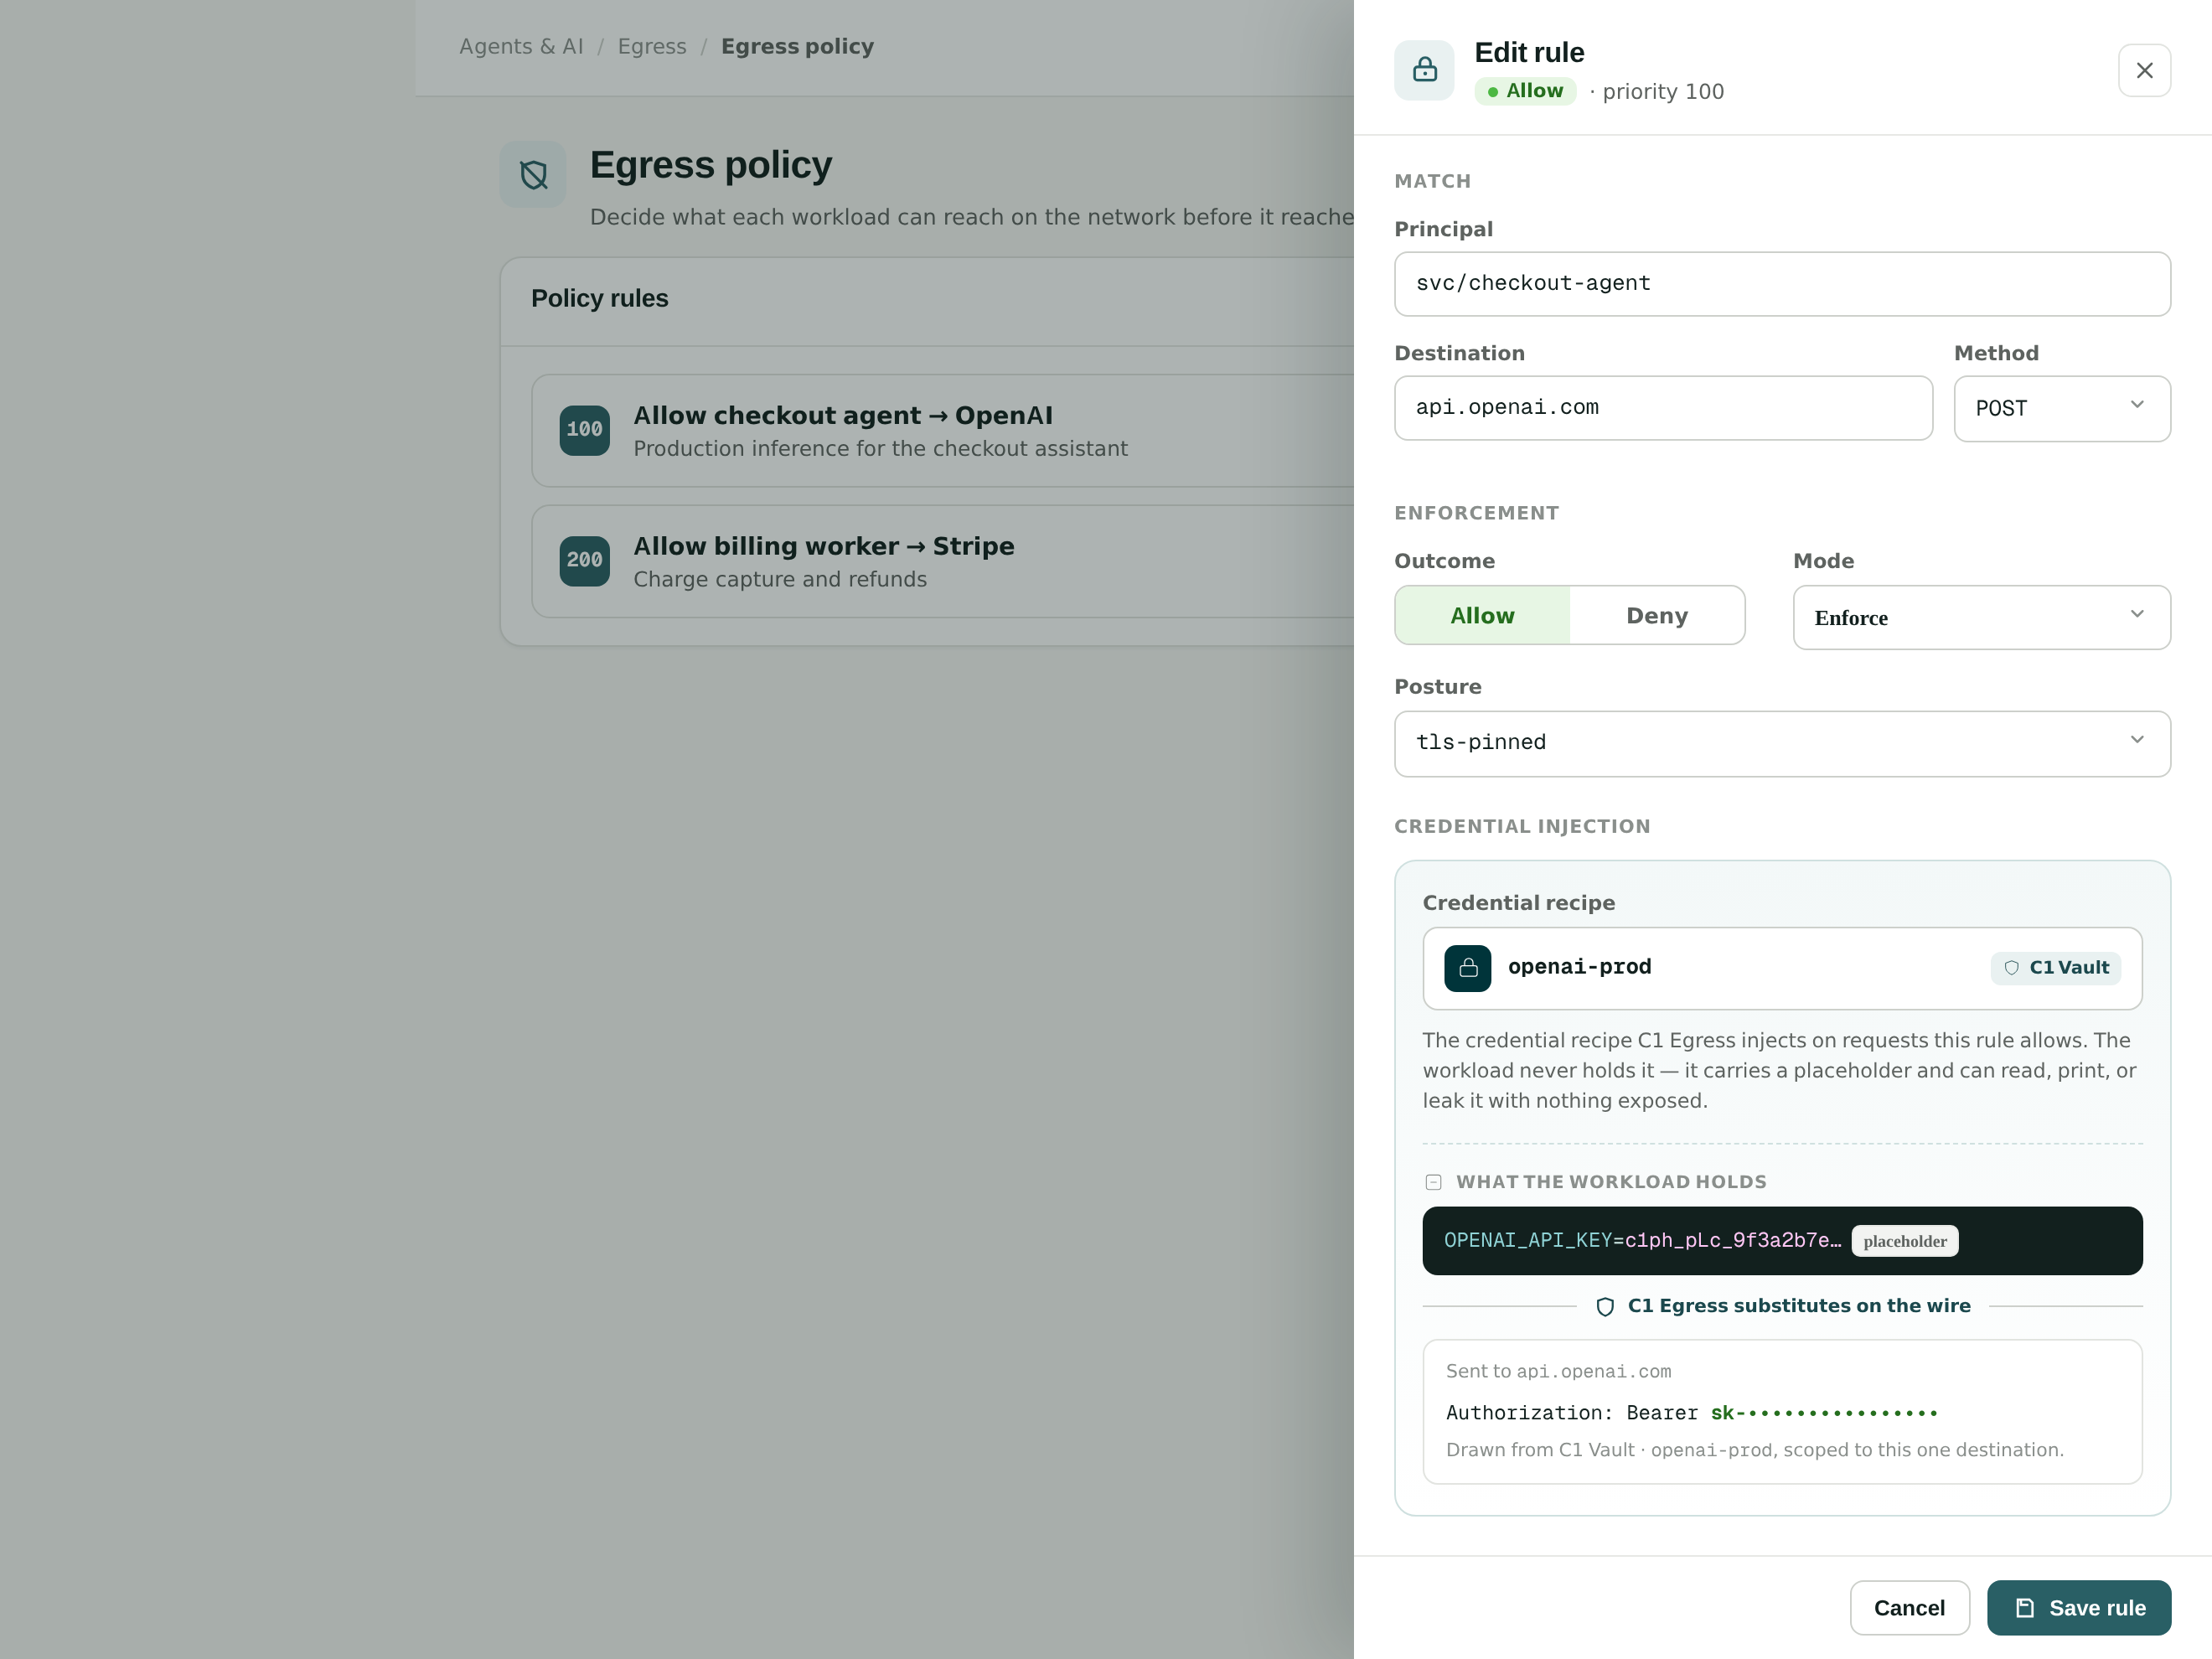
Keep the secret out of the LLM and off the endpoint.
How it works
The agent's environment holds a substitute credential. Read it, print it, or leak it and nothing is exposed.
EVIDENCE AND AUDIT
Keep a complete audit trail.
How it works
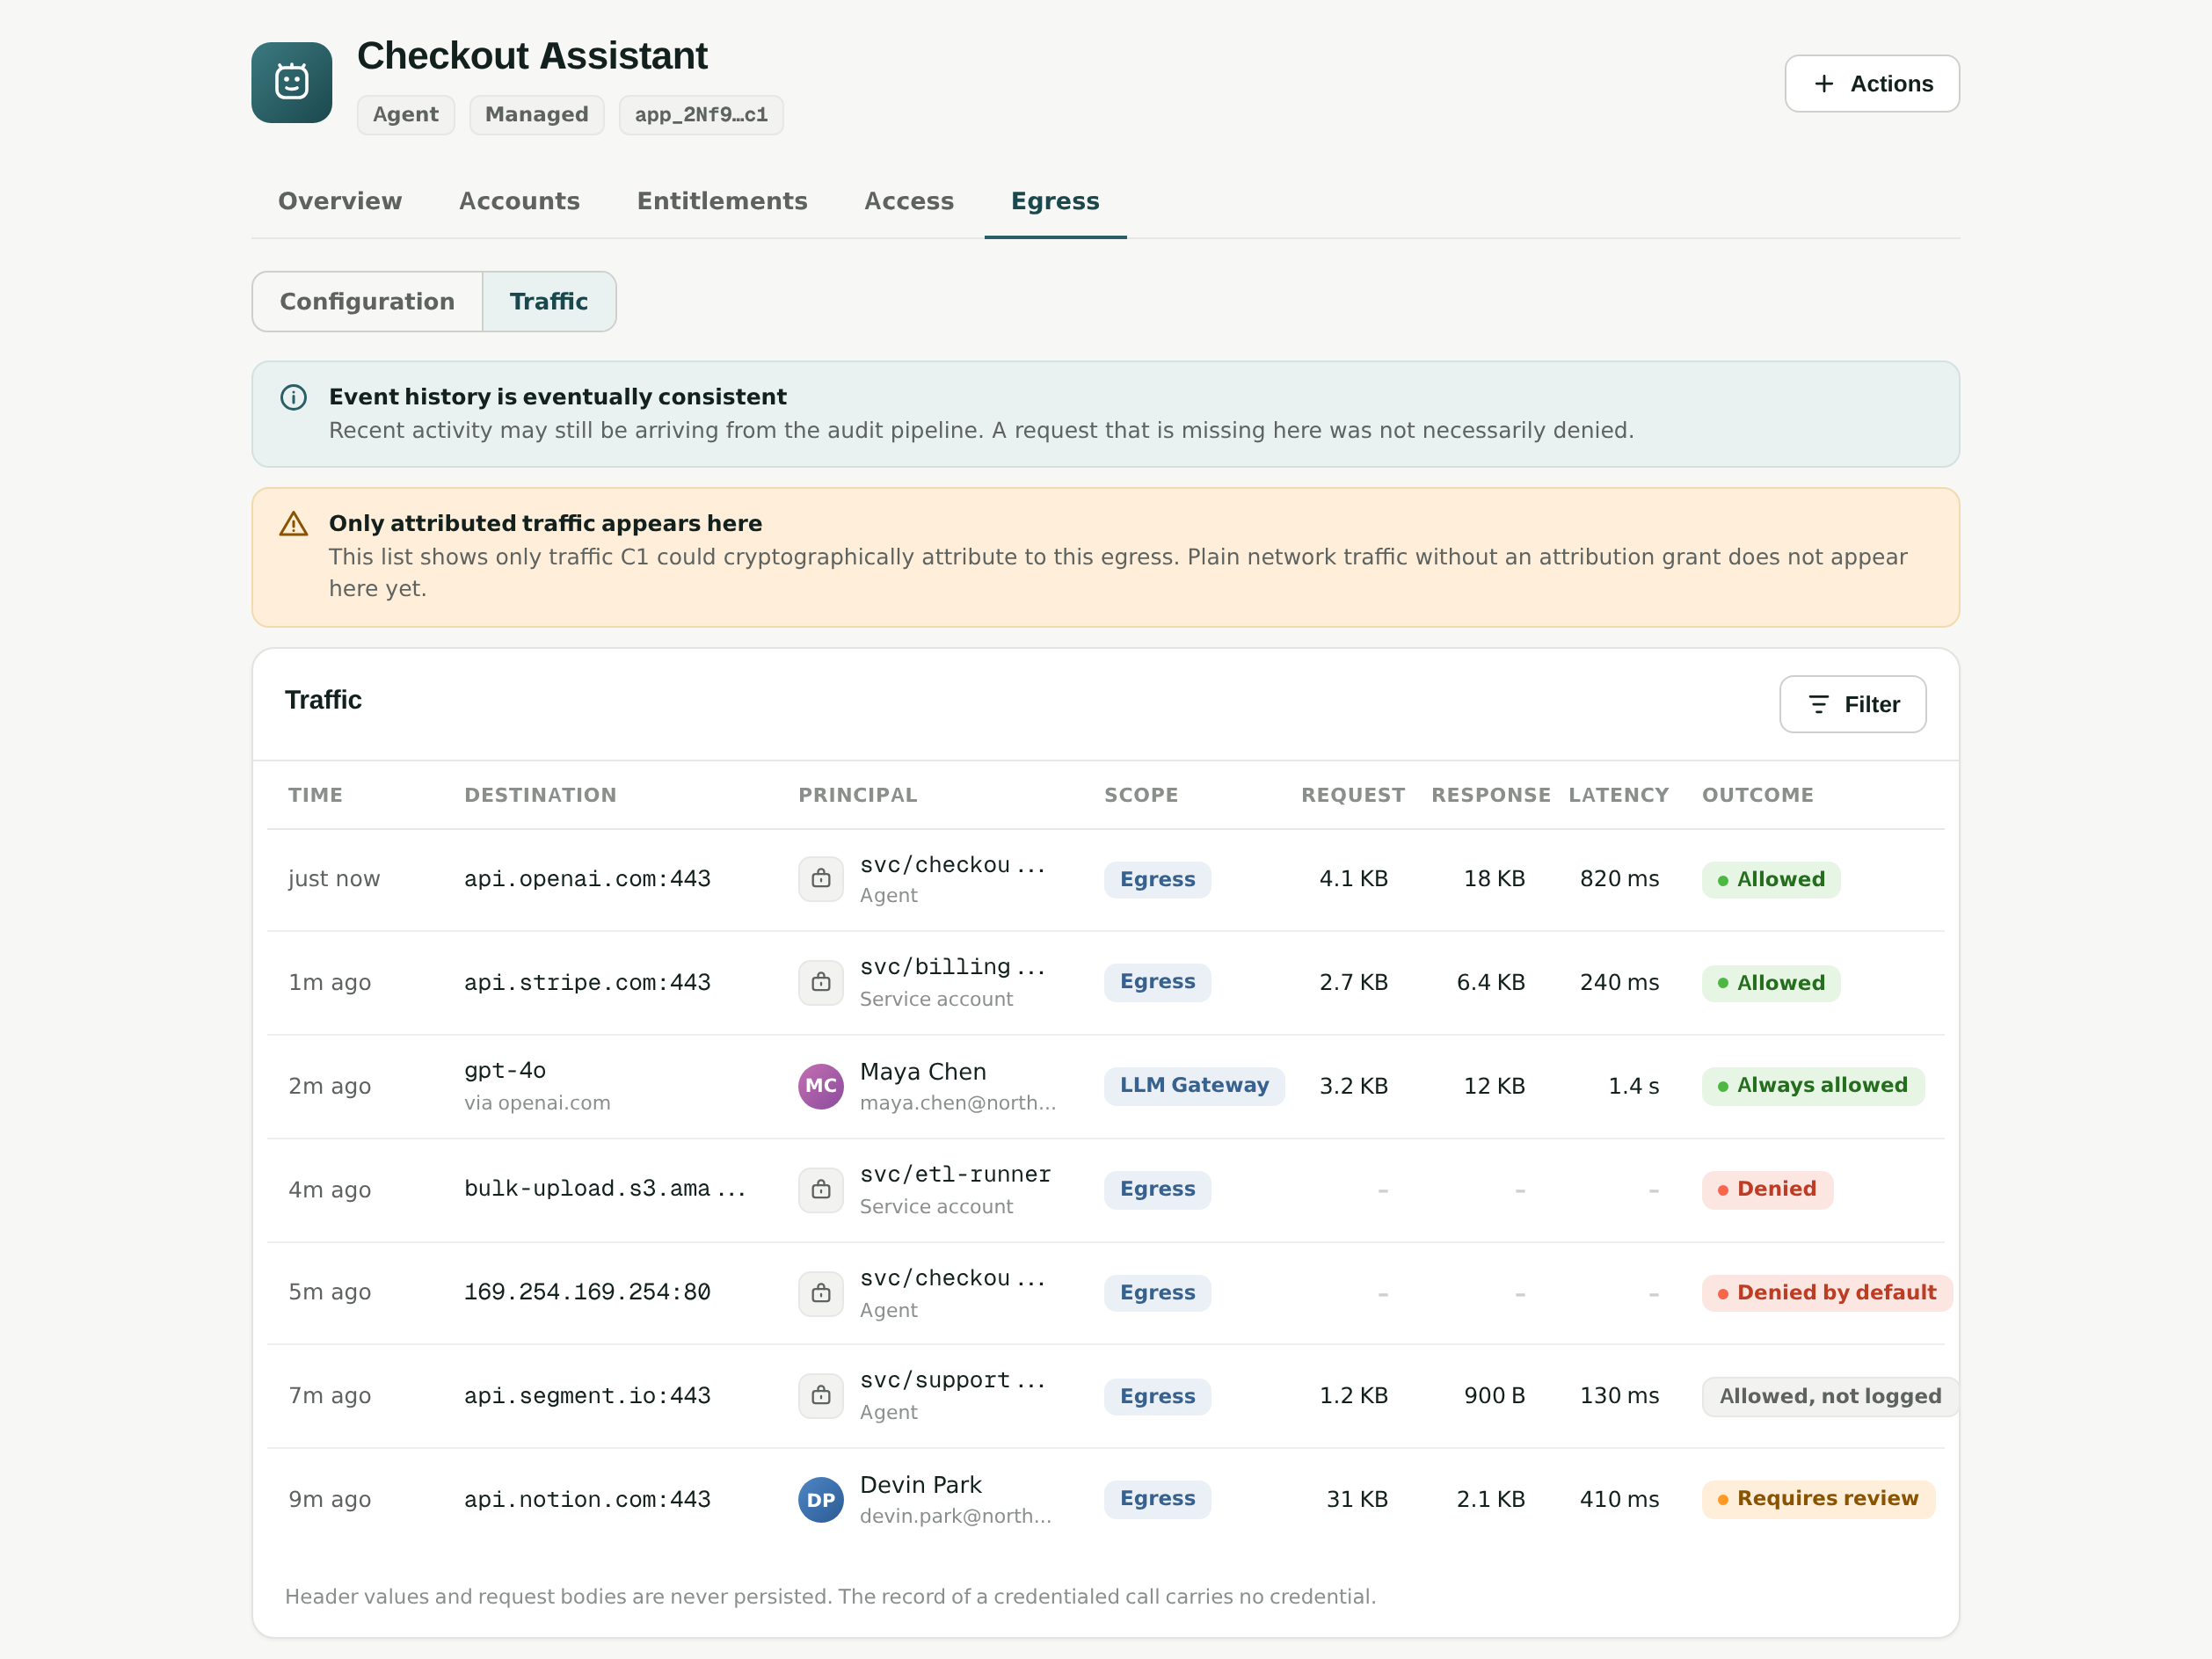
Source, destination, verdict, and counters for each outbound request, allowed and denied alike.