Request access where work happens
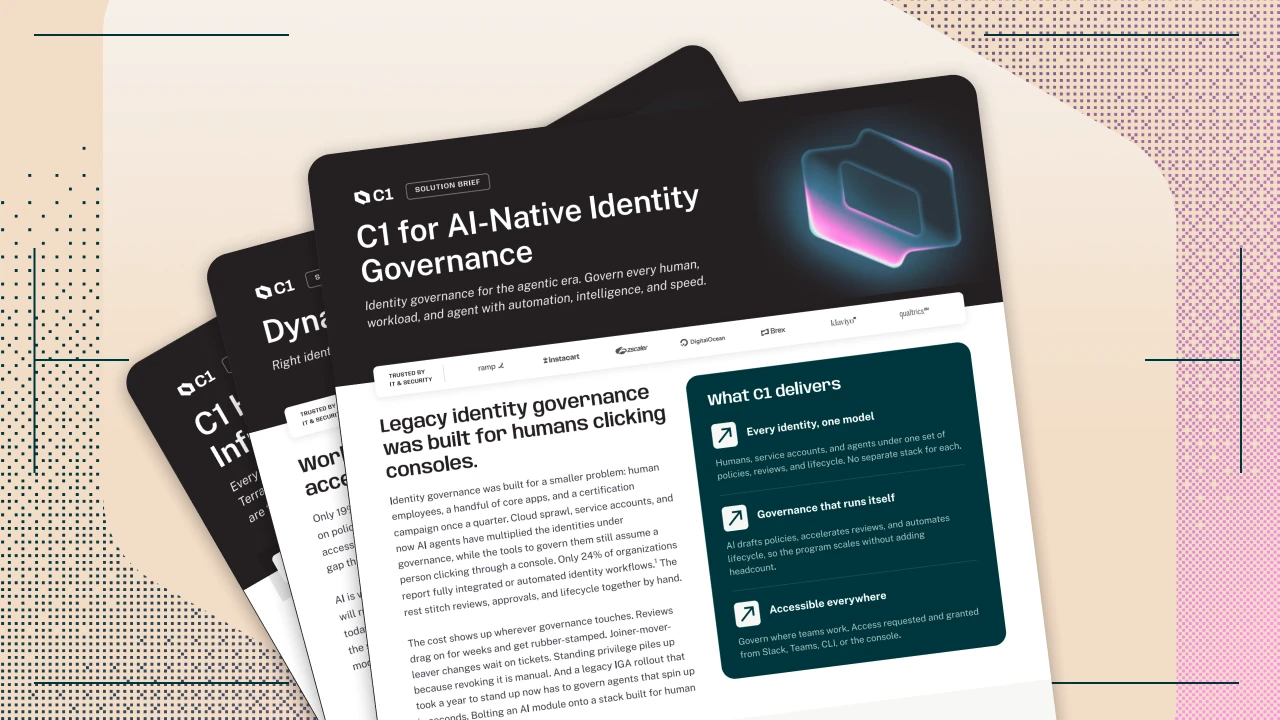
Let people request access in Slack, Microsoft Teams, web, CLI, or API, with the resource and duration included in the request.
Provision access on demand for humans and agents, for only as long as it's needed.
Let people request access in Slack, Microsoft Teams, web, CLI, or API, with the resource and duration included in the request.
Evaluate identity, role, resource, duration, risk, and emergency conditions before routing or auto-approving a request.
Limit each grant to the approved entitlement and duration, whether it is routine, on-call, or break-glass access.
Deprovision when time expires, the user stops using the access, or the justification no longer applies.