C1 MCP Gateway
Put identity-aware policy in front of every MCP tool call and resource access.
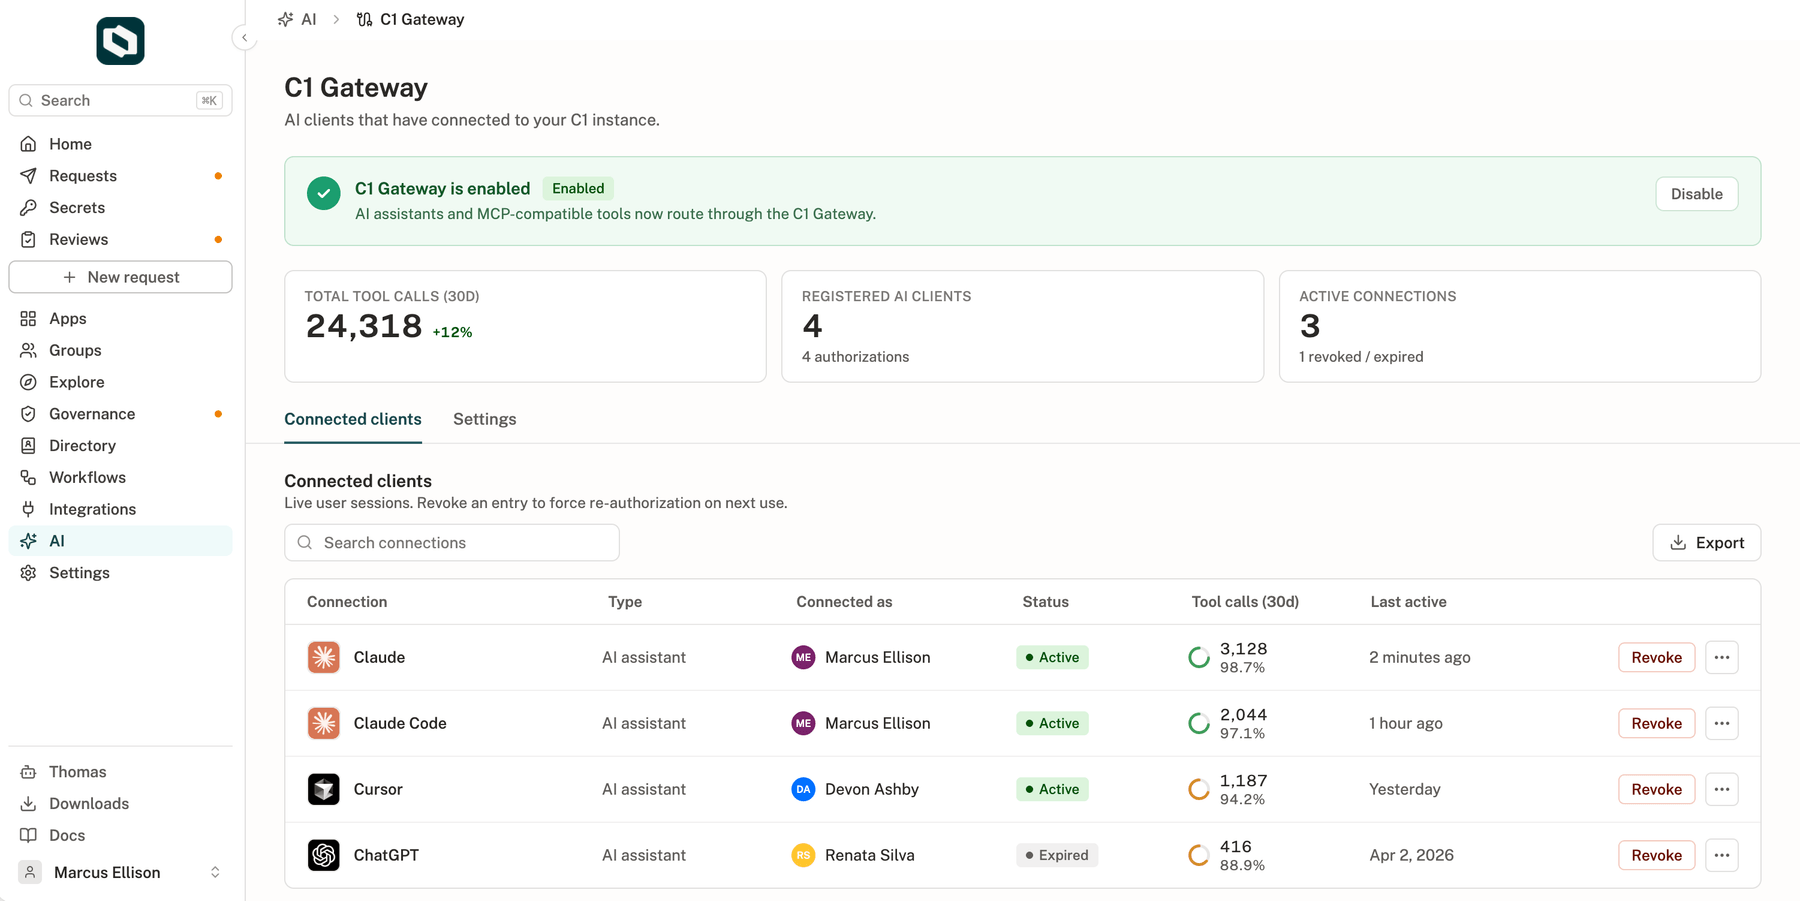
3000+ out of the box MCPs with identity-aware access controls.
Connect agents to every approved tool
Give agents and AI clients one governed path to approved MCP servers, SaaS, APIs, databases, and on-prem systems.
Enforce policy on every action
Evaluate identity, current access, action risk, and company policy on every call. Auto-approve low-risk work, require approval for higher-risk actions, and deny anything outside policy.
Capture every decision and outcome
Record the caller, tool, requested action, policy decision, approval, and outcome for investigations, access reviews, and audits.
TOOL MANAGEMENT
New AI tools, governed in minutes.
How it works
Authenticate to C1 once, and it brokers access to every tool downstream: a single login where Cross-App Access is supported, centralized auth everywhere else.
ROLE BASED ACCESS
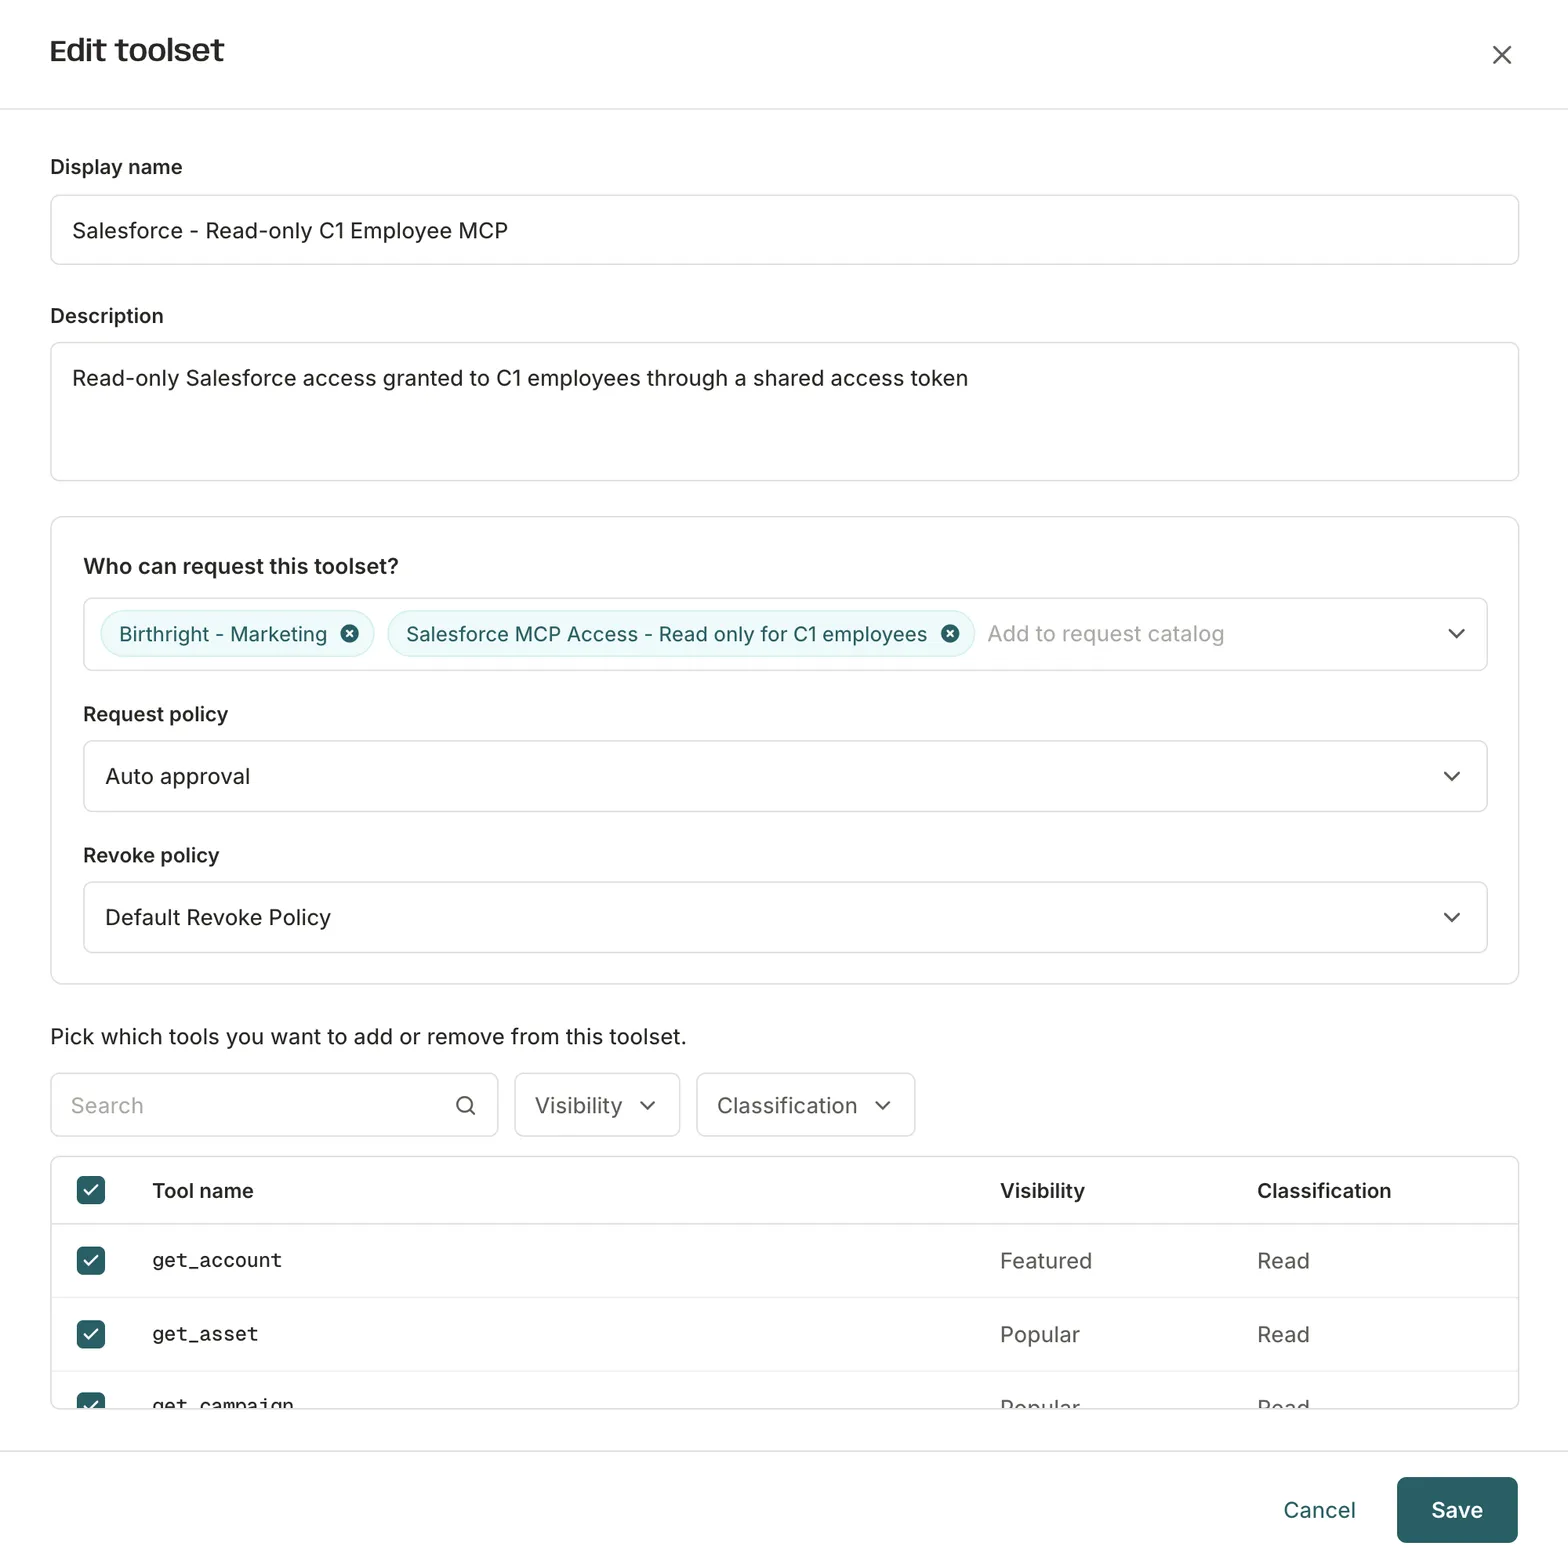
Assign access from agent identity and role.
How it works
When an agent acts for a person, start from that person's C1 identity and current grants so the agent never inherits broader access than its user.
GUARDRAILS
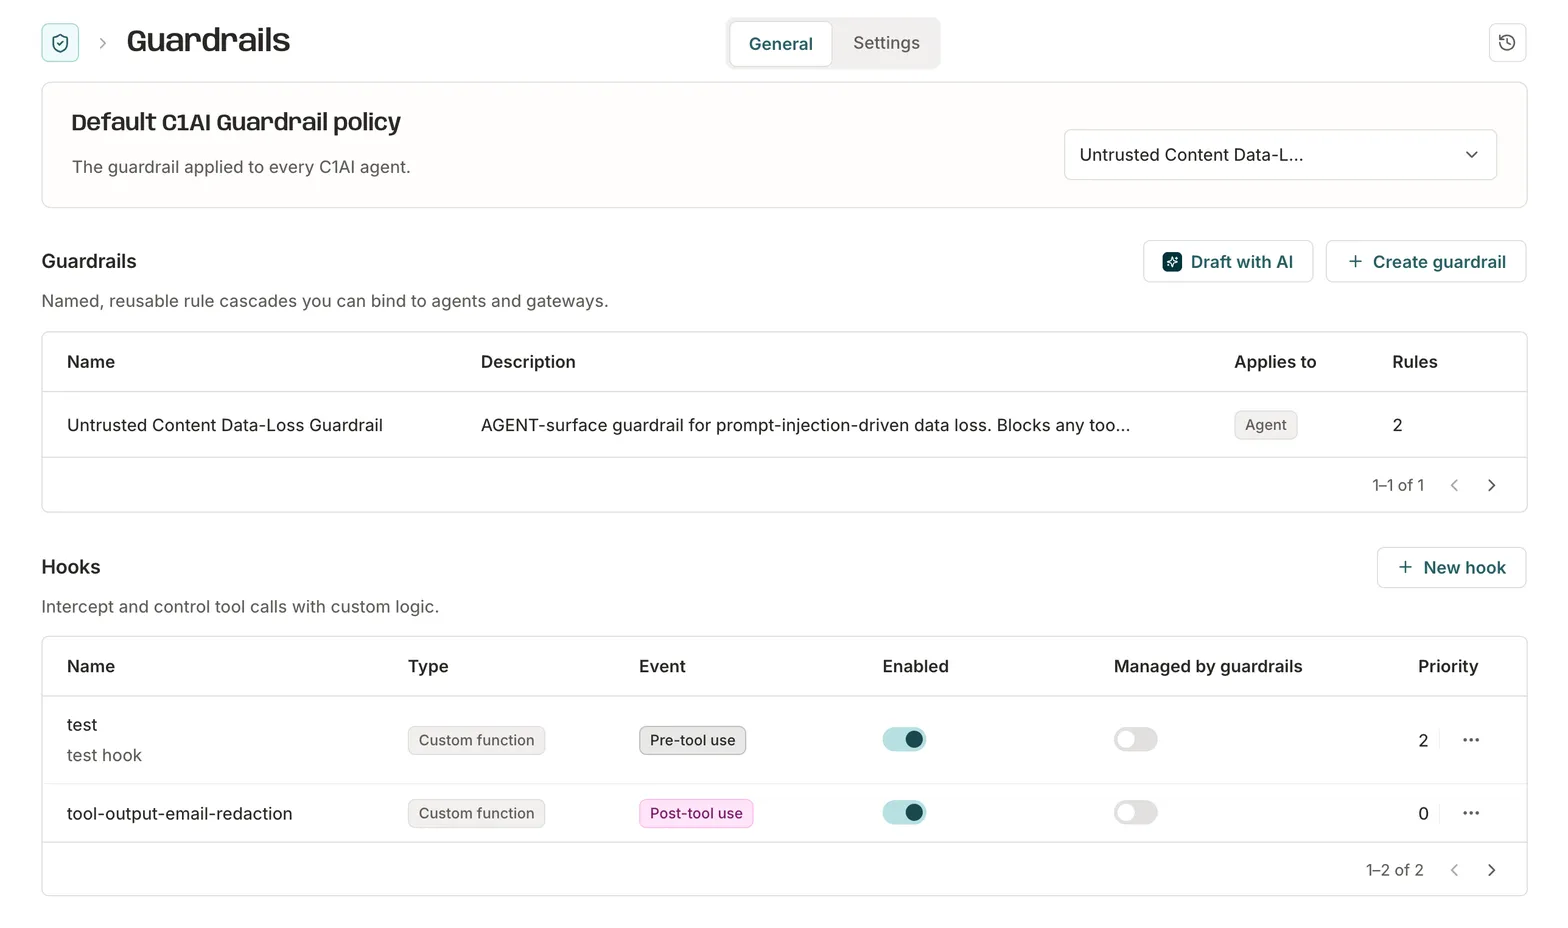
Govern the action, on every call.
How it works
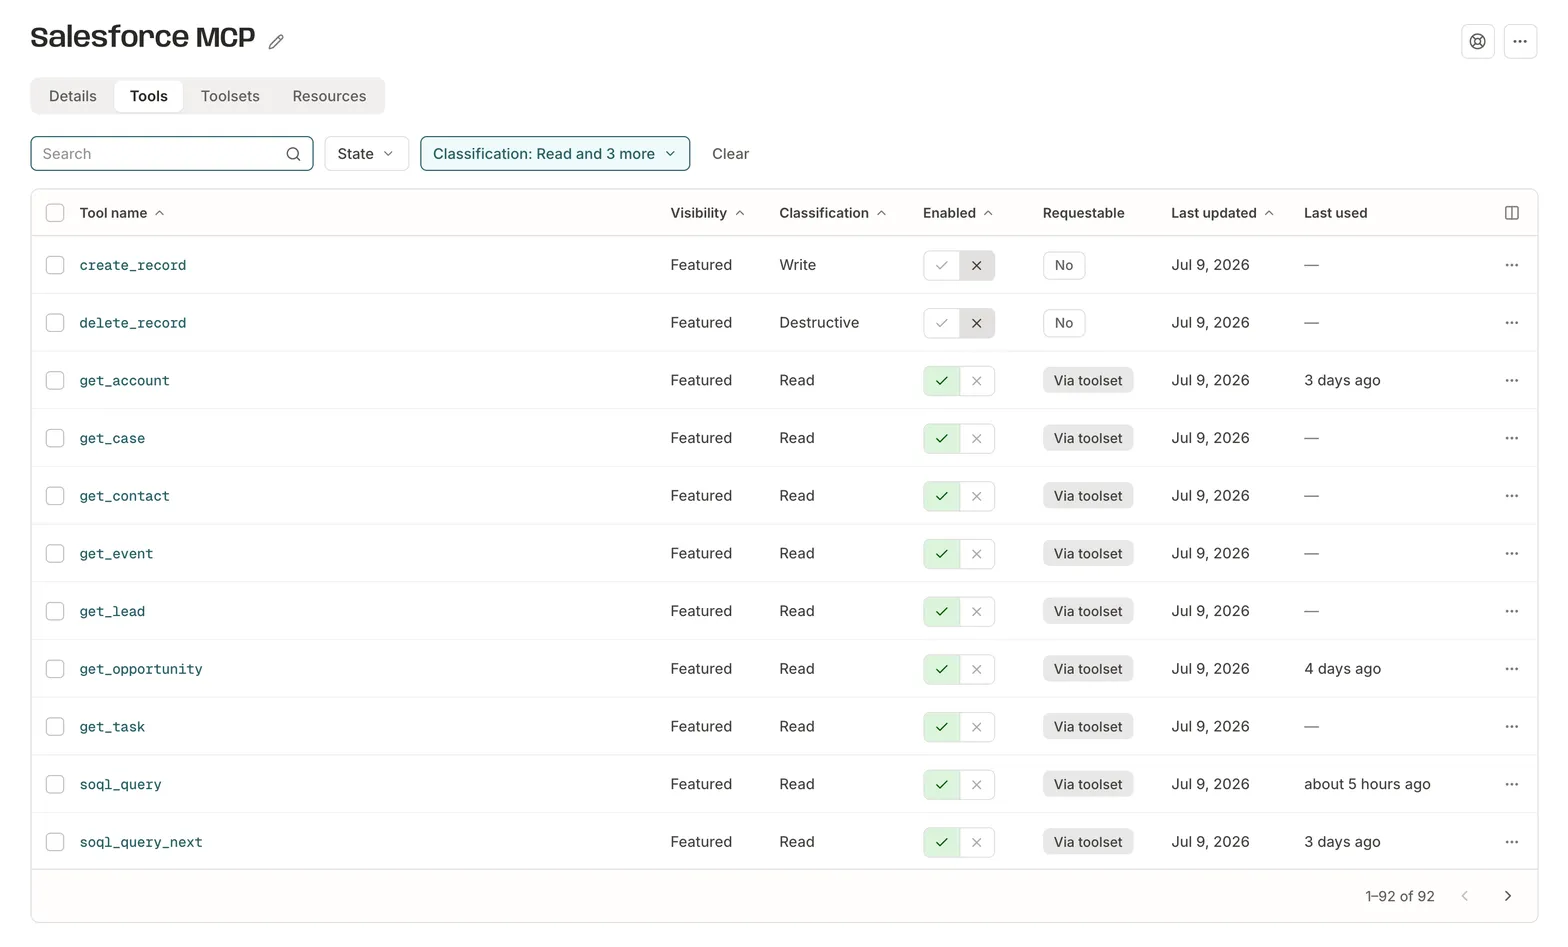
Every tool ships graded by risk. Reads auto-approve, writes route to an approver, and destructive calls are denied by default. Every grade is set by policy, so you tune it to your risk.
PERMISSION ESCALATION
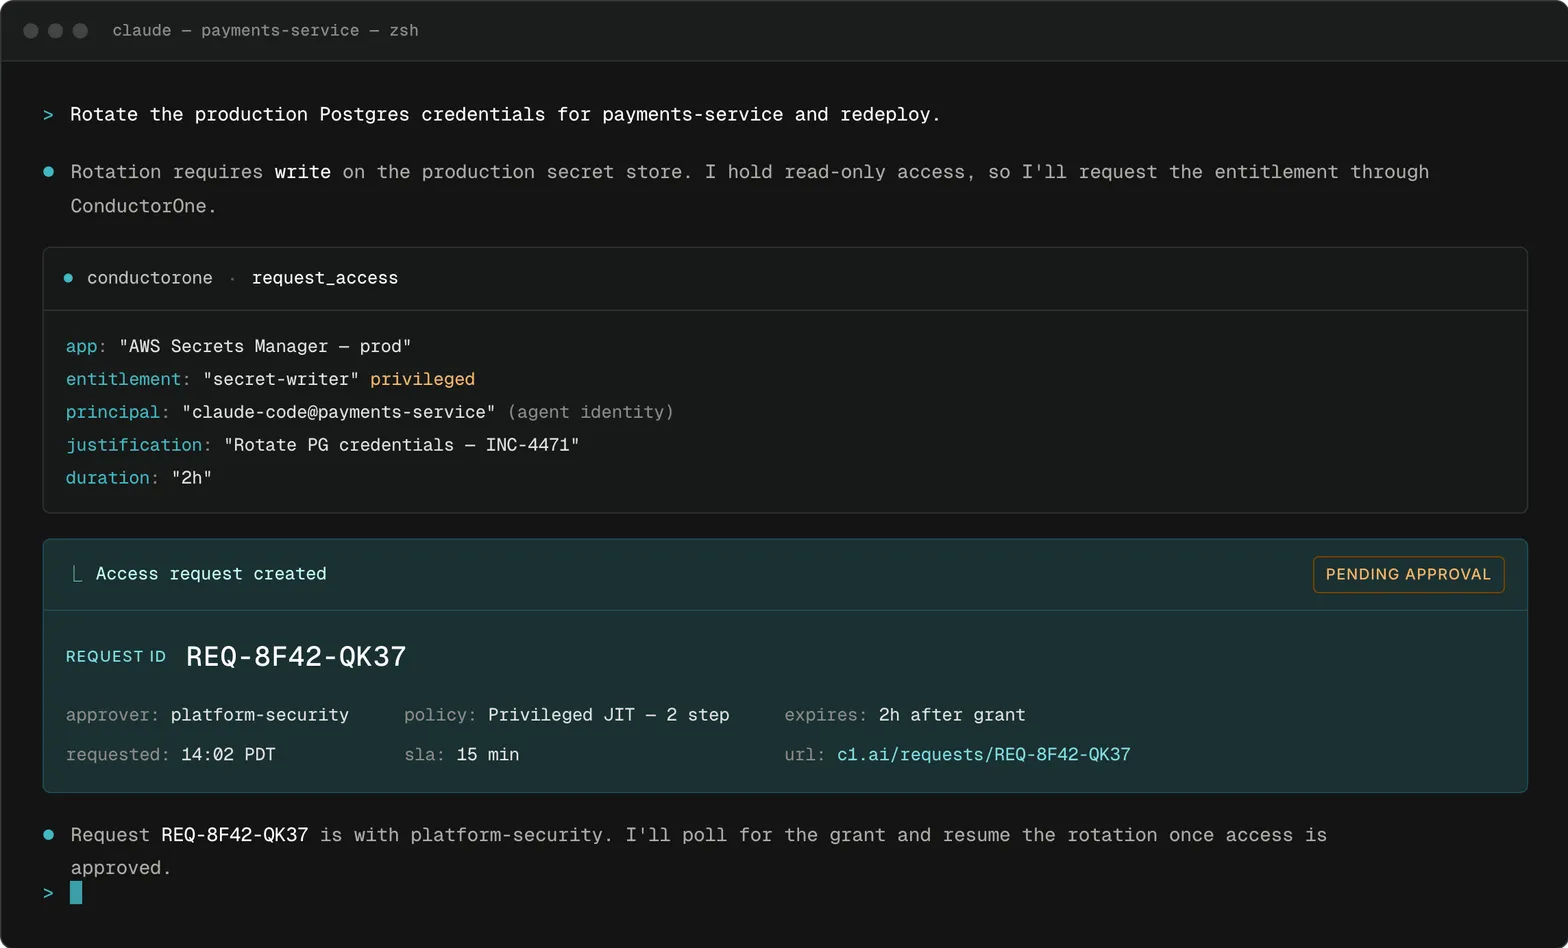
Agents escalate permissions requests seamlessly
How it works
Ask for an AI tool in Slack, Teams, the CLI, or your IDE, and policy grants it in seconds. No ticket, no wait.
SELF SERVICE MCP ACCESS
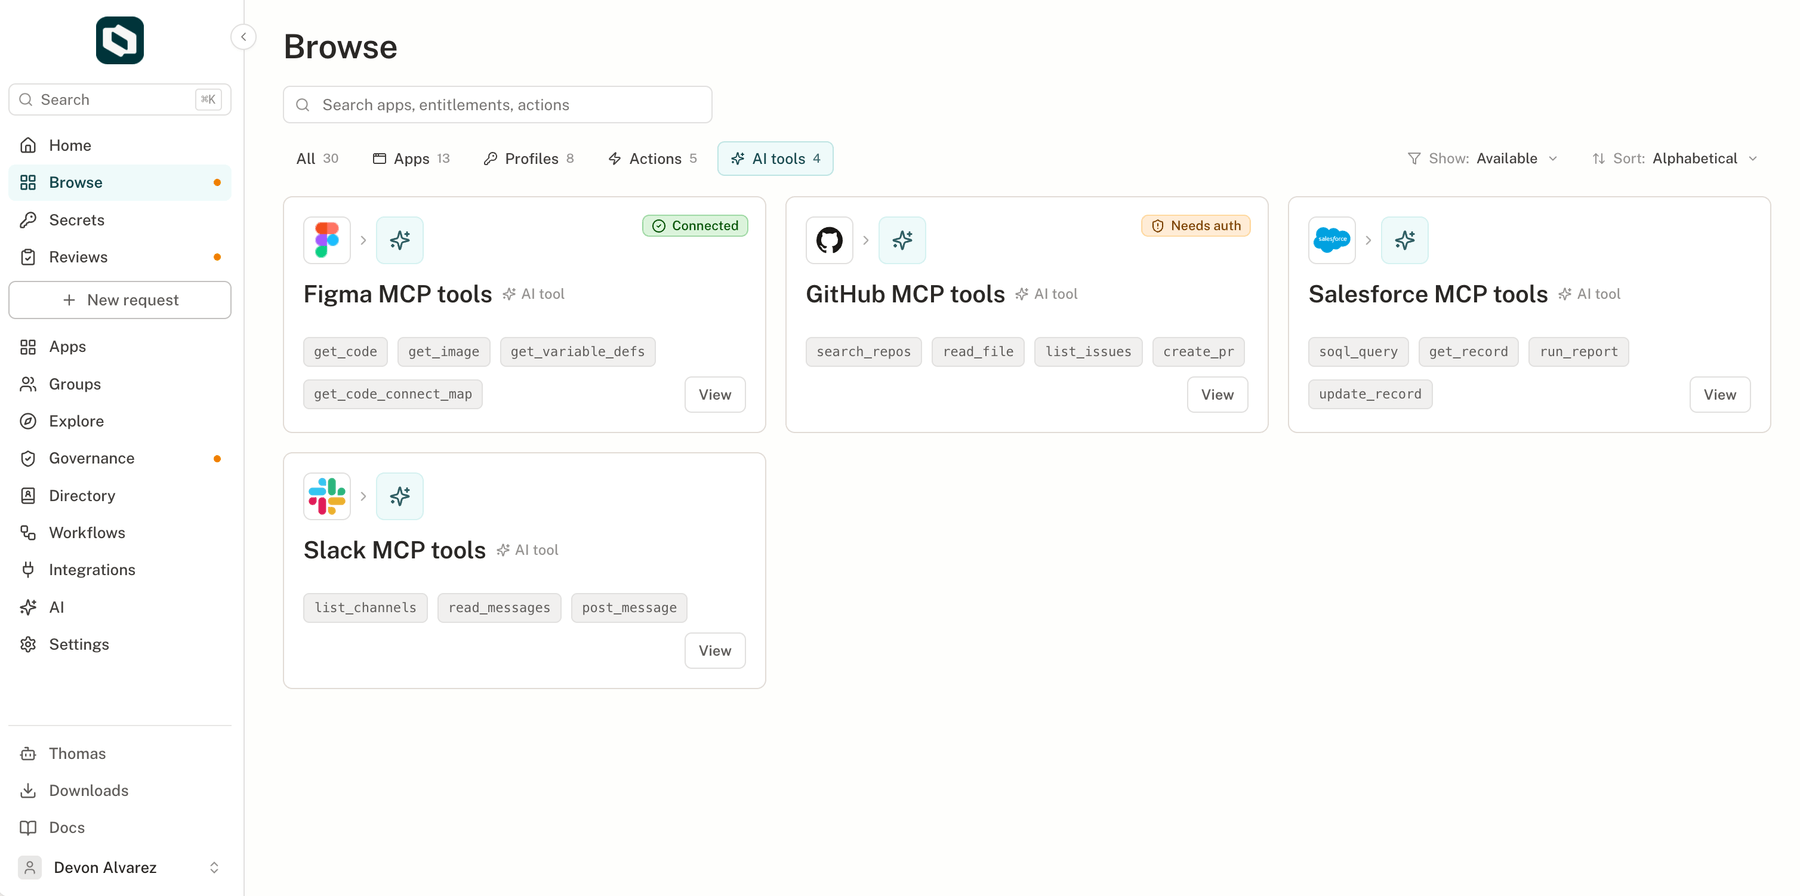
Make AI tools and MCP access self-service
How it works
Make MCP servers, toolsets, and individual tools discoverable without exposing anything that has not passed administrator review.
AUTHN & AUTHZ
Authenticate every agent. Authorize every action.
How it works
Let an agent act in a person's authorized context so every tool call starts from that user's current identity, roles, and grants.