IDENTITY GRAPH
HOW IT WORKS
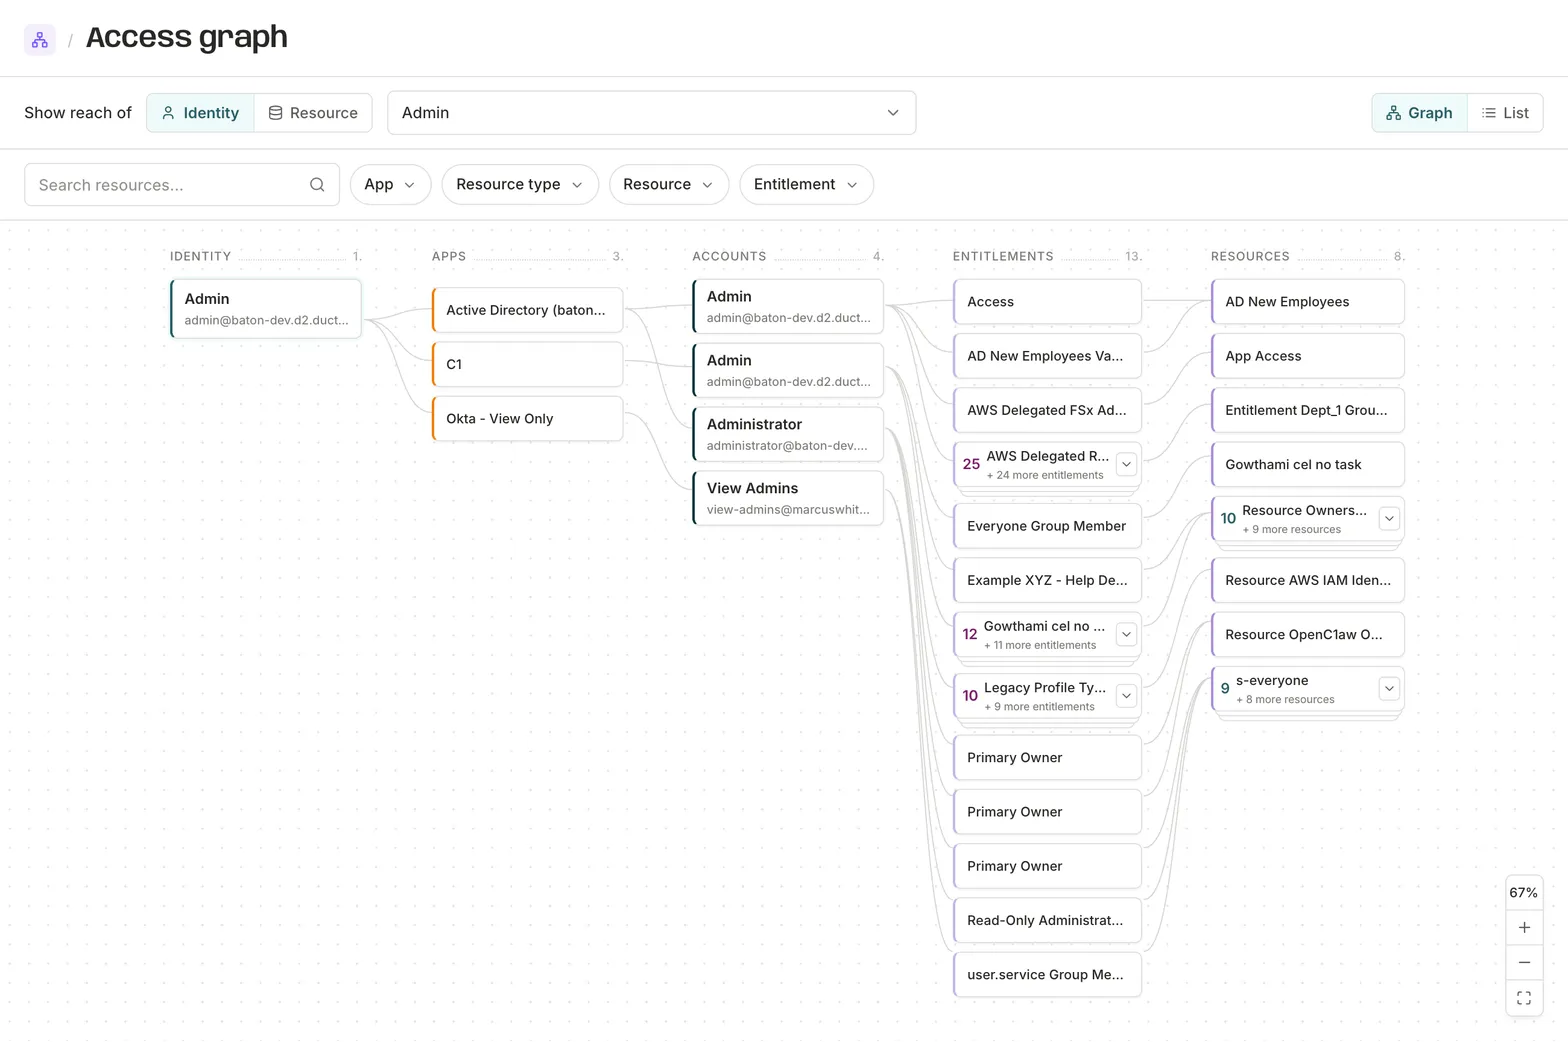
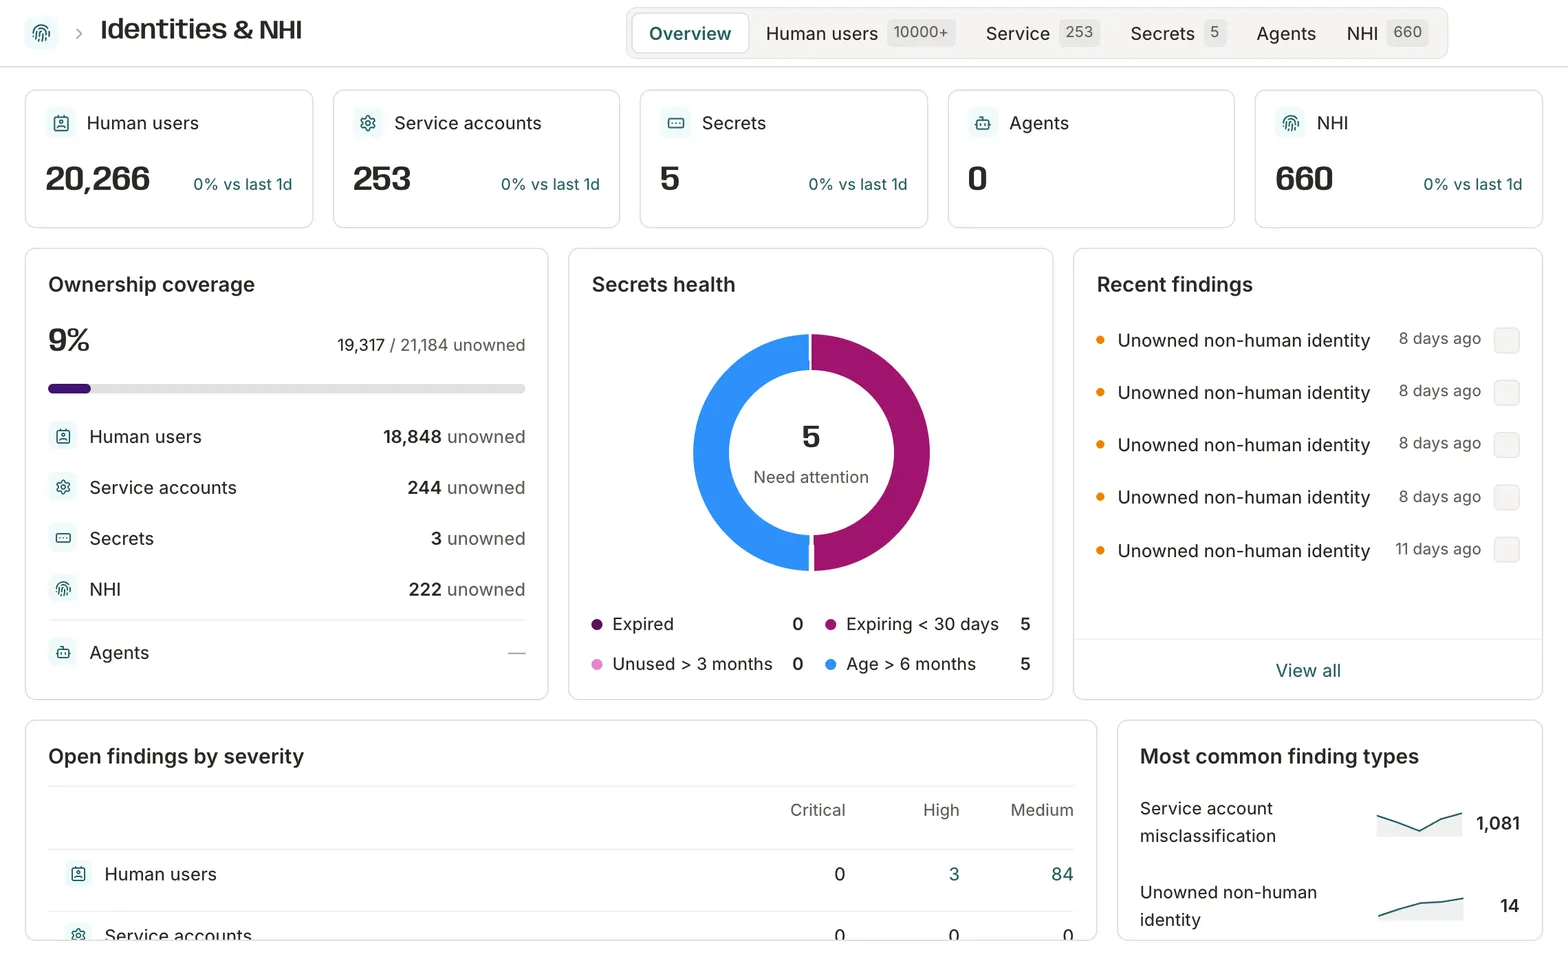
Connected records can associate a person, service account, workload, or agent with the accounts and accountable owners known to its sources.
FINDINGS
HOW IT WORKS
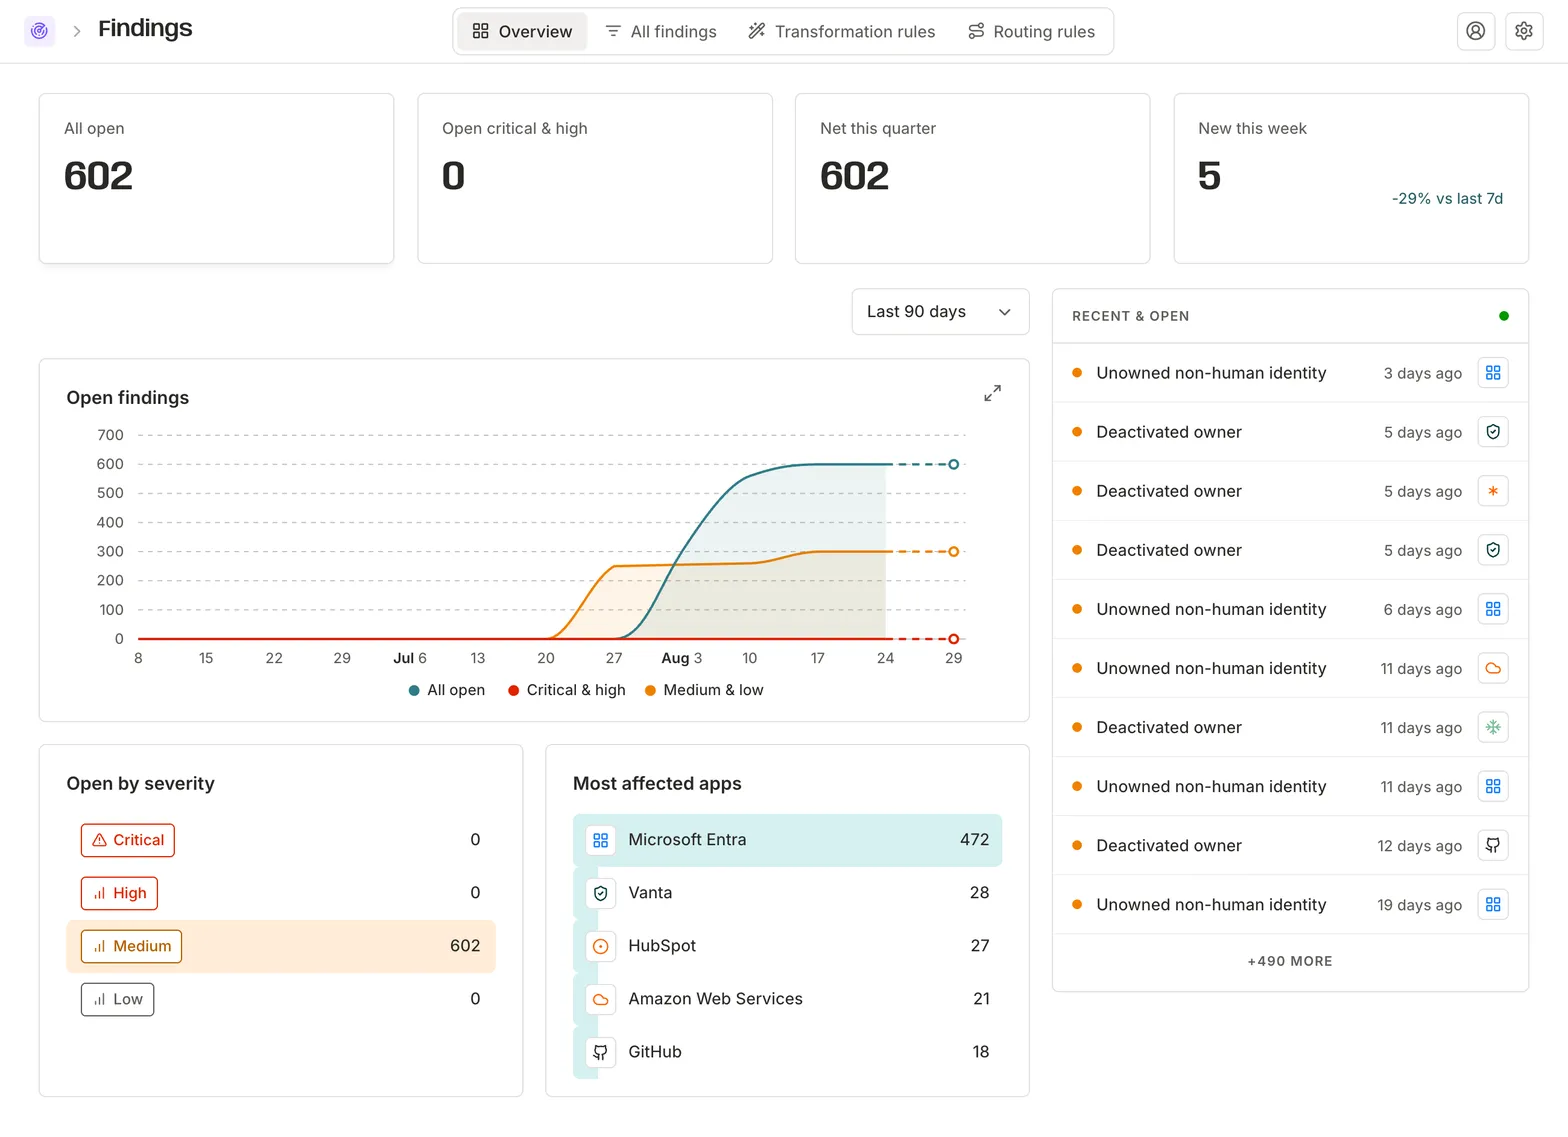
Findings can flag issues such as unowned accounts, identity misclassification, lookalike records, risky access, or a decoy credential in use when the connected data supports that signal.
DECOYS
How it works
C1 vends credentials that look exactly like real ones but belong to no legitimate workload: human and service-principal credentials, connector credentials, access tokens, and federation trusts. Each authenticates against C1-monitored endpoints, so any use is observable.

NHI and agent visibility
HOW IT WORKS
Supported connectors can ingest and categorize service accounts, keys, tokens, certificates, workloads, and other non-human identities from selected cloud and on-prem systems.
400+ Identity connectors
How it works
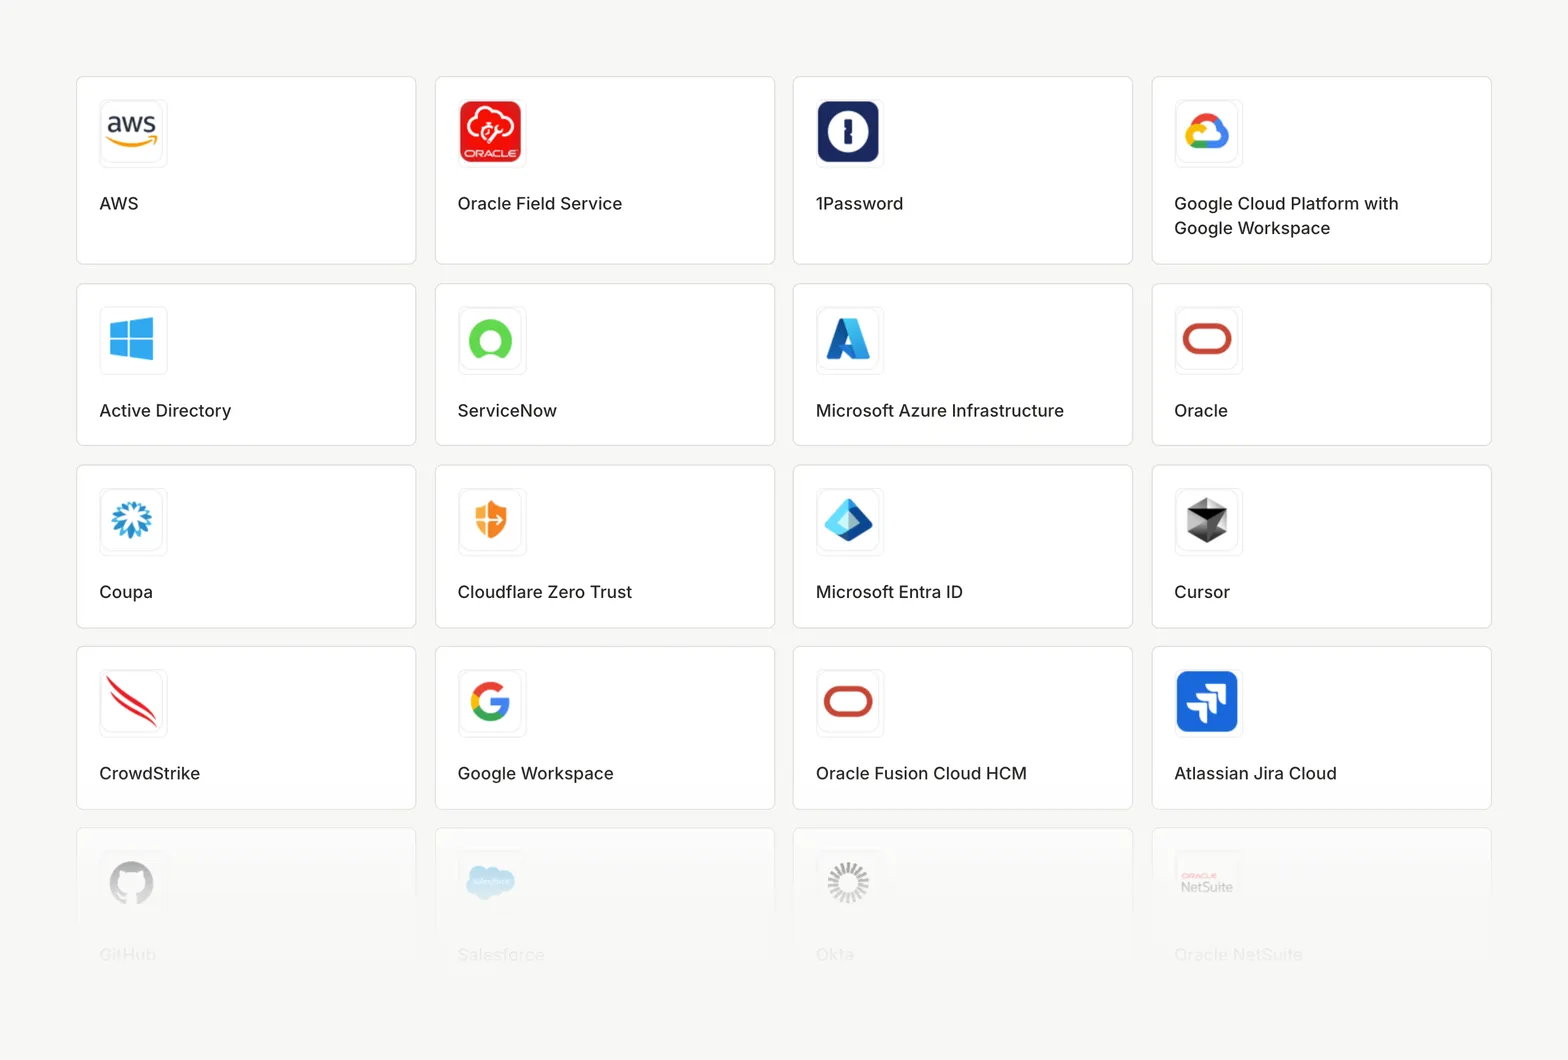
Deploy prebuilt connectors for directories, HR systems, business applications, cloud platforms, databases, and private infrastructure.
3000+ MCP connectors
How it works
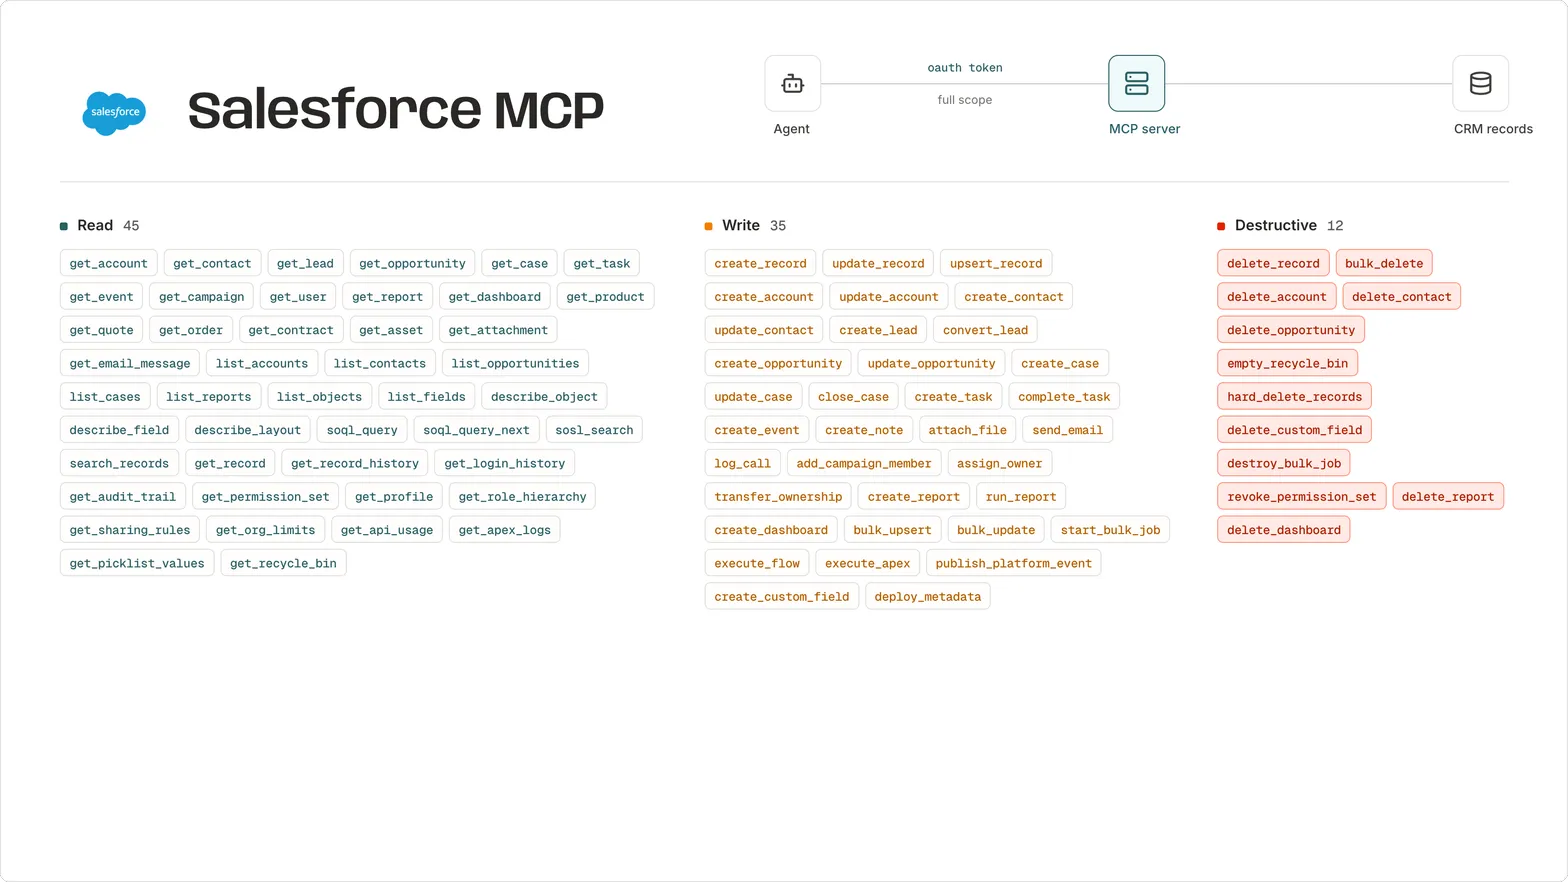
Select from the C1 catalog or register an MCP server directly, then discover its available tools and actions.
Extensibility and developer tooling
How it works
Query identity data, integrate C1 into internal services, and invoke supported operations through the REST API and generated SDKs.