


User Provisioning: How Automated Provisioning and Deprovisioning Work


User provisioning is the process of creating, updating, and removing user accounts and access rights across an organization's applications and systems, based on who the user is and what their role requires. Automated user provisioning runs that process from a source of truth, usually an HR system, so access changes without tickets or manual steps.
This guide is for IT admins and IAM engineers who run provisioning today and want to know where manual work still hides, how SCIM and connectors fit together, and what changes when the accounts you provision belong to AI agents and service accounts. Provisioning is a core function of identity governance and administration (IGA), so we cover the governance side too: who should have access, and how you prove it.
What is user provisioning?#
User provisioning gives a person the accounts and permissions they need to do their job. It also covers the changes that follow: a new team, a new manager, a leave of absence, a departure. The same discipline that creates an account on day one removes it on the last day.
In IGA terms, provisioning is the enforcement step. Policy decides who should have what. Provisioning makes it true in the target system. If the two drift apart, you get over-privileged users, orphaned accounts, and findings in your next audit.
Provisioning follows the identity lifecycle, usually described as joiner, mover, leaver:
- Joiner. A new hire or contractor needs accounts, group memberships, and application access on day one.
- Mover. A role or department change adds access the person now needs and removes access they no longer need. Skipping the removal half is how privilege creep starts.
- Leaver. A departure or end of contract means every account and entitlement is revoked, and the action is recorded.
For more on each stage, see our guides to identity lifecycle management and the joiner, mover, leaver process. For the shorter definition, see the glossary entry on user provisioning and deprovisioning.
Manual vs. automated provisioning#
Manual provisioning means a person acts on each request: a manager emails IT, IT opens a ticket, and an admin creates accounts in each application by hand. It works at small scale and fails predictably as application count and headcount grow. Automated provisioning replaces the handoffs. An HR event or an approved request triggers rules, and connectors carry out the change.
| Factor | Manual provisioning | Automated provisioning |
|---|---|---|
| Trigger | Email, ticket or chat message | HR event, approved request or policy change |
| Day-one access | Depends on admin availability | Ready when the start date arrives |
| Consistency | Varies by admin and by how the request was worded | The same rule gives the same result every time |
| Leaver handling | Easy to miss apps nobody remembers | Revokes across every connected system and logs it |
| Audit evidence | Reconstructed from tickets and screenshots | Generated as a by-product of each change |
| Where it breaks | Volume, turnover and tribal knowledge | Bad source data, missing connectors, unowned rules |
Automation does not remove judgment. It moves judgment from every request to the rules, which you can review, test and audit. Sensitive access still deserves an approval step, handled as a workflow rather than an email thread.
How automated provisioning works: SCIM, connectors, birthright rules#
Every automated setup has four parts: a source of truth, a rules engine, a delivery layer and a record of what happened. An HR event reaches the identity platform, rules decide which access applies, SCIM or a connector delivers it to each app, and every change is logged. Leavers follow the same path in reverse.
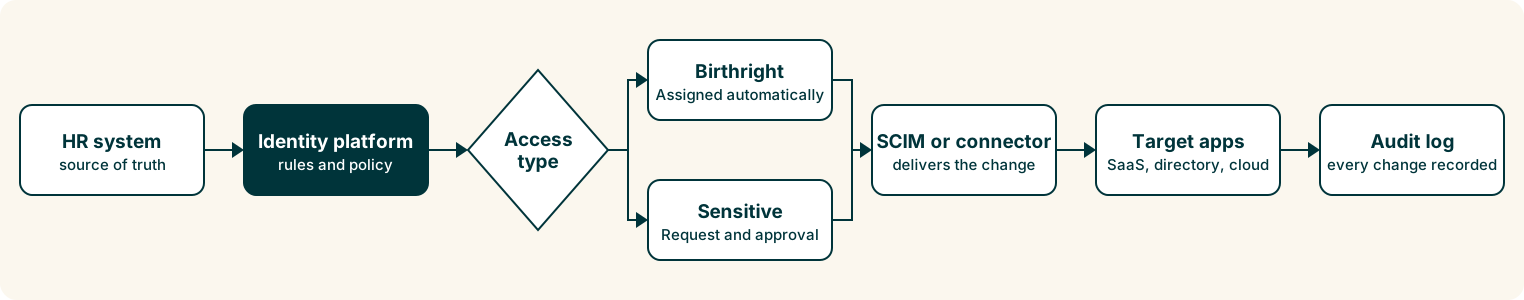
An HR event reaches the identity platform, rules decide which access applies, SCIM or a connector delivers it to each app, and every change is logged. Leavers follow the same path in reverse.
The source of truth#
Most teams use the HR system as the authoritative source because it knows when someone is hired, changes role, goes on leave or leaves. The common failure is unclean source data: a missing department field or a late termination entry makes automation do the wrong thing quickly. Fix attributes at the source before you automate on top of them.
SCIM#
SCIM, the System for Cross-domain Identity Management, is the open standard that lets an identity system and an application exchange account data in a common format. RFC 7644 defines an HTTP-based protocol with GET, POST, PUT, PATCH and DELETE operations on endpoints such as /Users and /Groups, and RFC 7643 defines the JSON schema, including core User and Group resources.
In practice, the identity system sends a POST to create a user, a PATCH to change attributes, and sets active to false or sends a DELETE to deactivate. Implementations vary between vendors, especially for group membership, so test each app. Our SCIM provisioning guide covers the schema, limits and security practices.
Connectors#
Not every application supports SCIM. A connector is the integration layer between the identity platform and a target system, built on that system's own API, database or directory protocol. A good connector reads existing accounts and entitlements, writes changes and reports failures. When evaluating coverage, ask whether it reads entitlements as well as accounts, so access reviews see real permissions, and what happens to systems with no connector.
Birthright rules#
Birthright access is the baseline access a person receives automatically because of their role, department or location, not because they asked for it. A rule is an attribute condition plus the access it grants. An illustrative example for a new finance hire:
| Rule | Condition (from HR data) | Access granted | Needs approval? |
|---|---|---|---|
| Everyone | Status is active employee | Email, chat, directory, HR portal | No |
| Finance team | Department is Finance | Finance shared drive, expense tool, accounting system (standard role) | No |
| Finance, elevated | Request by user or manager | Payment approval and journal entry permissions | Yes, manager and system owner |
On the start date the first two rules fire and the new hire logs in to a working environment. The third never fires on its own, because payment permissions are sensitive and combine badly with other finance access under separation of duties. If the person later moves to Sales, the department-based rules run in reverse: Finance access is removed and Sales access is added. Keep birthright rules narrow, since a rule that grants too much on day one is over-provisioning by design.
Deprovisioning and orphaned accounts#
User deprovisioning is the removal or disabling of a person's accounts and entitlements when they leave or change roles. It gets the least attention and causes the most audit findings. An orphaned account is an active account with no current owner, such as one belonging to someone who left or a test account nobody closed. Valid credentials attached to a nonexistent person are an easy way in.
Accounts usually become orphaned through manual offboarding that misses departmental tools and vendor portals, late or missing HR data, local accounts that sit outside SSO, or role changes where only the add side was automated.
To reduce them:
- Trigger from HR, not from a ticket. The termination event should start the workflow without anyone remembering to ask.
- Disable first, delete later. Disable accounts at the effective time, keep data for a defined retention window, then delete.
- Record every action. Each revoked account and entitlement should leave evidence of what was removed, when and by which workflow.
- Surface what the workflow missed. Compare active accounts in each app against active employees on a schedule. Anything unmatched is an orphan candidate.
- Close the loop with reviews. Periodic user access reviews catch what automation did not.
Provisioning for agents and service accounts#
AI agents, bots, API integrations and service accounts need credentials and permissions too, and they do not appear in the HR system. That removes the trigger most provisioning depends on. Service accounts often have broad permissions, long-lived secrets and no named owner, and agents can be created quickly by individual teams. An unmanaged agent can outlive the project that created it.
What carries over from human provisioning:
- An owner for every identity. Record an accountable human or team at creation, and flag identities for reassignment when the owner leaves.
- A source of truth. Without HR, the registry of agents and service accounts becomes the authoritative list. Provision from it and reconcile against what is actually running.
- Least privilege. Grant the narrowest scope that does the job, and prefer short-lived or just-in-time credentials over standing secrets.
- A defined end. Set an expiry or review date at creation.
- Deprovisioning. Revoke credentials and permissions when the workload retires, and log it the way you would for a person.
Treat these as the same lifecycle with a different trigger. When you evaluate any platform, ask whether agents and service accounts appear in the same inventory and reviews as human users, or in a separate tool. For more, see agentic identity governance.
How the top provisioning platforms compare#
Automated provisioning works when three things are true. An authoritative source, usually your HR system, triggers changes. Rules map attributes like department and job title to access. Connectors or SCIM push those changes into each application, and the same path removes access when someone leaves.
The platforms below all automate some or all of that. Which one fits depends on your environment.
| Platform | How it provisions (per vendor documentation) | Best fit |
|---|---|---|
| C1 | HR and directory events trigger account and access changes across supported systems, with removal and an action record at offboarding. Covers employees and AI agents. | Teams that want one identity governance model for people and agents |
| SailPoint | Lifecycle states grant or revoke access based on employment status. Roles grant access by job function. Sources with a direct connection are provisioned automatically. | Large enterprises already standardized on SailPoint |
| Saviynt | REST connector with SCIM support pushes changes to apps, imports users and access, and can disable or delete accounts. | Teams that need SCIM-based and API-driven integrations |
| Okta Lifecycle Management | Automates account management using pre-built Okta Integration Network apps or custom API connections, and uses SCIM between Okta and apps. | Organizations that already use Okta as the identity provider |
| Microsoft Entra ID Governance | Lifecycle Workflows automate joiner, mover, and leaver tasks. Requires an Entra ID Governance or Entra Suite license. | Microsoft-centric environments |
| One Identity Manager | Describes automated provisioning to on-premises and cloud targets, with role management. | Hybrid estates with significant on-premises targets |
Capabilities change often. Check each vendor's documentation before you shortlist.
FAQ#
What is user provisioning?#
User provisioning is the process of creating, updating, and removing user accounts and access rights across applications and systems. It covers the full lifecycle: joiner, mover, and leaver. Automated provisioning triggers these changes from an authoritative source such as an HR system.
What is the difference between provisioning and deprovisioning?#
Provisioning creates accounts and grants access. Deprovisioning removes or disables accounts and revokes access when someone leaves or changes roles. Both belong to the same workflow, and deprovisioning is where most orphaned accounts and audit findings come from. See the provisioning and deprovisioning glossary entry.
Do I need SCIM to automate provisioning?#
No. SCIM is the simplest path when an application supports it, because you configure an endpoint and token. Applications without SCIM need a connector, an API integration, or a manual fulfillment step. Most environments use a mix. See our SCIM provisioning guide.
What is birthright access?#
Birthright access is the baseline access a person receives automatically based on attributes such as role, department, or location. It removes routine requests and gives new hires working access on day one. Keep it narrow and put sensitive access behind approval. More in our birthright access glossary entry.
How do you provision AI agents and service accounts?#
Treat them as identities with an owner, a defined scope, and an end date. Register each one at creation, grant least privilege, prefer short-lived credentials, and revoke them when the workload retires. Because they do not come from HR, the agent registry becomes the source of truth.
How do you find and remove orphaned accounts?#
Compare active accounts in each application against active employees and registered non-human identities. Anything with no matching owner is a candidate. Disable it, confirm with the app owner, and delete after your retention window. Trigger offboarding from HR events and run periodic access reviews to catch the rest.
See how C1 automates provisioning and deprovisioning#
C1 (formerly ConductorOne) is an identity governance platform that turns HR and directory events into day-one access and removes access when people leave, for employees and AI agents. Explore C1 identity governance (IGA) or book a demo.