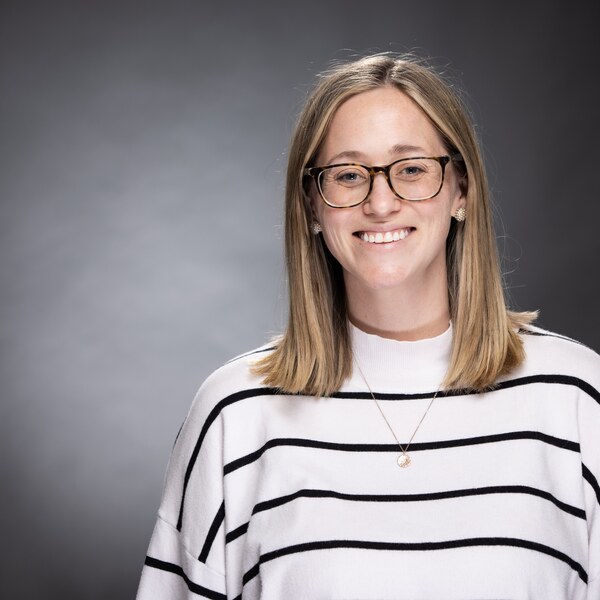
Melody Scheidler
Director of Product Marketing, C1.ai
Melody Scheidler is Director of Product Marketing at C1.ai, focused on the company's AI and agent products. Launches covered here include Agentic Vault, shadow AI discovery, and the C1 Autonomous Worker.
12 articles by Melody Scheidler
 Blog
Launch Week Roundup: The Paved Road to the Agentic Enterprise
Catch up on C1 Launch Week: AppHub, sign-in and permissions, credential vending and C1 Egress, and C1 LLM Gateway. Four launches paving the road to the agentic enterprise.
- Blog
Introducing credential vending and C1 Egress: secrets your apps never have to hold
C1 mints a scoped, short-lived credential for every workload and pairs it with C1 Egress, a governed proxy that injects the real secret at the network layer so the application never has to hold it.
- Blog
Introducing sign-in and permissions for your AI-built applications
C1.ai launches governed OIDC sign-in and real-time OpenID AuthZEN permissions for AI-built applications, replacing hardcoded logins and stale local permission tables with entitlements a company already governs.
 Blog
Anatomy of a decoy: what happens when someone uses a stolen credential
A decoy credential looks exactly like a real one and belongs to no workload, so using it is unambiguous. Here is the path a request takes through C1.ai when someone tries a planted decoy: what the caller gets back, and the critical finding that lands on your side.
 Blog
Six Domains, One Control Plane: Mapping C1.ai to SACR's ARMCF
SACR's AI and Agentic Risk Management and Control Framework (ARMCF) applies a NIST CSF-style lifecycle to AI agents. Here is how C1.ai maps to all six domains: GOVERN, IDENTIFY, PROTECT, DETECT, RESPOND, and RECOVER.
 Blog
C1 Deploy: Onboarding that does the setup for you
Most identity deployments begin with a long setup project. Ours begins with a question: what are you trying to get done first? Pick a goal, connect a directory, and C1 AI builds the plan from your live environment and runs the setup work for you, with every action gated on your approval.
- Blog
Launch Week Roundup: The Agentic Control Plane
A recap of C1 Launch Week: shadow AI discovery, Agentic Vault, agent runtime governance, and agentic security and intelligence. Four launches, one control plane for governing every AI agent, secret, and non-human identity.
- Blog
Introducing Agentic Vault: govern every secret like an identity
The C1.ai Agentic Vault secures the credentials your people, agents, and service accounts depend on, governing every secret through the same request, approval, and audit path as any other access, with post-quantum protection from day one.
- Blog
Introducing shadow AI discovery: find the AI you didn't sanction
The C1.ai shadow AI discovery helps security teams find unsanctioned AI tools, AI agents, MCP servers, and exposed credentials across cloud and endpoints, then assign ownership and govern them.
 Blog
Introducing the C1 Autonomous Worker
Introducing the C1 Autonomous Worker, an agent that runs work loops, carries state, executes code, and acts on your behalf across the full C1.ai API surface.
- Blog
Governing Cloud Infrastructure Access at Scale
C1.ai provides hierarchical access management for cloud infrastructure so users and agents can request and review access to resources the way the cloud actually models it: as a hierarchy, not a flat list.
 Blog
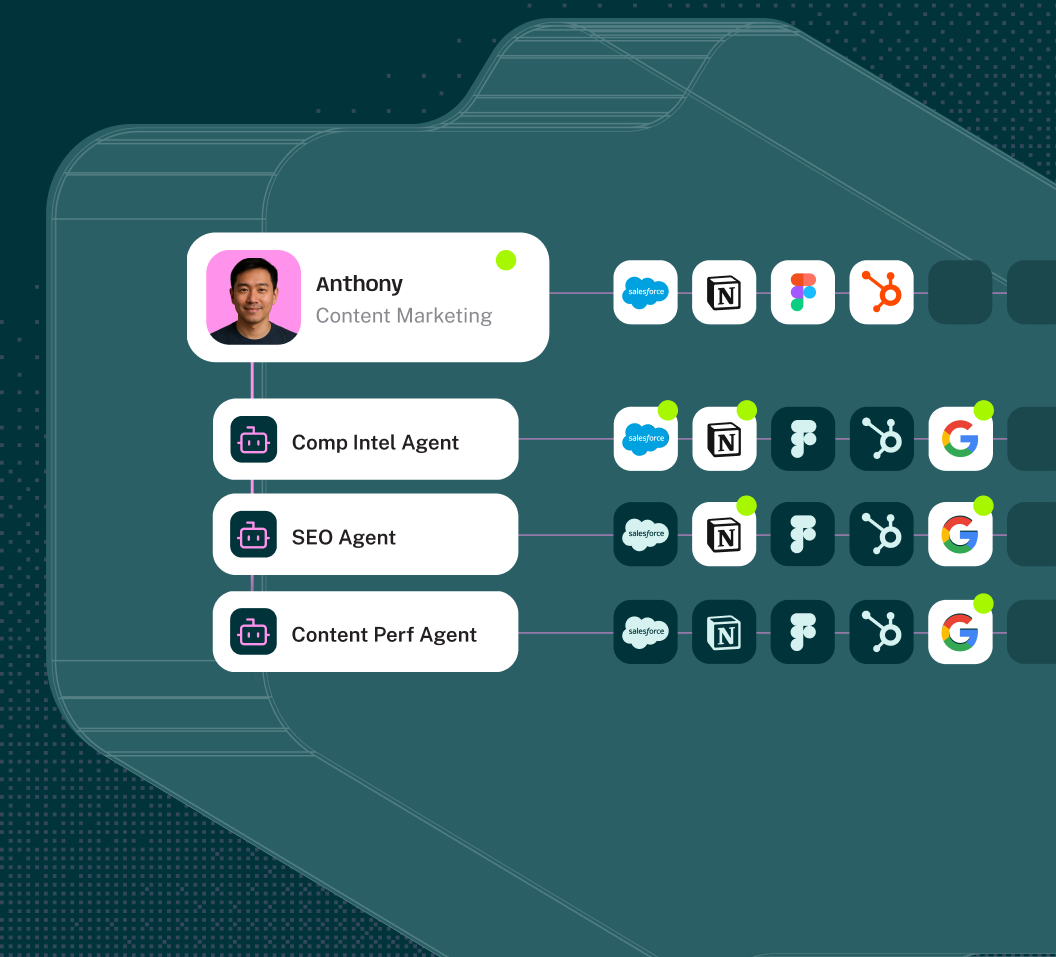
AI Access Management Is Now Generally Available
AI Access Management is generally available for all C1.ai customers. Govern how employees, personal AI assistants, and enterprise agents access enterprise tools and data — at the speed AI actually moves.