IDENTITY GRAPH
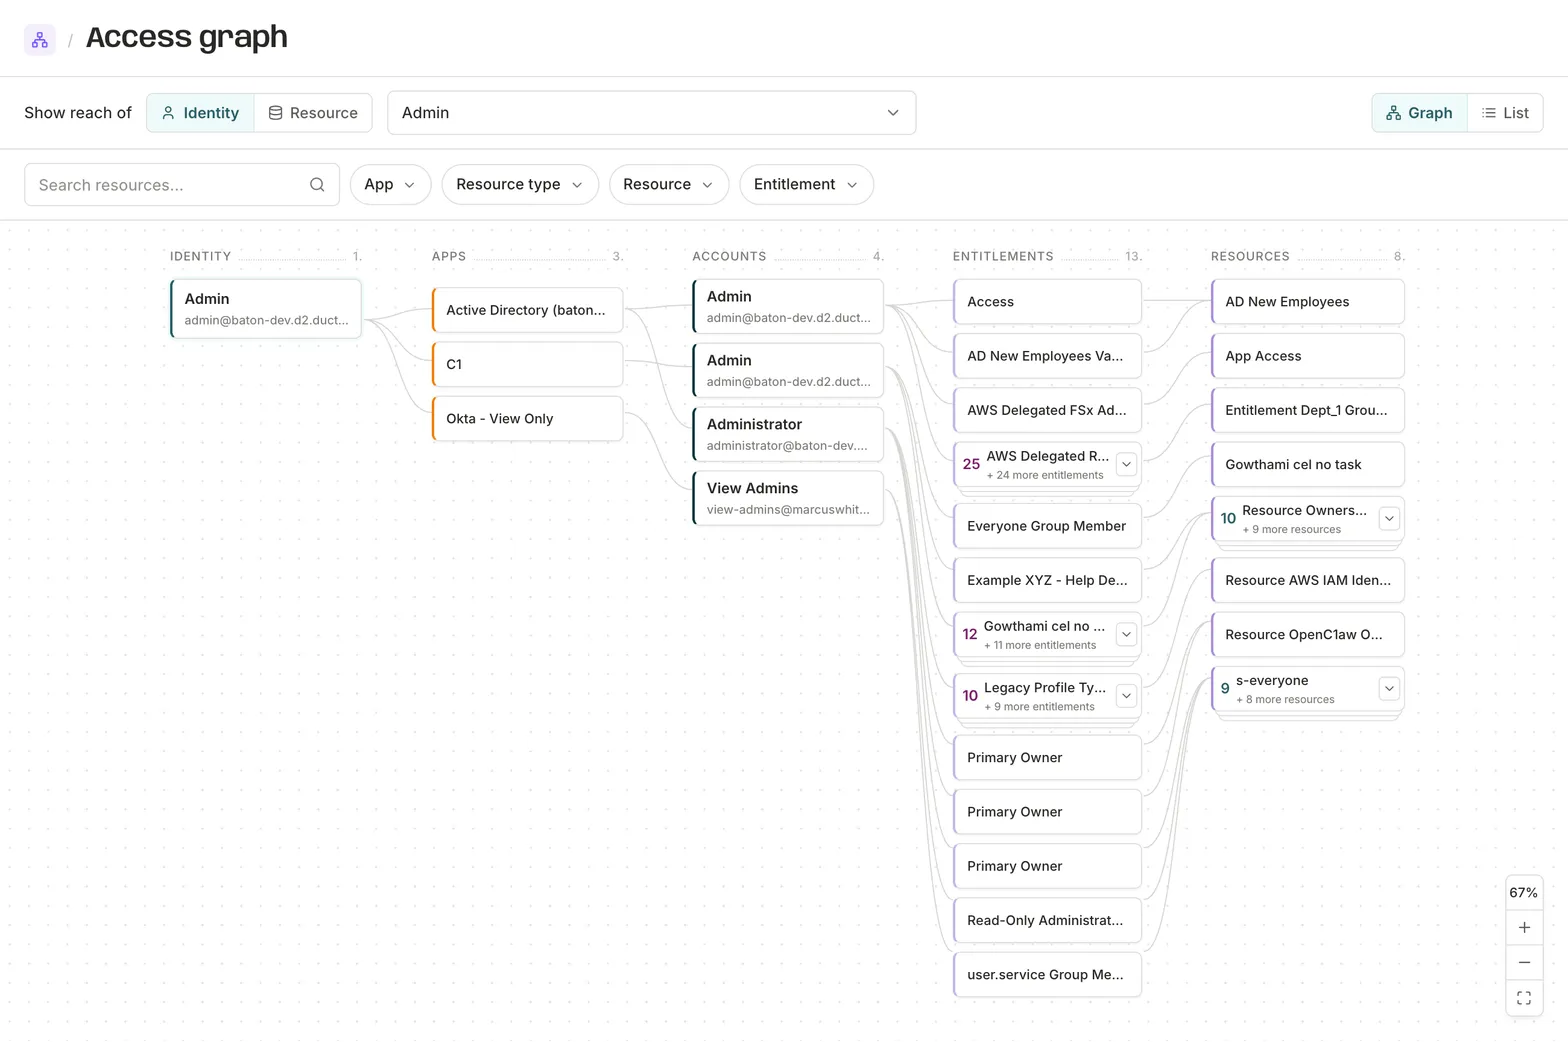
Complete visibility over every identity and entitlement
HOW IT WORKS
Connected records can associate a person, service account, workload, or agent with the accounts and accountable owners known to its sources.
FINDINGS
Detect security issues in real-time across your workforce and agents
HOW IT WORKS
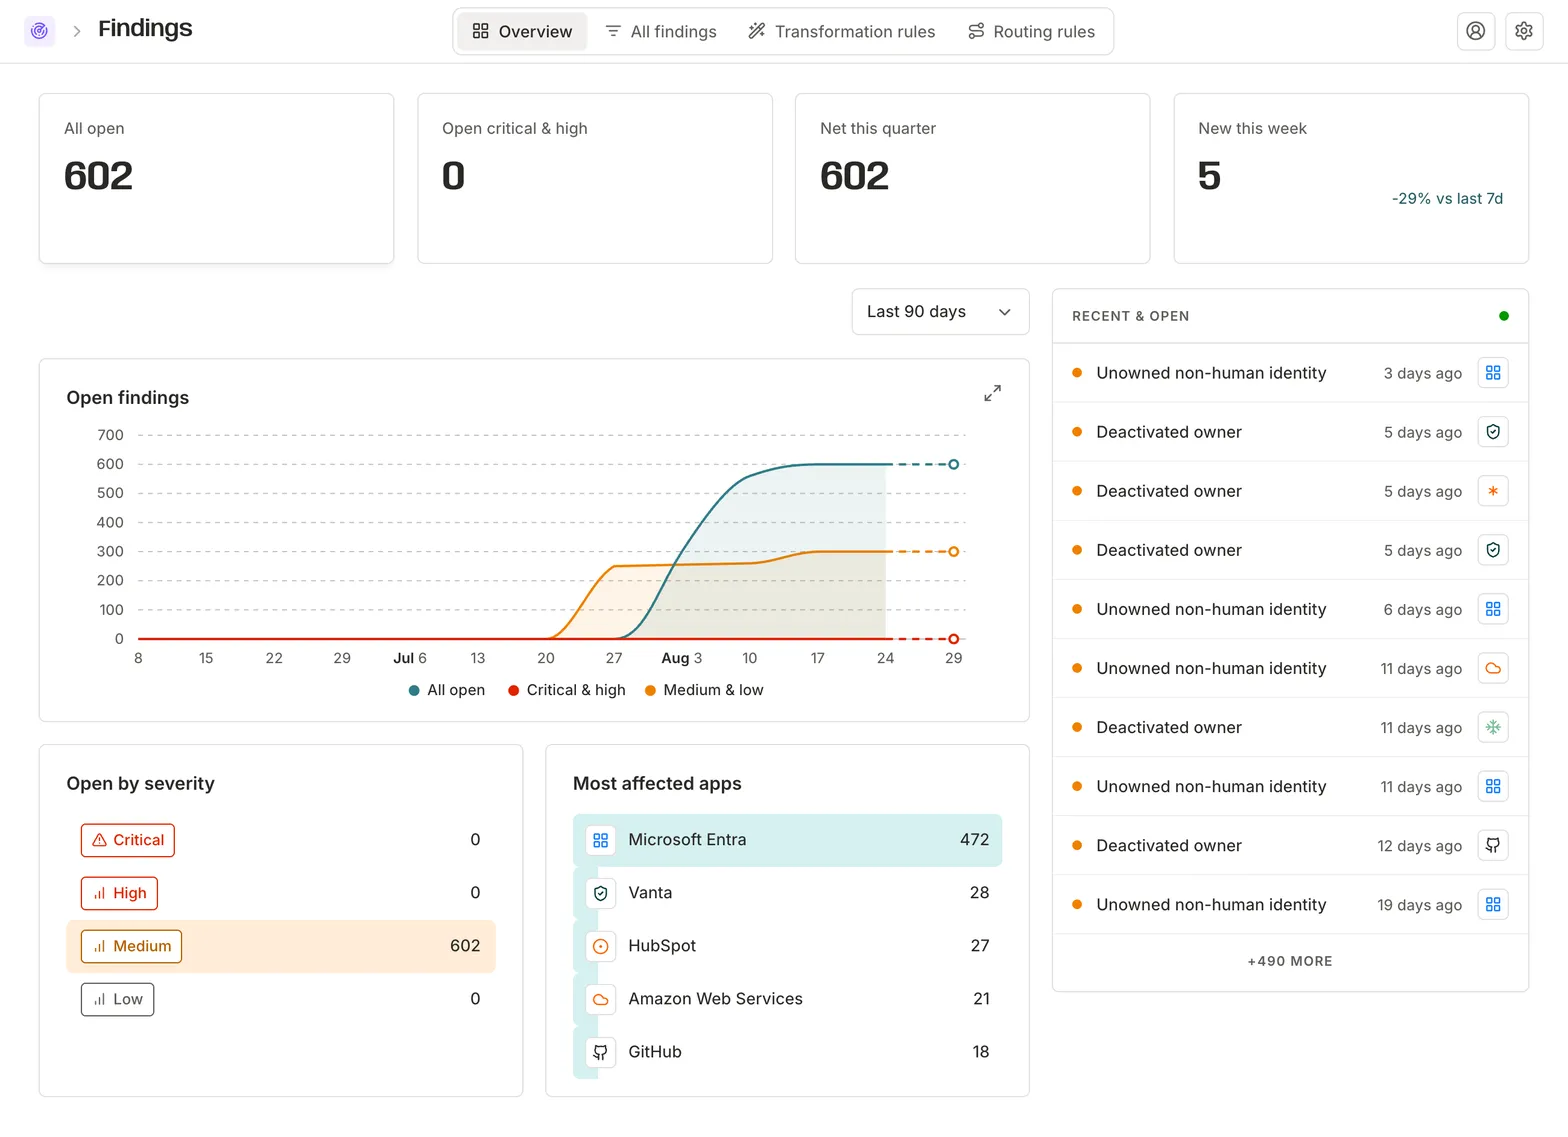
Findings can flag issues such as unowned accounts, identity misclassification, lookalike records, risky access, or a decoy credential in use when the connected data supports that signal.
DECOYS
Detect credential theft in realtime
How it works
C1.ai vends credentials that look exactly like real ones but belong to no legitimate workload: human and service-principal credentials, connector credentials, access tokens, and federation trusts. Each authenticates against C1.ai-monitored endpoints, so any use is observable.

NHI and agent visibility
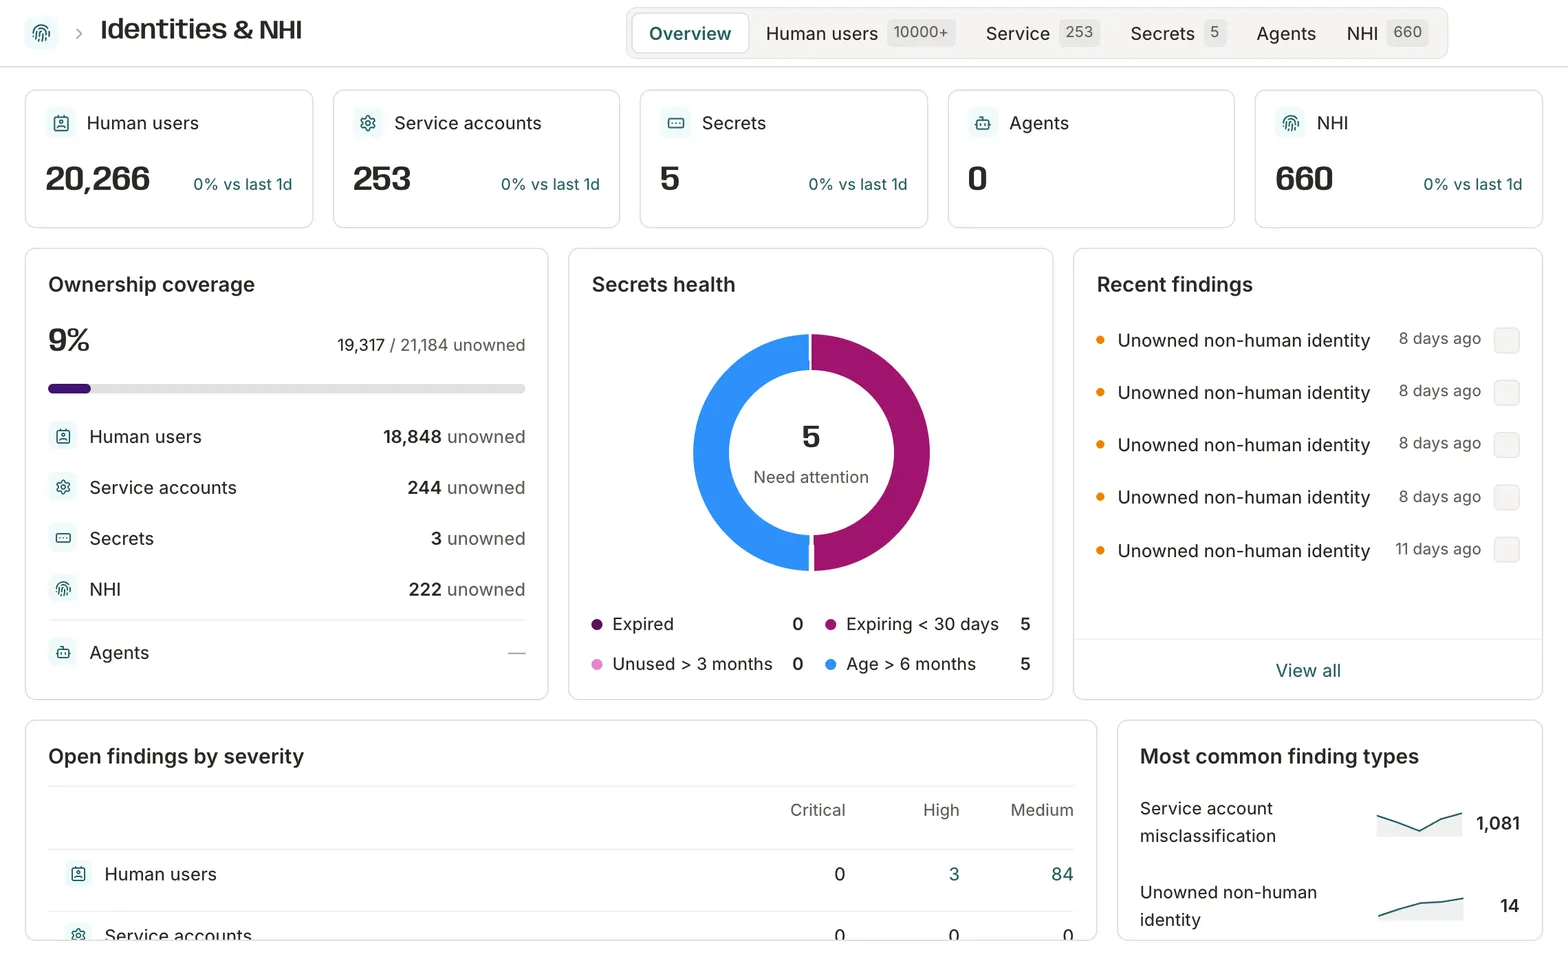
Discover every non-human identity and agent
HOW IT WORKS
Supported connectors can ingest and categorize service accounts, keys, tokens, certificates, workloads, and other non-human identities from selected cloud and on-prem systems.
APPLICATION SIGN-IN
Add governed sign-in to your AI-built apps
Stop custom writing auth. Your apps get standard OIDC sign-in, and who may sign in becomes an entitlement you already review.
HOW IT WORKS
C1 redirects to your existing IdP, then issues its own OIDC tokens to your app. Your users keep the credentials they already have. C1 holds no local authenticators.
APPLICATION AUTHORIZATION
Define permissions for your AI-built apps
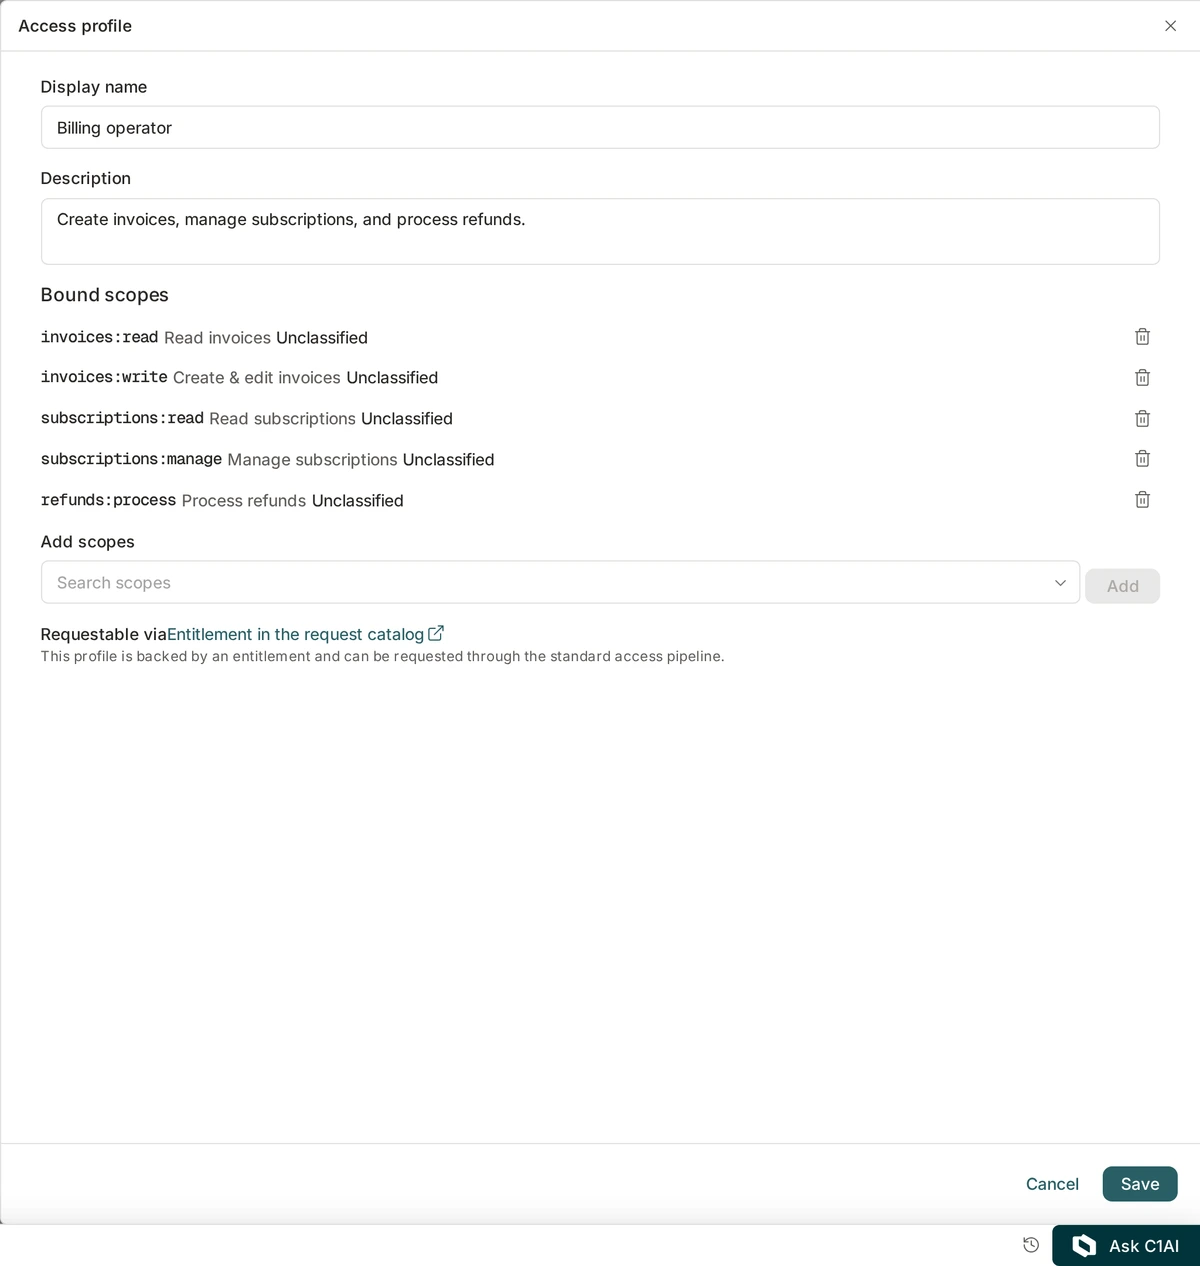
Every app you build has to know who gets to see what. Instead of copying entitlement data and watching it go stale, your app sends one request to C1 and gets a decision grounded in access you already govern.
HOW IT WORKS
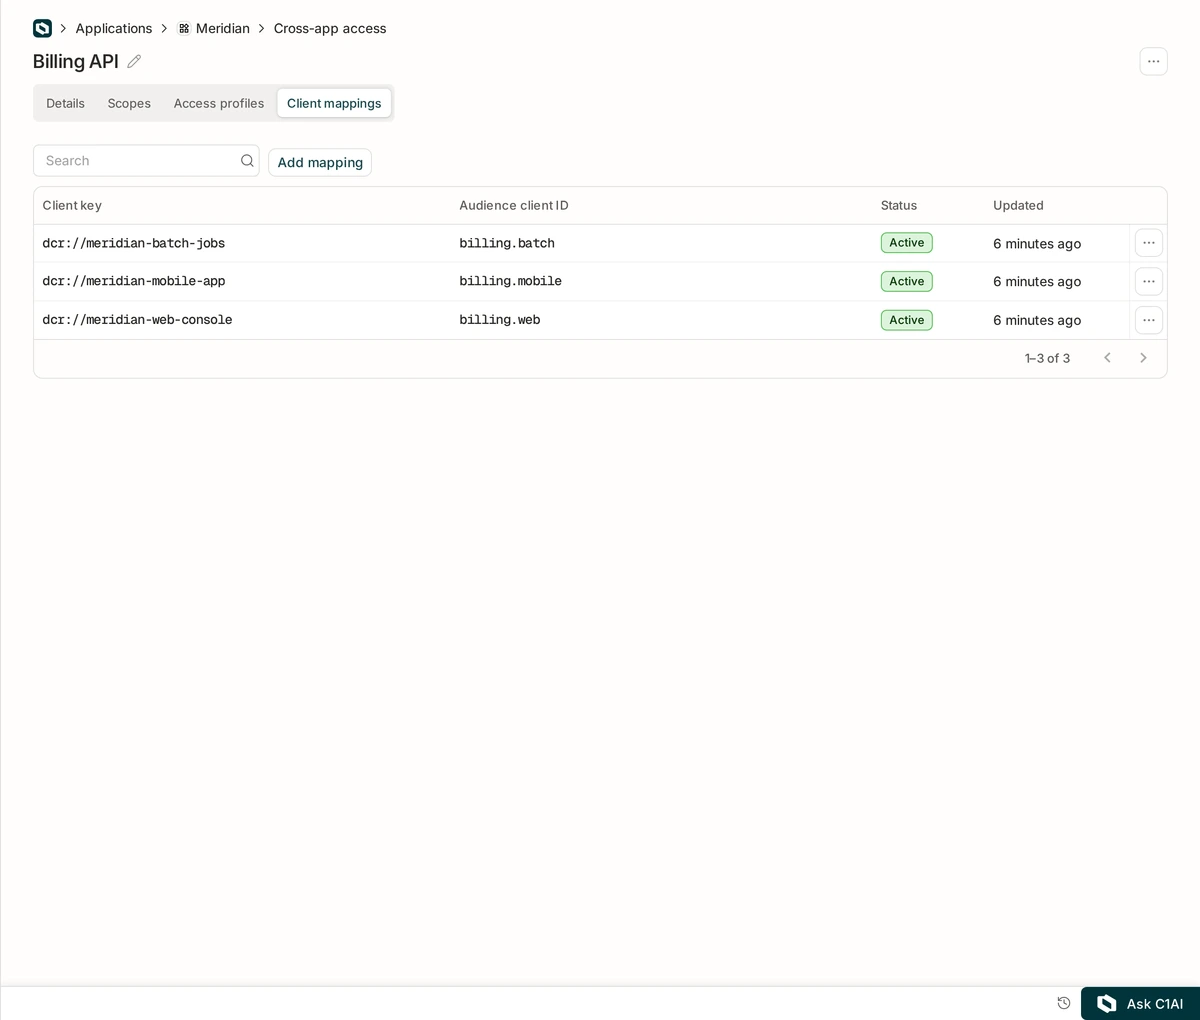
Tell C1 which resources your app cares about and map each one to an entitlement you already manage. That's the setup. No policy language to learn, nothing new to maintain.
400+ Identity connectors
Bring every identity and entitlement into one graph
How it works
Deploy prebuilt connectors for directories, HR systems, business applications, cloud platforms, databases, and private infrastructure.
3000+ MCP servers
Give agents governed access to enterprise tools
How it works
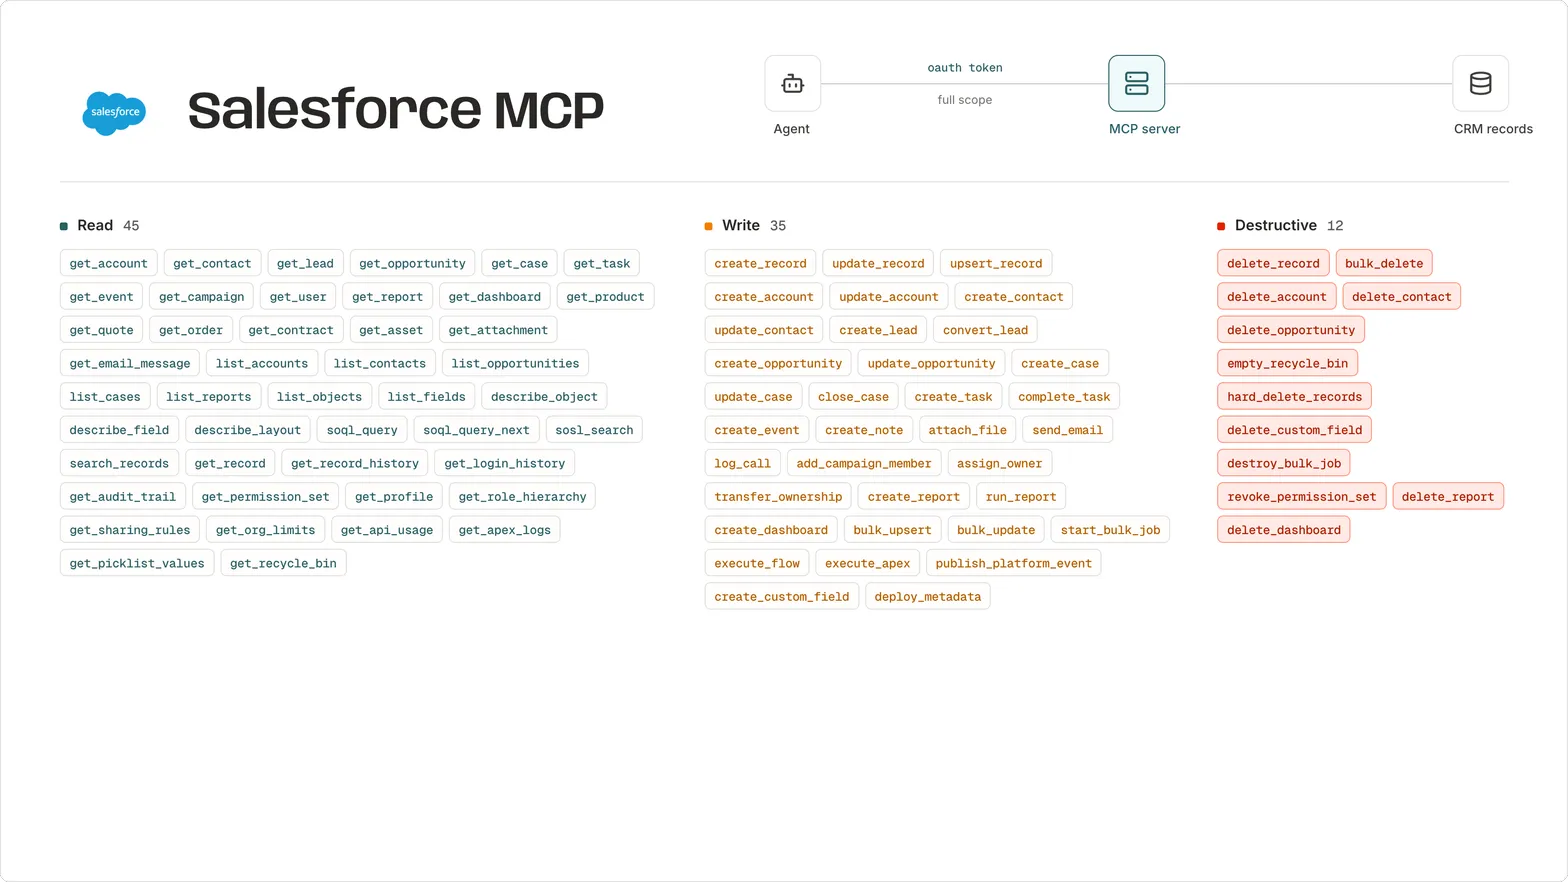
Select from the C1.ai catalog or register an MCP server directly, then discover its available tools and actions.
Extensibility and developer tooling
Build and operate C1.ai with the tools your engineers already use
How it works
Query identity data, integrate C1.ai into internal services, and invoke supported operations through the REST API and generated SDKs.