

TL;DR: The AI builder era has a credentials problem. In a C1 Academy video, C1.ai VP of Product Erik Huckle explains what happens to secrets when sales and marketing teams start building their own apps, and what the governed version looks like.
- The new reality: apps built across the business often start life "on a local machine as HTML files that either can't be shared or are never able to update."
- Sharing is ungoverned: once an app has a URL, there's no way to control who opens it, for how long, or who they pass it to.
- Credentials travel badly: plain-text API keys get texted back and forth; the fix is credentials that are time-boxed and expire.
- Sprawl needs pruning: apps that sit unused for months or years "need to be retired and put on the shelf," which takes activity tracking.
- The point of all of it: governance primitives that let teams "scale, move fast, and share and collaborate safely."
Picture the app your sales ops team built last month. It pulls from the CRM, cross-references the data warehouse, and saves everyone an hour a week. Now ask two questions about it: where does it live, and what credentials does it hold? The third video in C1 Academy's Building the Agentic Enterprise series is about how uncomfortable the honest answers usually are.
Why is the builder era a secrets problem?#
Because the building is real and the infrastructure underneath it isn't. Huckle describes what AI diffusion across the business actually looks like: sales teams building dashboards that track customers and pipeline, marketing teams writing one-pagers and deploying their own apps for conferences. "This is awesome for those companies," he says, "but it's creating its own host of problems."
The first problem is where the apps live: "a lot of these applications initially live on a local machine as HTML files that either can't be shared or are never able to update." The second arrives the moment one graduates to a link: "once you have a URL, you don't have any way to govern it." If a salesperson shares that URL with a company leader, there's no way to know "if it was the right person, how long they could access it, or who that person could share it with."
And underneath both sits the credentials problem, in exactly the form you'd fear: critical API keys "in plain text," or being texted back and forth between teammates. The key now lives wherever the app lives, works for whoever finds it, and expires never. It's the same credential sprawl Alex Bovee described as vibe coded applications "in all sorts of places," seen from the secrets side.
What does the governed version look like?#
Huckle's model, built on what C1.ai learned "from building and deploying our own apps internally," fixes the three problems in order.
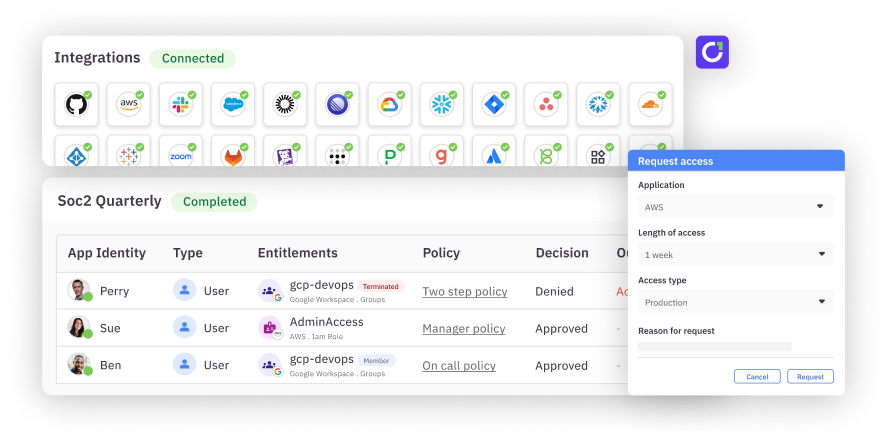
Access gets a front door. Instead of an app anyone with the link can open, SSO and authorization control who can open it, what they can access inside it, how long their access lasts, and who they're allowed to share it with. The app becomes shareable precisely because sharing it no longer means handing over its insides.
Credentials get an expiration date. In place of plain-text keys, "you can TTL these credentials, have them time-boxed and expire, and also let your admin manage those at scale." What leaks when something goes wrong is a credential that stopped working hours ago rather than a skeleton key. This is the pattern behind credential vending: the secret does its job without the builder, the app, or the agent holding it indefinitely.
The population gets pruned. Builders are going to be busy, and the inevitable byproduct is "applications that have sat unused for days, months, years. They need to be retired and put on the shelf." That only happens when something is watching, which is what activity tracking is for: builder-era sprawl is a cleanup problem as much as a creation problem.
Does this slow the builders down?#
It's designed not to, and Huckle's closing line names the goal: as AI diffuses across departments, companies need "the governance primitives that underpin all this to make sure you can scale, move fast, and share and collaborate safely." None of the three fixes asks the sales team to learn security; they ask the platform to supply it. C1.ai packages exactly that: C1 Vault for the secrets, C1 AppHub for governed deployment and sharing, and expiring access instead of forever-keys, so the fastest way to build is also the one your security team can live with.
The apps your teams are building aren't going away, and neither are the credentials inside them. The only real choice is whether those credentials expire by design or leak by accident.
Watch the full video on C1 Academy, then see how C1.ai handles secrets for the builder era.