C1.ai to join Workday. Read the announcement →C1.ai to join Workday. Read the announcement →
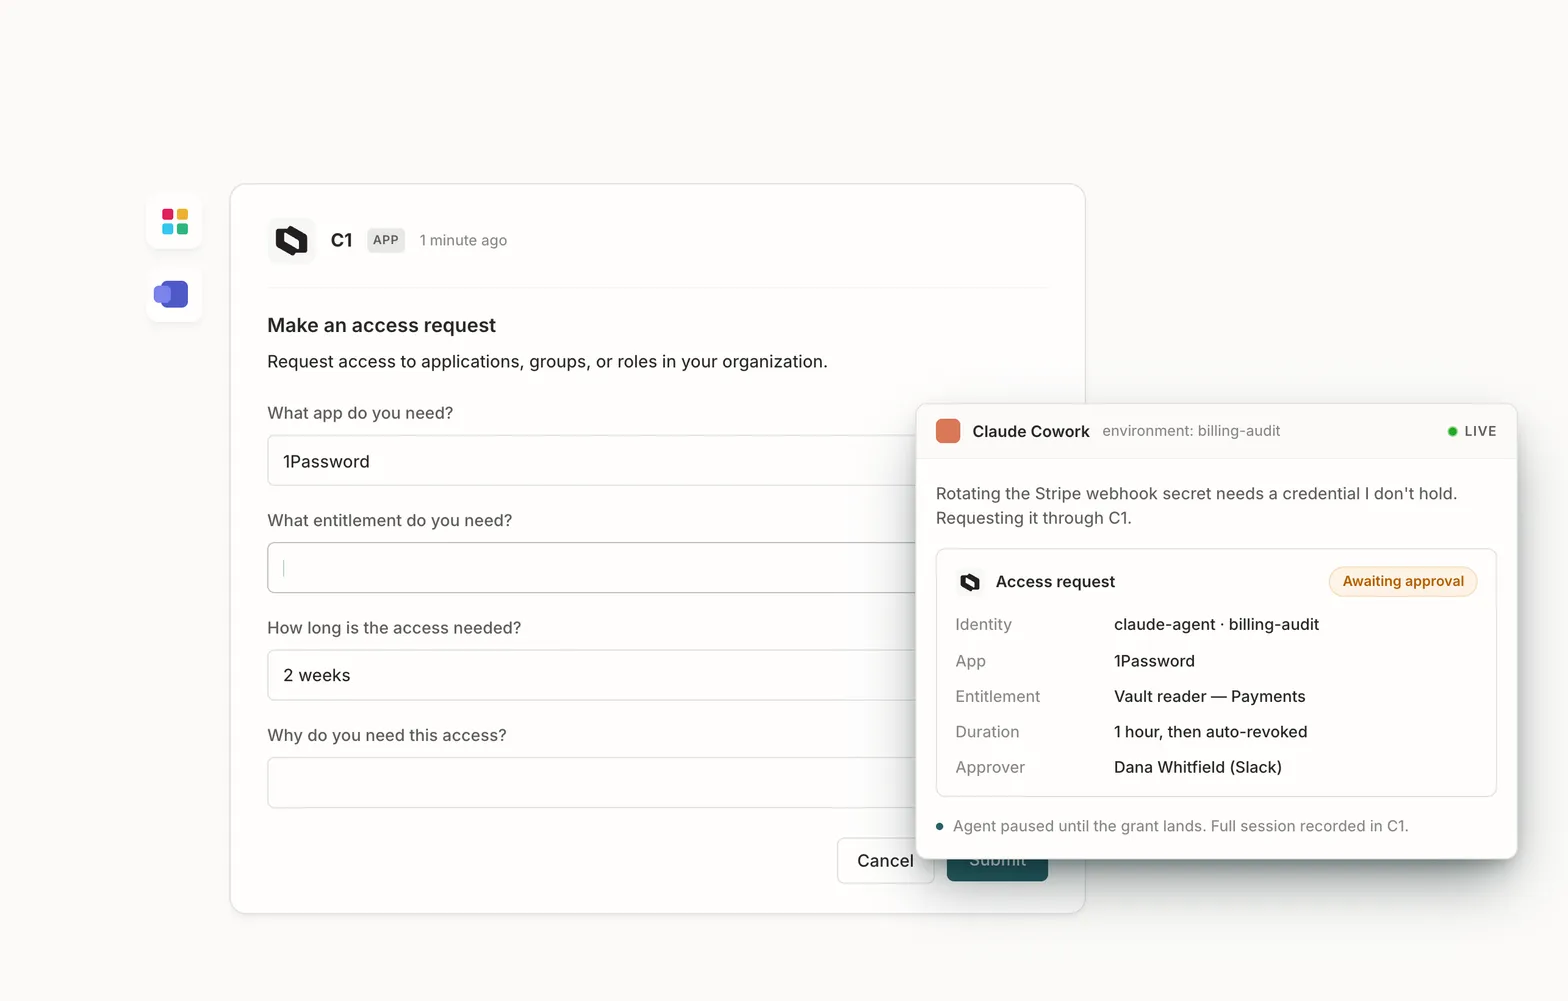
Let employees, contractors, workloads, and agents request access from the web, Slack, Teams, MCP, API, or CLI.
Evaluate identity, role, resource, and risk context to auto-approve routine access or route sensitive requests.
Expire just-in-time grants automatically and keep the request, decision, grant, and removal together.
Self-service requests, RBAC, and just-in-time access control in one policy-driven system.
Dynamic Access Controls
How it works
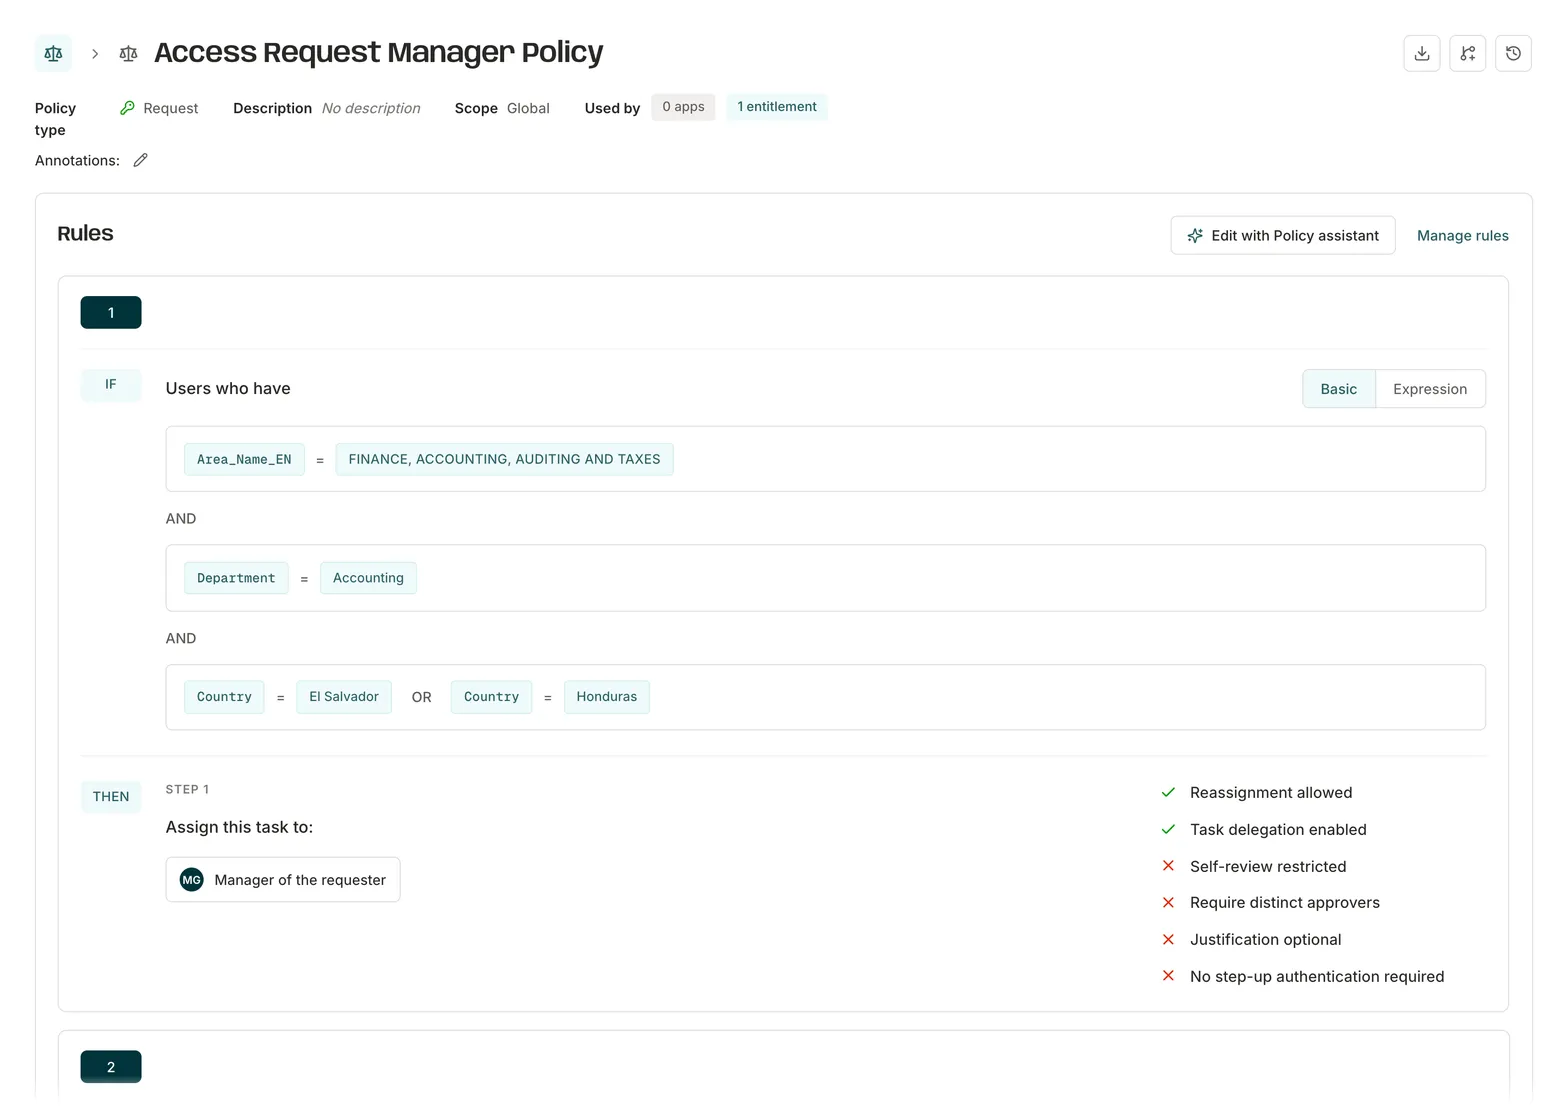
Conditional policies evaluate role, attribute, and risk context in real time to grant or revoke access automatically.

Self-Service Access
How it works
Accept requests from a catalog, Slack, Microsoft Teams, CLI, web, or an approved automation.
RBAC + Just-in-Time Access
How it works
Define role-based access around job function, team, attributes, and resource scope instead of rebuilding every grant by hand.
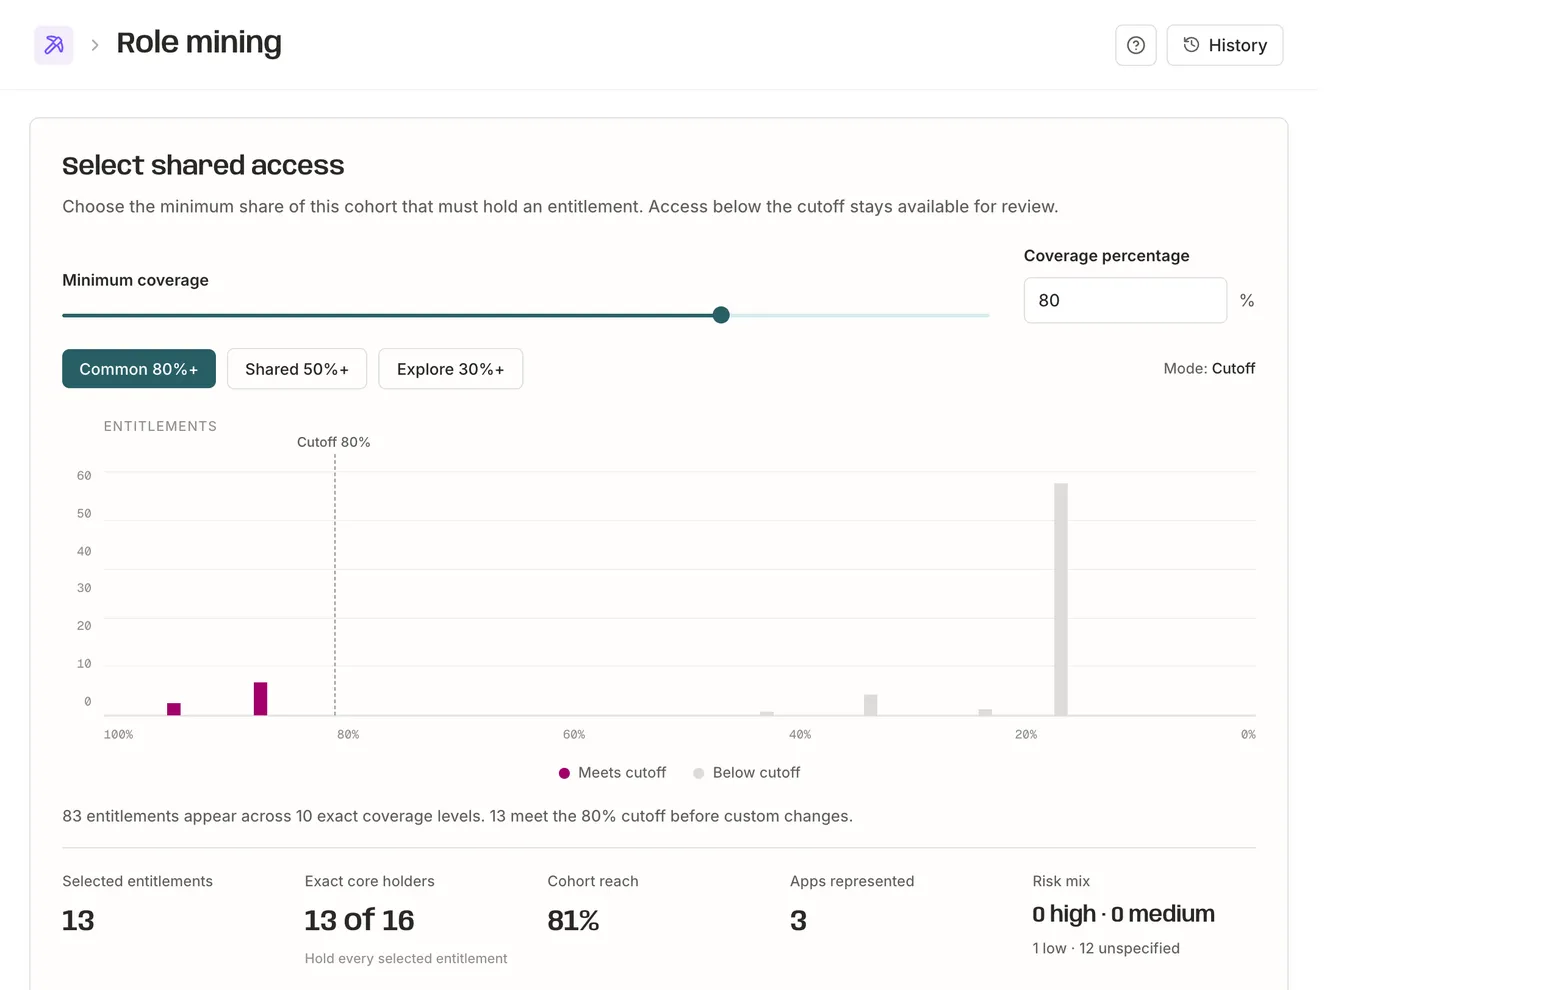
Role Mining
How it works
Filter by department, job title, manager, employment status, or other mapped workforce attributes to identify a specific group of people.