

C1.ai launches SSO and application permissions two of the building blocks organizations need to custom-fit business processes and apps using AI. Define who can sign in and what they can do once they get there. Second of four launches in C1 Launch Week.
SAN FRANCISCO — September 29, 2026 — Every AI-built application has to answer two questions: who are you and what are you allowed to do? C1.ai today launched governed sign-in and permissions for AI-built applications, so both answers come from the entitlements a company already governs in C1.ai instead of from a login page and an email list somebody wrote once.
The usual pattern is familiar to anyone who has inherited an app built with AI. A developer creates a sign-in screen, then hardcodes a list of email addresses or copies group membership into a local table where it quietly goes stale. Nobody updates either one. Neither tells a security team what changed, when, or why. And when the answer to a permission check is no, the application returns an error, the person files a ticket, and someone ships a code change to fix it. Multiply that by every app a team now builds with AI, and access sprawls faster than anyone can govern it.
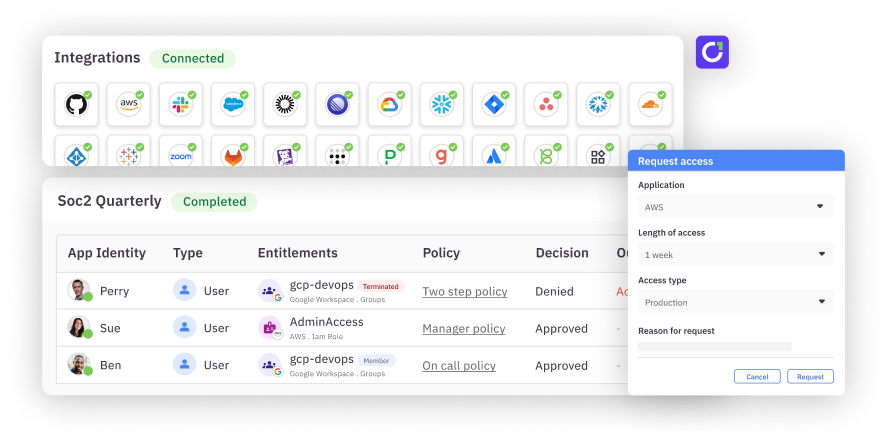
With C1 AppHub, which launched Sept. 28 as the first announcement of C1 Launch Week, that work goes away. Builders publish an app to AppHub, and C1.ai manages who can sign in and what they can do from the moment it goes live, the same way it already governs third-party applications. Access to each published app becomes a C1.ai entitlement, which means it is requested, approved, reviewed, and revoked in the same access reviews as everything else the company governs. Employees sign in with the credentials they already have, because C1.ai connects to the identity provider the company already runs, and builders never write a login page or a user table.
On permissions, applications call a live C1.ai endpoint built on OpenID AuthZEN, an open authorization standard, and ask whether a specific person may take a specific action. The answer comes from the same entitlement graph, so separation-of-duties rules, certification status, and risk checks that already apply to human access apply here too. Because the endpoint is standards-based, any AuthZEN-compliant client can call it.
What a team gets on day one:
- Ship the app, C1.ai manages the login. Your builders spend their time on what the application does, not on rebuilding sign-in and a user table for every new tool.
- Application access joins your standard reviews. Who may sign in to a given application shows up in the same access reviews as everything else you govern, and a revocation takes effect on the next request.
- Access becomes a request, not a ticket. A user requests access, the owner approves it, and the user retries. Separation of duties, certification, and risk checks all still apply.
This is the second piece of what your teams need to put AI to work, so you can focus on building what makes your business unique. C1.ai paves the road to the agentic enterprise. Monday gave your teams a governed place to build. Today decides who gets in and what they can reach once they are there.
“Teams shouldn’t have to rebuild identity and permissions every time they create an application,” said Alex Bovee, CEO and co-founder of C1.ai. “C1.ai gives every app a governed path to sign-in, authorization, and access requests without hardcoded lists or another system to maintain.”
Governed sign-in and permissions are available today. It is the second of four launches in C1 Launch Week, leading into C1 Transform in San Francisco on October 6. Book a demo at c1.ai.
About C1.ai
C1.ai is the identity platform for the AI era. Our platform connects humans and agents to enterprise systems with scoped access, enforced policies, human approval, and a record of every action. With C1.ai, the fastest path to AI adoption at scale is the governed path—giving organizations visibility and control without sacrificing security or slowing innovation. Companies such as Ramp, Zscaler, Qualtrics, and DoorDash trust C1.ai to govern identity, secure agents, and empower their teams to put AI to work. Learn more at c1.ai.
# # #
Media Contact