

FOR IMMEDIATE RELEASE
Apps published to C1.ai App Hub now get every credential they need from C1.ai, scoped, time-bound, and logged. C1 Egress substitutes the real secret at the network layer so the LLM never holds it. The launch builds on App Hub, introduced Sept. 28, and governed sign-in and permissions for App Hub apps, introduced Sept. 29. Third of four launches in C1 Launch Week.
SAN FRANCISCO — September 30, 2026 — The person who built your newest application may never have heard the phrase "hardcoded credential." C1.ai today launched credential vending and C1 Egress, a governed egress proxy, which together make the safe outcome the automatic one: applications get the access they need without ever holding the secret that grants it. This means eliminating hardcoded credentials and closing the revocation gap that turns a long-lived credential into a breach.
Applications need secrets to do anything useful, and the standard way to give them one is to paste it into a config file or an environment variable. From there it spreads. It lands in a repository, a container image, a screenshot, an agent's context window. Nobody can say what it can reach or when it was last used, and turning it off means finding every copy and redeploying the application. That was a manageable problem when a handful of engineers wrote every application. It is not manageable when anyone in the company can stand one up in an afternoon.
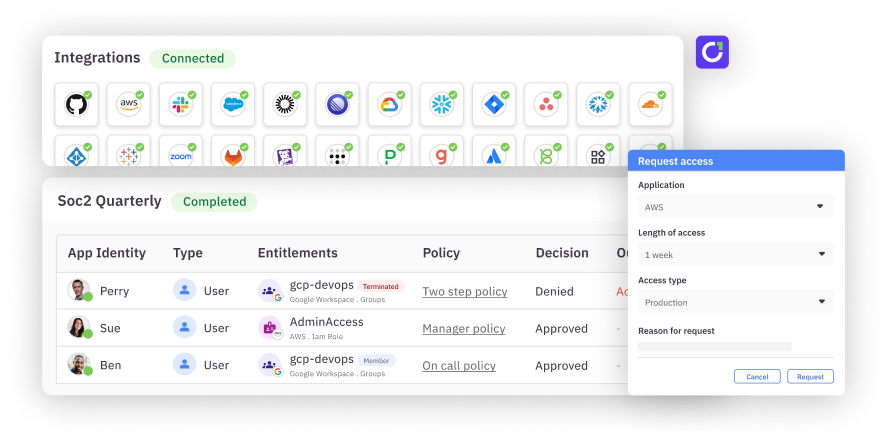
C1.ai issues the credential instead. Credentials come out scoped to a specific role and pinned to allowed IP ranges, delivered through a vault rather than handed to the application to keep. One inventory shows who minted each credential, what it can do, and when it was last used, and every mint, use, and revocation lands in an audit trail. Revoking a credential takes effect on the next call rather than the next deploy.
C1 Egress addresses the other half of the credential problem. It sits between an application and the outside world, and it substitutes the real credential only when the request is going somewhere policy allows. Requests to internal addresses and cloud metadata endpoints are blocked by default. Every call is logged with its source, destination, and decision, and the secret itself is never recorded. Because that enforcement happens outside the application, at the network layer, the control remains effective even if application code attempts to route around it.
What a team gets on day one:
- Safe by default, not by expertise. Someone who has never heard of a hardcoded credential gets the safe outcome automatically. The business carries less risk without asking every builder to become a security engineer.
- Revocation is immediate. Turning off a credential kills it on the next call, not on the next deploy, so an offboarding or incident-response action takes effect immediately.
- Nothing to steal. Inspect an agent's environment and there is no credential in it for an attacker to find, because the workload never had one.
This is the third piece of launch week, and it lets builders keep working on what helps your business grow while keeping data secure. When C1.ai mints the credential and the proxy holds it, the question stops being where the secrets are and becomes which systems this application is allowed to talk to, which is a question a company can actually answer, review, and change. That is what makes it safe to let a thousand applications reach real data.
"Builders should be able to connect an application to real systems without copying a credential into code or configuration," said Alex Bovee, CEO and co-founder of C1.ai. "We make the governed path the fastest path."
Credential vending and C1 Egress launch today. It is the third of four launches in C1 Launch Week, leading into C1 Transform in San Francisco on October 6. Book a demo at c1.ai.
About C1.ai#
C1.ai is the identity platform for the AI era. Our platform connects humans and agents to enterprise systems with scoped access, enforced policies, human approval, and a record of every action. With C1.ai, the fastest path to AI adoption at scale is the governed path—giving organizations visibility and control without sacrificing security or slowing innovation. Companies such as Ramp, Zscaler, Qualtrics, and DoorDash trust C1.ai to govern identity, secure agents, and empower their teams to put AI to work. Learn more at c1.ai.
Media Contact: press@c1.ai
###