
Secure sensitive resources with just-in-time access
Talk to our team to learn how to:
- ✅Grant engineers temporary elevated access to specific roles, groups, or resources
- ✅Move away from standing privileges for cloud and on-prem infrastructure
- ✅Configure JIT policies (including break-glass and on-call) and track all access changes from one control plane
See how it works
Trusted by IT and Security @




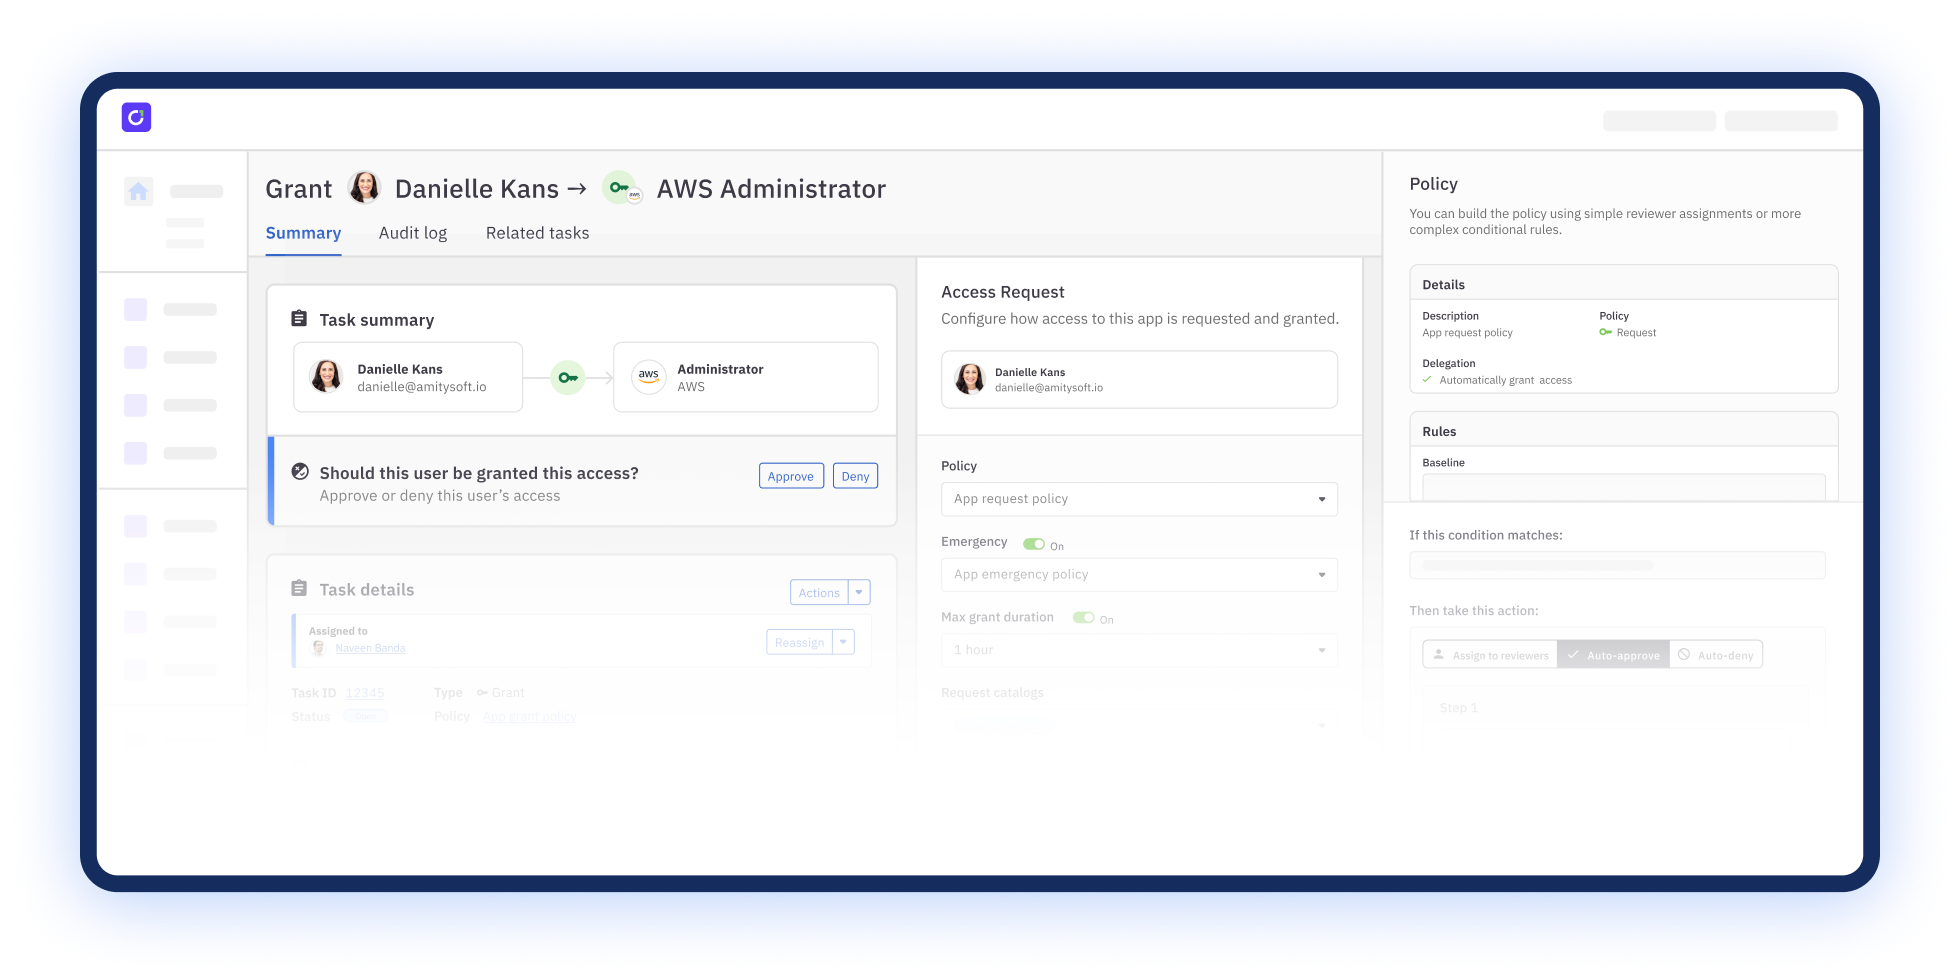
Secure all your apps
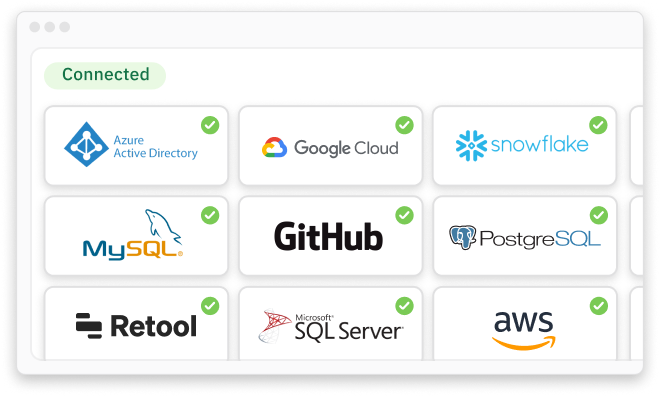
Connect all your cloud and on-prem systems, including private apps and infrastructure, for fine-grained control of access.
Make security the default
Move to just-in-time access with user-friendly self-service requests and no-touch provisioning.
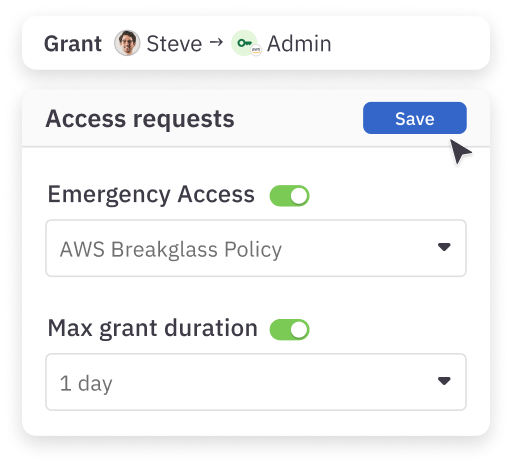
Configure policy-driven access controls
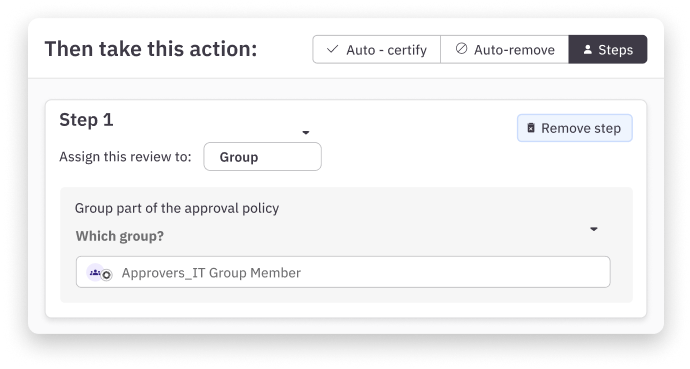
Create zero-touch, conditional, and multi-step approval policies and workflows that meet your security needs.
Integrations

Cloud
Integrate with your cloud infrastructure, SaaS, directories, data warehouses, and HR systems.


Infrastructure
Connect to your your non-cloud infrastructure, including LDAP, Postgres, Microsoft SQL, and more.


On-prem
Secure your on-premises technology such as Active Directory and homegrown and back-office apps.

Learn how security, IT, and GRC teams use C1 to be more secure and productive
95%
reduction in effort to process access requests
150+
hours saved on access request tickets every month
<1month
average time to go live


